Active Directory
SailPoint Entro connects to your on-premises Active Directory to discover, monitor, and analyze user identities, groups, computers, and permissions.
Purpose
This integration ingests Active Directory objects and ACLs to find identity risk, excessive permissions, and lateral movement paths.
Supported Environments
-
On-premises Active Directory forests, single or multi-domain. A multi-domain forest needs a reachable Global Catalog.
-
Hybrid environments, as long as the Worker Group (connector) can reach a domain controller.
-
Each forest is onboarded separately. Trusts to other forests are recorded, but those forests' objects are not collected, and the connector never sends them the service account's credentials.
Architecture
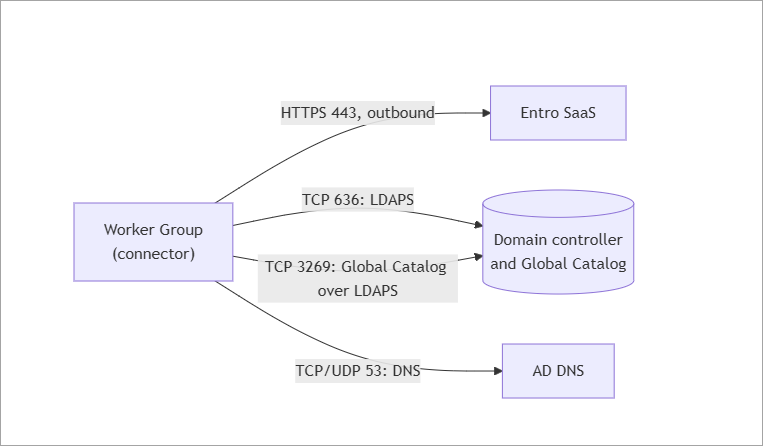
The connector reaches one domain controller. Pick one that is also a Global Catalog, and the firewall needs only TCP 636 and 3269 to that host. Refer to the Active Directory Onboarding Guide for the full network requirements.
What Entro Collects
-
Users: identity attributes, account state and risk flags (disabled, password not required, Kerberos pre-authentication not required, delegation), last logon, password age, SPNs, and privileged status (adminCount).
-
Groups and nested membership, including primary groups and very large groups.
-
Computers: host name, operating system, SPNs, and delegation.
-
Domains in the forest, and their trust relationships.
-
ACLs (owner, group, and DACL), turned into permission edges such as GenericAll, WriteDACL, AddMember, ForceChangePassword, and ReadLAPSPassword.
SailPoint Entro does not collect passwords or hashes, LAPS, BitLocker or gMSA secrets, SACLs, GPOs, or password policies.
Authentication and Access
-
A dedicated service account, a member of Domain Users only, signs in with a simple LDAP bind over TLS: LDAPS on 636, or StartTLS. The connector never falls back to plain-text LDAP.
-
SailPoint Entro makes read-only LDAP queries from the Worker Group (connector).
-
TLS trust comes from the DC's LDAPS certificate and the root CA that issued it, which you paste into SailPoint Entro.
Getting Started
-
Active Directory Onboarding Guide: network, service account, certificate, validation, and the Console fields.
-
Troubleshooting and Validation: what each error means and how to fix it.
Security & Compliance
-
TLS 1.2+ for every connection. The service account's password is never sent in cleartext.
-
SailPoint Entro uses read-only directory access.
-
Stored credentials are encrypted using AES-256.
-
Applicable standards: SOC 2 Type II, ISO 27001, GDPR (data retention and export controls apply).