Prerequisites for AWS
To use the Data Access Security AWS connector, you must have sufficient permissions in AWS to configure AWS manually.
Best Practice
Verify the Identity Collector associated to this application has completed an aggregation initiated from Data Access Security by navigating to Admin > Identity Collector > locate IC > Actions > Run Aggregation. This ensures all permissions will be mapped properly to SailPoint Human Fabric identities.
You can create the required AWS resources in one of two ways:
- Configuring AWS automatically (recommended) – use the SailPoint CloudFormation templates to create the IAM user, access keys, policies, and roles.
- Configuring AWS manually – create the IAM user, policies, and roles in the AWS IAM console.
Both methods create the same AWS resources. Use only one method per AWS account.
Configuring AWS Automatically
SailPoint provides AWS CloudFormation templates to automate the creation of the IAM user, access keys, policies, and roles required by the Data Access Security AWS connector.
Deploy the templates in two steps:
- Use a stack to configure the primary (management) account.
- Use a stack set to configure every other account the connector should analyze.
Important
Deploy the templates in a single region. IAM resources are account-level objects and should not be created per region.
Configuring the Primary Account
The primary account is the AWS management account that holds the dedicated Data Access Security IAM user.
- Sign in to your organization’s management account.
- Download the DAS_AWS_S3_Stack.json.
- Follow the AWS directions to create a stack, choosing With new resources (standard), and upload the template.
-
Enter the stack parameters:
- DasUserName - Name of the dedicated IAM user for Data Access Security. Default: SailPoint_DAS_User
- TargetRoleName - Name of the role Data Access Security assumes. Do not change this value.
Important
The role name
SailPoint_DataAccessSecurityRolecannot be changed. Data Access Security cannot connect to accounts that use a different role name. -
Select I acknowledge that AWS CloudFormation might create IAM resources with custom names, then create the stack.
- When the stack completes, open the Outputs tab and save the AccessKeyId and SecretAccessKey values.
Important
Save the access key and secret key in a secure place. You will need to enter them in the connection details when you add the AWS S3 application.
This stack creates the dedicated IAM user with programmatic access, the assume-role policy, and the SailPoint_DataAccessSecurityRole role with read-only permissions in the primary account.
Configuring the Remaining Accounts
Use a stack set to create the role and read-only policy in each additional account the connector should analyze.
Caution
Do not include the primary account in the stack set. The role and policy already exist from the stack, and the deployment will fail.
- Download the DAS_AWS_S3_StackSet.json.
- From the management account, follow the AWS directions to create a stack set with service-managed permissions, and upload the template.
-
Enter the stack parameters:
- PrimaryAccountId - The 12-digit AWS account ID of the primary account where the Data Access Security IAM user was created.
- DasUserName - The name of the IAM user created in the primary account. This must match the DasUserName value used in the stack.
-
Under Deployment regions, select a single region.
- Select the organizational units or accounts the connector should analyze, then create the stack set.
This creates the SailPoint_DataAccessSecurityRole role and the SailPoint_DataAccessSecurity_S3IAMReadOnlyAccessPolicy policy in each target account, and allows the Data Access Security user in the primary account to assume that role.
Note
If your accounts are not managed by AWS organizations, you can deploy DAS_AWS_S3_StackSet.json as a standard stack in each account instead.
You can now add a new AWS S3 application in Data Access Security using the access key and secret key from the stack outputs.
Configuring AWS Manually
If you do not use the CloudFormation templates, create the IAM user, policies, and roles manually.
To configure the connector, you will create dedicated IAM users with the policies and roles needed to allow Data Access Security to access your AWS objects.
-
Sign into your organization’s management account.
-
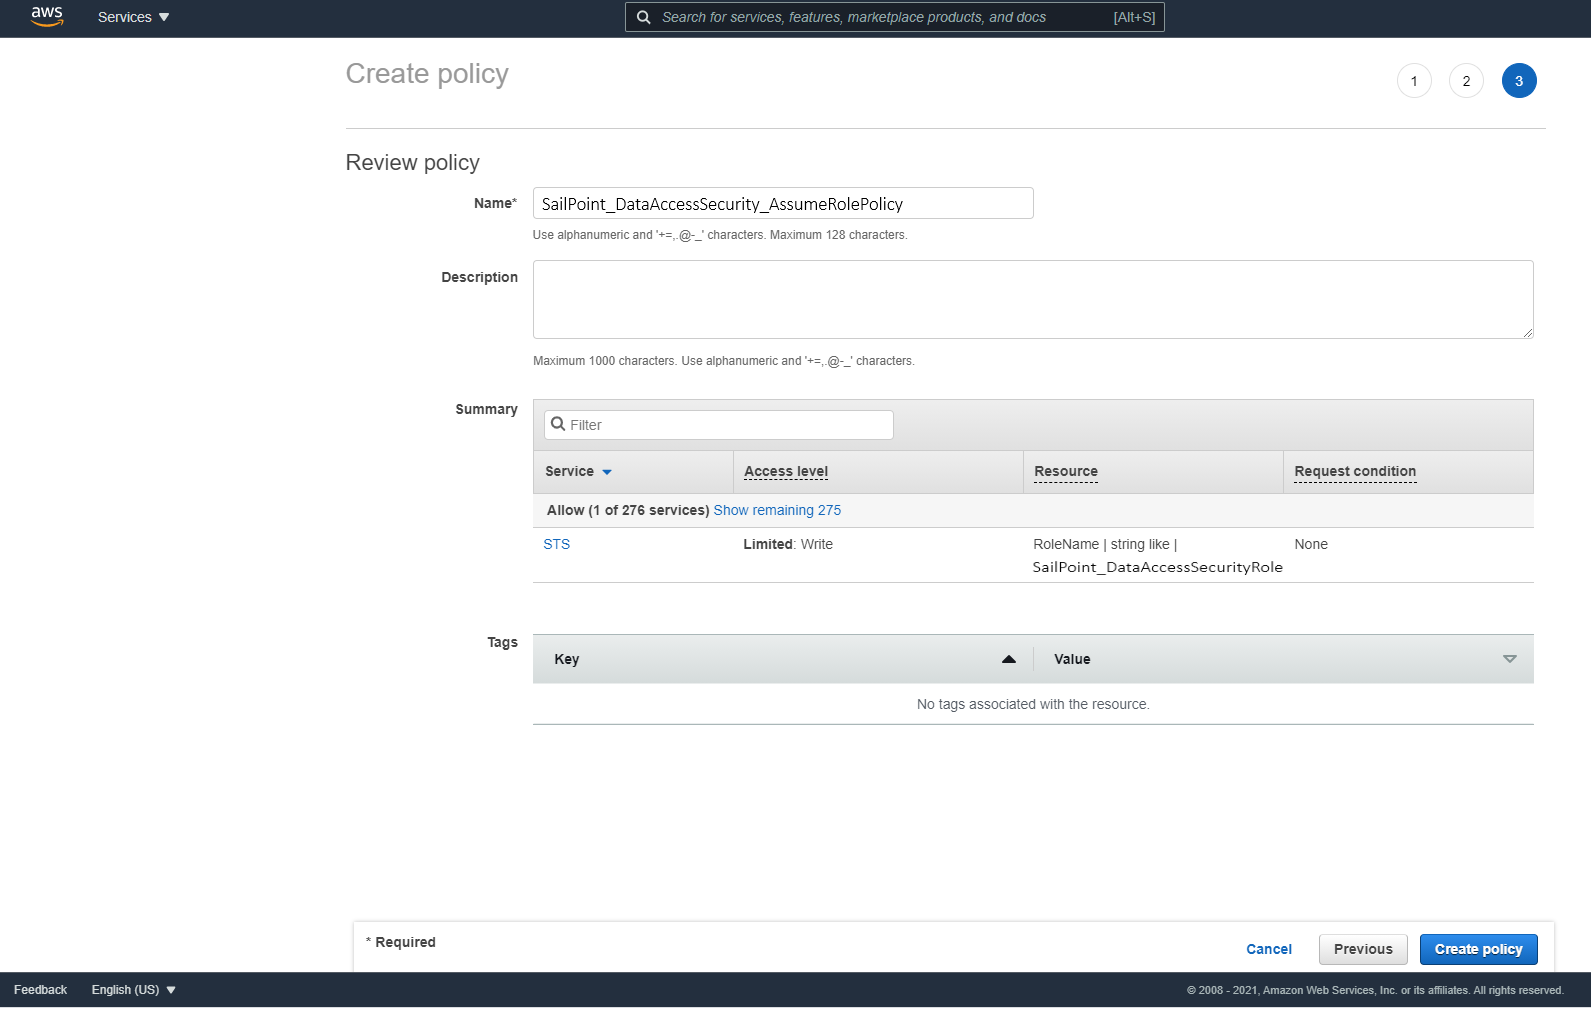
Use the SailPoint_DataAccessSecurity_AssumeRolePolicy.json script to create a policy titled "DataAccessSecurity_AssumeRolePolicy” so the Data Access Security user created in the next step can assume the roles created in each account.
-
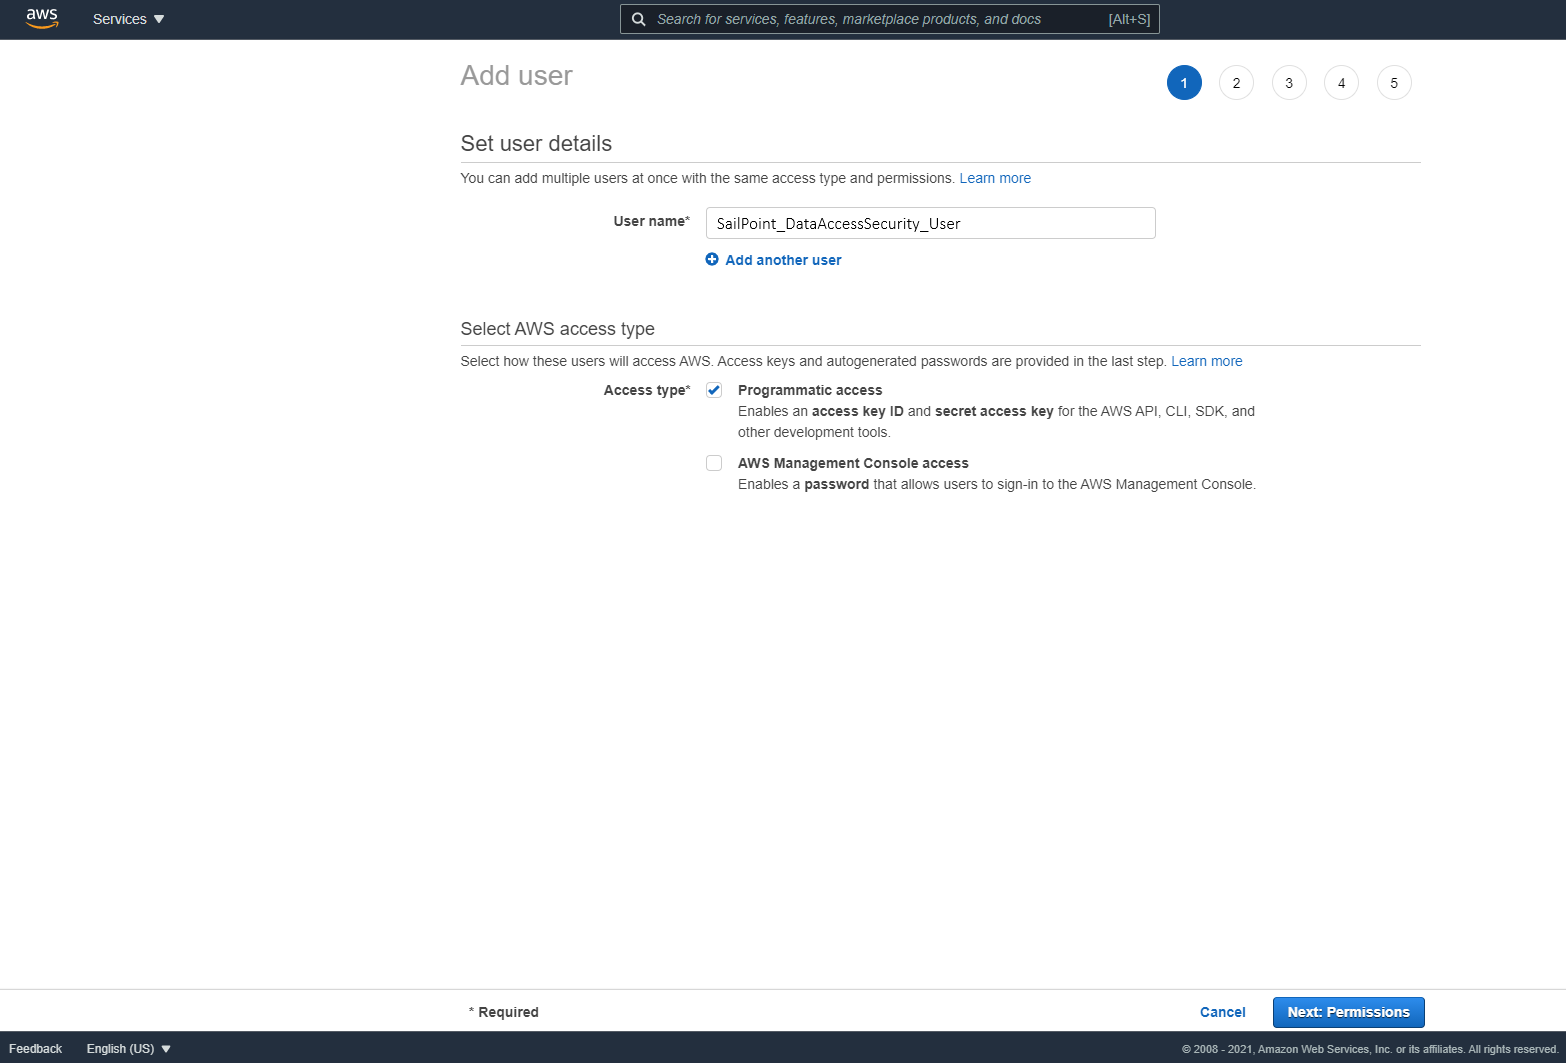
Create an IAM User for Data Access Security and select Programmatic access. This access requires an access key and secret key.
-
Attach the "SailPoint_DataAccessSecurity_AssumeRolePolicy" policy created above to the new user.
Important
Save the generated Access Key and Secret Key in a secure place.
-
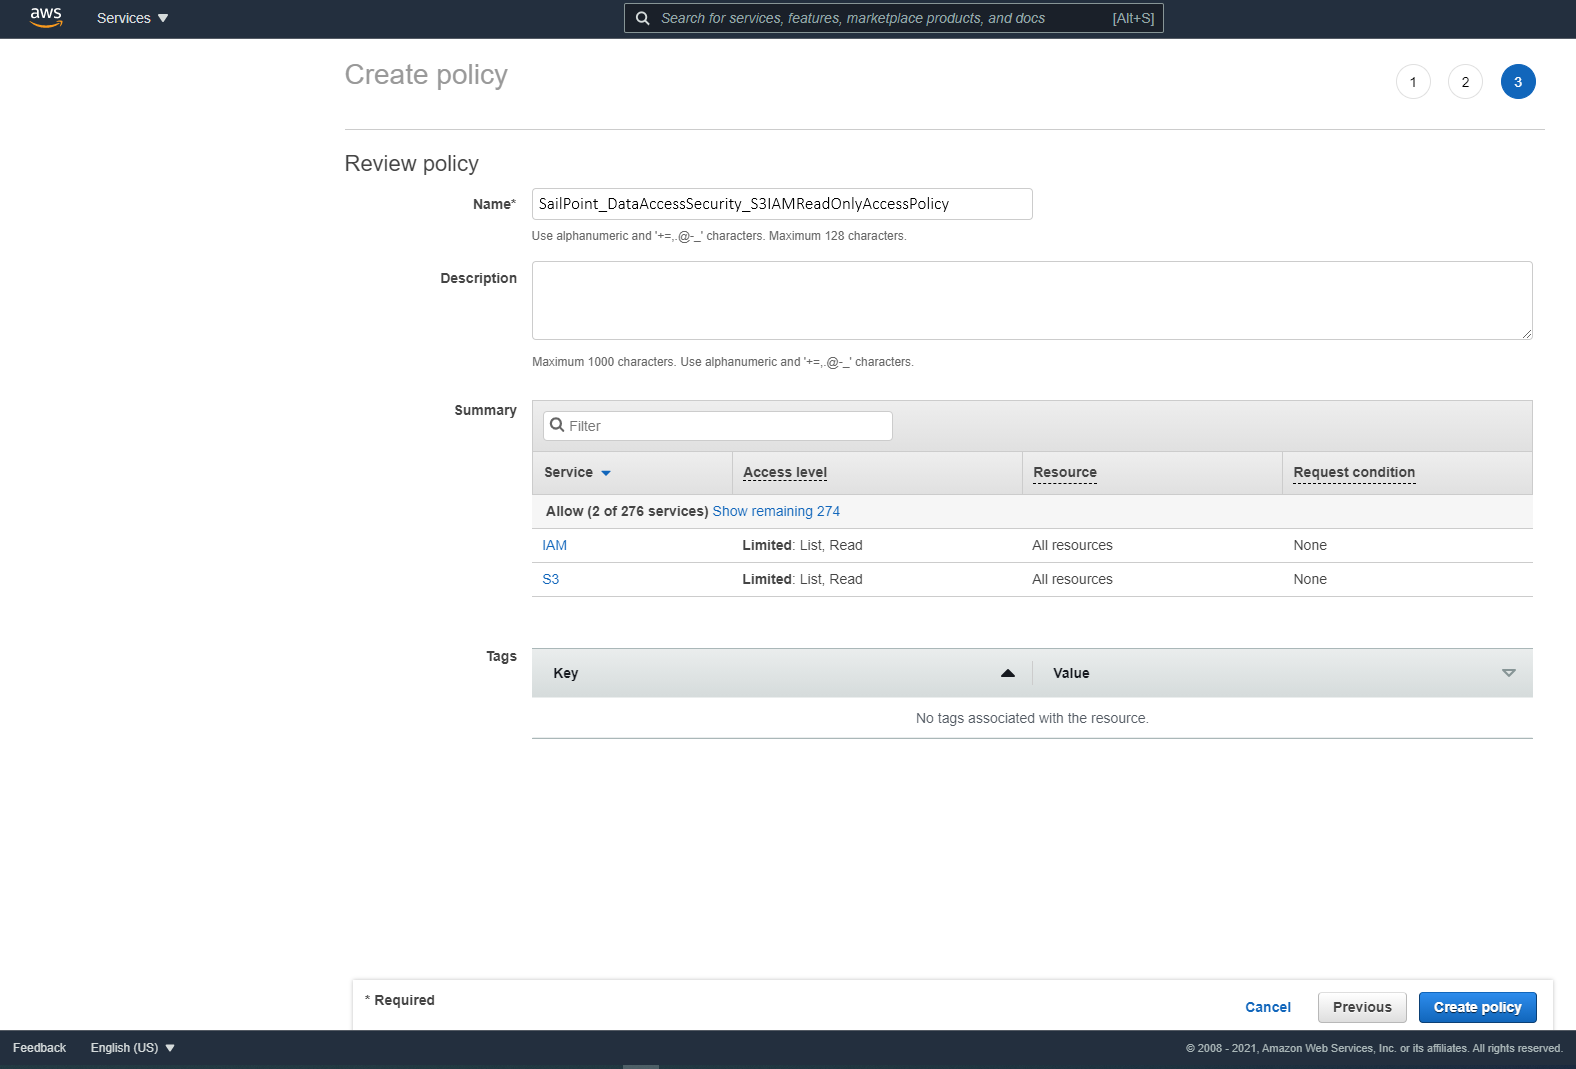
On each organization account the connector should analyze, including the management account, use the SailPoint_DataAccessSecurity_S3IAMReadOnlyAccessPolicy.json script to create a policy titled “SailPoint_DataAccessSecurity_S3IAMReadOnlyAccessPolicy” with the required permissions for the connector.
-
Create a new role titled “SailPoint_DataAccessSecurityRole”, which the Data Access Security user will assume on each organization account the connector should analyze. Select Another AWS Account to enter the user account ID.
-
Attach the "SailPoint_DataAccessSecurity_S3IAMReadOnlyAccessPolicy" policy you created above.
-
Enter the role name SailPoint_DataAccessSecurityRole.
Important
This name cannot be changed.
-
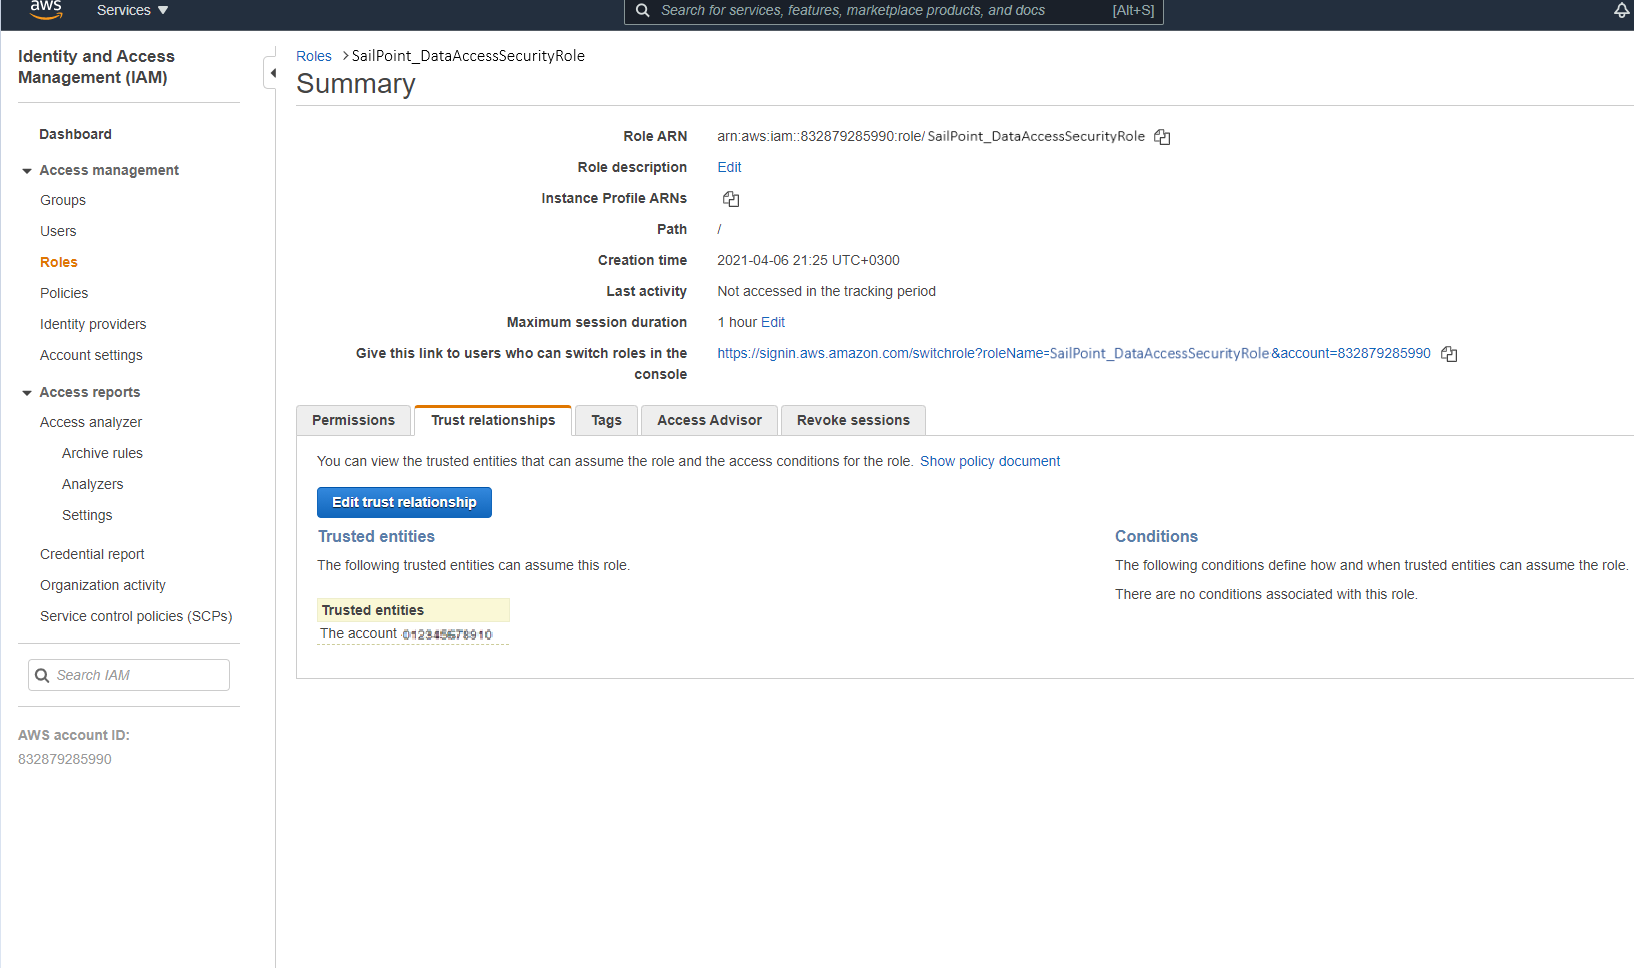
Edit the trust relationship of the new role.
-
Edit the JSON file.
Use the DataAccessSecurity.json (Dedicated User) script and replace
rootin the Principal section withuser/{DAS IAM User username}whereDAS IAM User usernameis the user created above.
Appendix: AWS JSON Scripts
Copy or download the following scripts to create the roles and policies required to connect AWS and Data Access Security.
Important
Do not change the file names.
Assume Role Policy
Download or copy the SailPoint_DataAccessSecurity_AssumeRolePolicy.json to create a policy defining the roles the IAM user can assume in each account.
S3 IAM Read-Only Access Policy
Download or copy the SailPoint_DataAccessSecurity_S3IAMReadOnlyAccessPolicy.json to create a policy with read-only access to your S3 objects.
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Effect": "Allow",
            "Action": [
                "s3:ListAllMyBuckets",
                "s3:ListBucket",
                "s3:GetBucketAcl",
                "s3:GetBucketLocation",
                "s3:GetBucketPolicy",
                "s3:GetBucketPolicyStatus",
                "s3:GetBucketPublicAccessBlock",
                "s3:GetAccountPublicAccessBlock",
                "s3:GetObject",
                "s3:GetObjectAcl",
                "iam:ListAttachedGroupPolicies",
                "iam:ListAttachedRolePolicies",
                "iam:ListAttachedUserPolicies",
                "iam:ListGroupPolicies",
                "iam:ListGroups",
                "iam:ListPolicies",
                "iam:ListPolicyVersions",
                "iam:ListRolePolicies",
                "iam:ListRoles",
                "iam:ListUserPolicies",
                "iam:ListUsers",
                "iam:GetGroup",
                "iam:GetGroupPolicy",
                "iam:GetPolicy",
                "iam:GetPolicyVersion",
                "iam:GetRolePolicy",
                "iam:GetUserPolicy",
                "organizations:ListAccountsForParent",
                "organizations:ListRoots",
                "organizations:ListAccounts",
                "organizations:ListOrganizationalUnitsForParent",
                "organizations:DescribeAccount",
                "ec2:DescribeRegions"
            ],
            "Resource": "*"
        }
    ]
}
Dedicated IAM User-Creation Policy
Download or copy the DataAccessSecurity.json (Dedicated User) script to set the dedicated IAM user who can use the roles and policies you've configured.
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.