Configuring Other Parameters
There are other important parameters in addition to the connection parameters for the ServiceNow admin to configure.
-
Enter the SailPoint attribute to correlate with ServiceNow account. For example,
nameoraccountId. To help ensure successful attribute correlation, you must use the exact name for the attribute as it appears in SailPoint in parenthesis (not the "friendly name" that’s displayed for the identity profile) and you must prefix any second level or custom fields withattributes.Note
An understanding of the data model used to organize your data in SailPoint will help ensure you specify the correct value. Refer to the table of attributes in Second-level Fields for Identities for more information.
- Enter the ServiceNow Account attribute to correlate with the SailPoint Identity Cube. For example,
user_name.
Note
The values of attributes being correlated as a result of mapping a SailPoint attribute and a ServiceNow account attribute are treated as case-insensitive.
- Select your choice from Approval Flow.
The integration relies on ServiceNow Manager approvals before it can create access requests in SailPoint.
- To use a SailPoint approval workflow instead, select
None. - To use only ServiceNow as a manager in ServiceNow, use
Manager Approval(Option included to maintain compatibility to earlier versions, soon to be deprecated). - To use the easy to configure and native ServiceNow approvals, use
Configurable Approvalsfrom the Approval Flow list. For more information, refer to Configuring Approval Flow.
- Enter the ServiceNow Account attribute to correlate with the SailPoint Identity Cube. For example,
-
Select your choice for Generic Approval Definition Enabled (applicable if Configurable Approvals is selected for Approval Flow). For more information, refer to Generic Approval Definition.
-
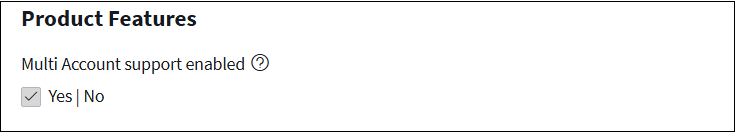
Select your choice for Multi Account support enabled. Set the “Multi Account support enabled” property to “Yes” to activate the feature. For more information, refer to Configuring Multi Account.
Screenshot
- Set the configuration for the Default comments for requested items. Keep it blank to impose comment configuration of SailPoint. For more information, refer to Configuration of the Comments Field.
- Select your choice for Is Sunset Date Mandatory for Access Requests? For more information, refer to Configuration of the Sunset Date Field.
- Select your choice for Skip user selection screen for users who can request access for self only. If the user will select access only for themselves, leave the default value as
Yes. This bypasses the user selection screen and redirects them to the sign in page. If the user needs to be able to request access for others, change the value toNo. This requires the user to select a user before it redirects them to the sign in page. -
Enter page URL to redirect after submission (Default: Service Portal page). This is where you want your user to be redirected after successfully creating a new ServiceNow Access request. For example,
-
You can leave the field empty to redirect the user to the default Service Portal page.
- You can specify a relative path that starts with / to redirect the user to that page. For example, to send a user to the Manage Access page use
/sp?id=manage_access. -
You can enter a URL with an absolute path to a page or site. For example,
https://www.sailpoint.com/10. Enter a user-friendly Header that will be displayed in the sidebar. For example,SailPoint Identity Security Cloud for Service Catalog. 11. Select your choice for Show Header text box?
Instructional text in the remaining customizable header fields will be applicable based on your choice:
- User Header text
- Add Access Header text
- Recommendations Header text
- Remove Access Header text
-
Review & Submit Header text.
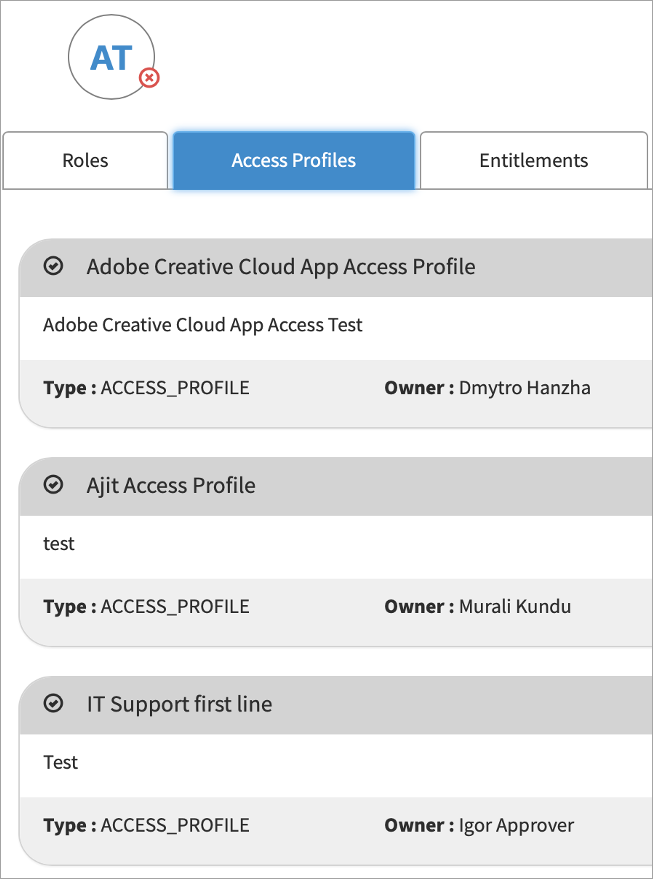
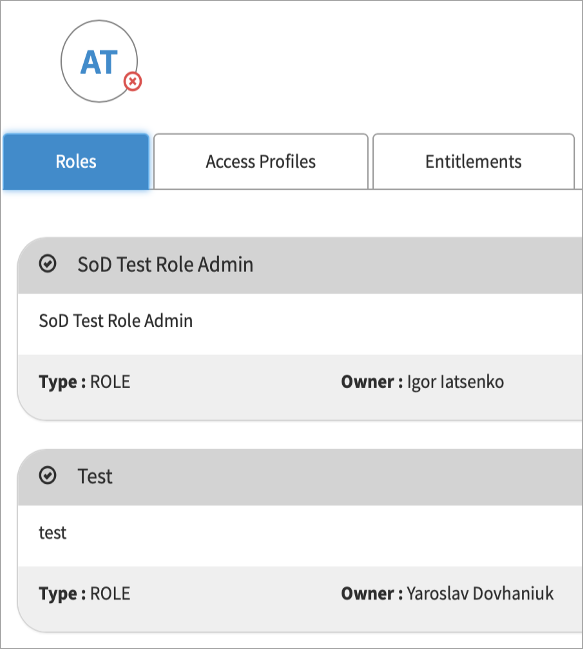
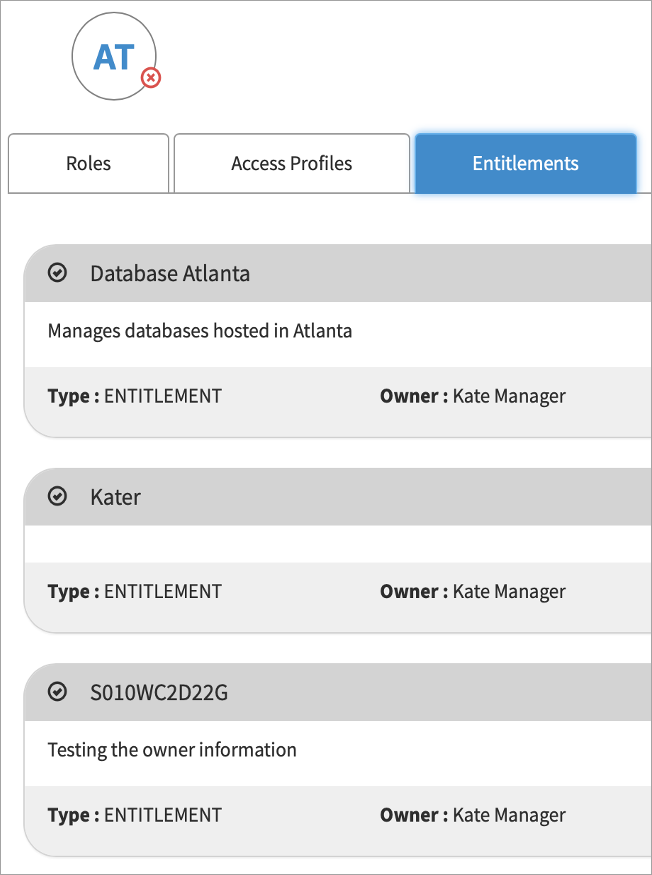
For more information, refer to Configuring Page Headers. 12. Select whether you want to Display Non-Requestable Access Objects or not. 13. Set the configuration for List and order of Search results tab. Exact text separated by comma to be used. (For manage_access page and Native search only) For more information refer to Configuring the Search Results Tab 14. Enter additional query conditions for Additional query for fetching list of access profiles, Additional query for fetching list of roles, and Additional query for fetching list of entitlements. Through these, the admin user can filter Roles, Access Profiles and Entitlements using any attribute the access object has. Only those filtered values will be available for end users. By default, these fields are empty.
Examples of a query condition
Screenshot

Screenshot
Screenshot
Screenshot
Note
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
- Enter the number of search results in Count of displayed access profiles/roles/entitlements on one page (Max 250)
Screenshot
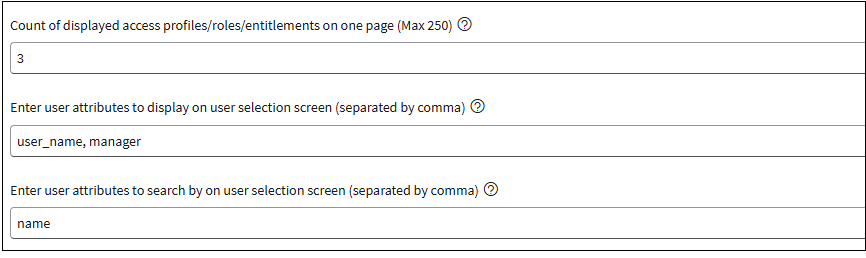
- Enter user attributes to display on user selection screen (separated by comma).These are the attributes you want to make available on the users search page. Use field names from the
sys_user tableseparated by a comma.
Note
For both SailPoint Access Request 2 and ISC Request Sample 2 widgets, ensure that the attributes configured under Display Fields exactly match the field names available in the
sys_usertable. Configure only those attributes that exist as valid fields in thesys_usertable. -
Enter user attributes to search by on user selection screen (separated by a comma). These are the attributes you want to use for the users search page. Use fields names from the
sys_user tableseparated by a comma. -
Select how you want to manage Separation of Duties policy checks for the selected users before a new access request can be raised. For example,
- Disabled (default) - There is no Separation of Duties violation check for the selected users.
- Soft: allow submission - The Separation of Duties violation check is applied for all the selected users. If there is a violation, a warning message is displayed and the request can be submitted.
- Hard: reject submission - The Separation of Duties violation check is applied for all the selected users. If there is a violation, an error message is displayed and the request cannot be submitted.
-
To show the recommendations tab, select
Yesfor Show Recommendations, applicable only if required license available This property is applicable only if a required license is available. - Specify the field name that will be used to store the access request ID from SailPoint. This field name is used to link tickets created by
SailPoint Identity Security Cloud for ServiceNow Catalogwith those created for the same request bySailPoint for Service Desk. This property is applicable only if you have both theSailPoint Identity Security Cloud for Service CatalogandSailPoint for Service Deskstore applications installed on the same ServiceNow instance. The default value iscorrelation_id. You can change it to another custom field if you are already usingcorrelation_idon requested item for other integration. For more information, refer to Linking with the SailPoint for Service Desk Application. -
Specify the value for status check timer activity in minutes. Default value is 1440 minutes which is 24 hours The default configuration for the workflow involves pooling statuses from SailPoint once every 24 hours. However, this can be adjusted to align with specific business requirements using the provided property.
Important
Exercise caution when adjusting this value, as setting it too low may lead to requests being canceled. Recommended value: no less than 720.
Note
For app version 3.1.0 and earlier, the required steps are outlined in Configure Status Pooling Timer.
- The Auto Approve Enabled field is applicable to customers with app version 3.2.0 and later. The default setting is
No. IfYesis selected, the approval request will be auto-approved if theapproverandrequester/requested forare the same user.
Note
- This property applies exclusively to the rule types of
ServiceNow User,ServiceNow Manager,Identity Security Cloud OwnerandIdentity Security Cloud Manager. - The property does not apply to
ServiceNow Workflow,ServiceNow Flow, andIdentity Security Cloud Workflow.
- The Auto Approve Enabled field is applicable to customers with app version 3.2.0 and later. The default setting is
-
The Property to determine which logs to print. Choices are debug, info, warn and error. Default is warn is used to determine the level of logging. For more information, refer to Debug and Error Handlers.
- The Native Search Redirect Page ID (example: manage_access) setting is useful if Native Search is implemented. For more information, refer to Configuring Native Search.
- Select Save.
Application Level Configuration
Refer to Application Level Configuration for more information.
Employee Service Center Portal Configuration
The Manage Access request page can now also be included with the Employee Service Center portal.
Note
SailPoint has configured and supports only the ServiceNow out-of-the-box Employee Center (EC) theme of the Employee Service Center (ESC). Issues related to custom changes to the EC theme or other themes are not supported.
Creating a Quick Link Record
A quick link to the Manage Access page must be manually configured in the Employee Service Center because this is not an automatic process during app installation.
Note
The process outlined may vary based on your configuration.
- Sign in as an administrator, and change the application scope to Global.
-
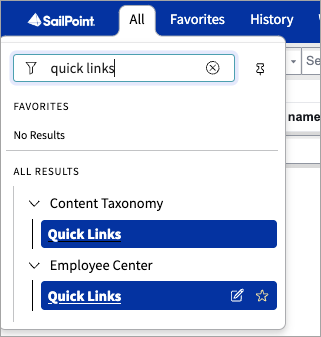
Go to the application navigator, enter
Quick Linksin the filter navigator, and open the Employee CenterQuick Linksmenu.Screenshot
-
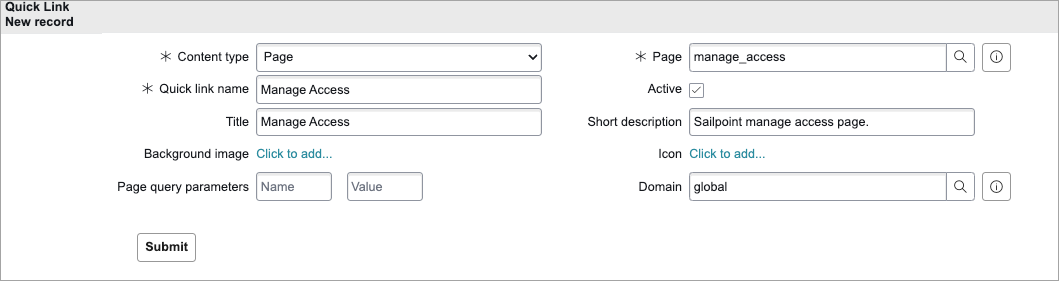
Select New, and enter the following details:
- Content type - Page
- Page - manage_access
- Provide a Quick link name and Title.
- Ensure it is marked as Active.
-
(Optional) Provide a background image.
Screenshot
-
Select Submit.
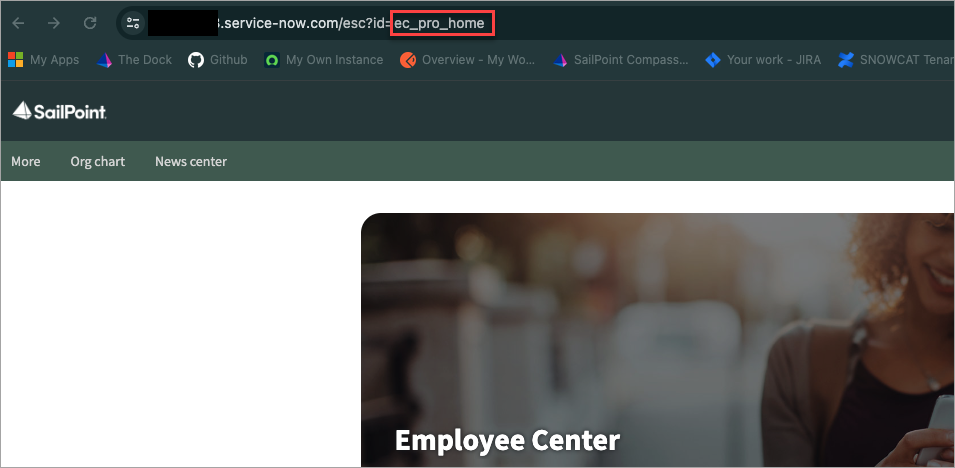
- Go to the Employee Center homepage by entering https://instance-name.service-now.com/esc in the browser.
-
Select the logo in the top-left corner. This ensures that the redirect homepage is selected while adding the quick link widget.
Screenshot
-
Highlight the homepage ID from the URL after
id=and copy it.Screenshot
-
Change the application scope to
Employee CenterorEmployee Center Prodepending on which scope your homepage is in. In this example, change to theEmployee Center Proscope. -
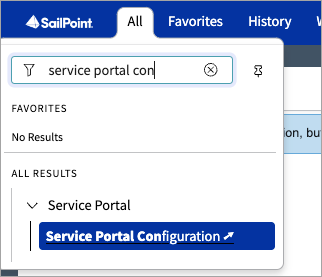
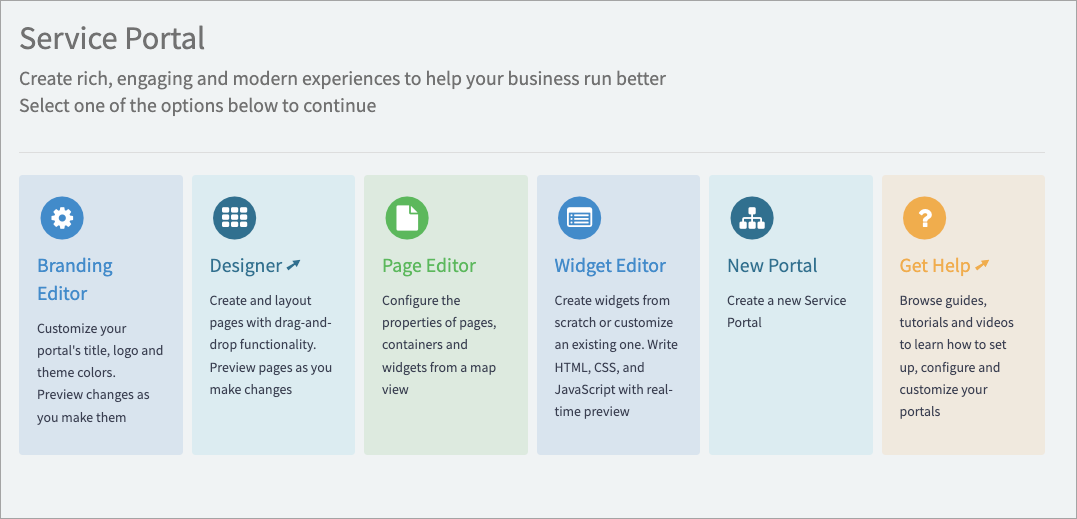
Use the application navigator to open
Service Portal Configuration, and then select Designer from the options shown.Screenshot
Screenshot
-
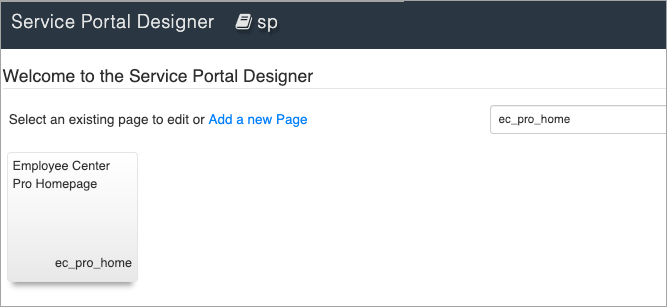
Paste the copied homepage ID to search for it.
Screenshot
-
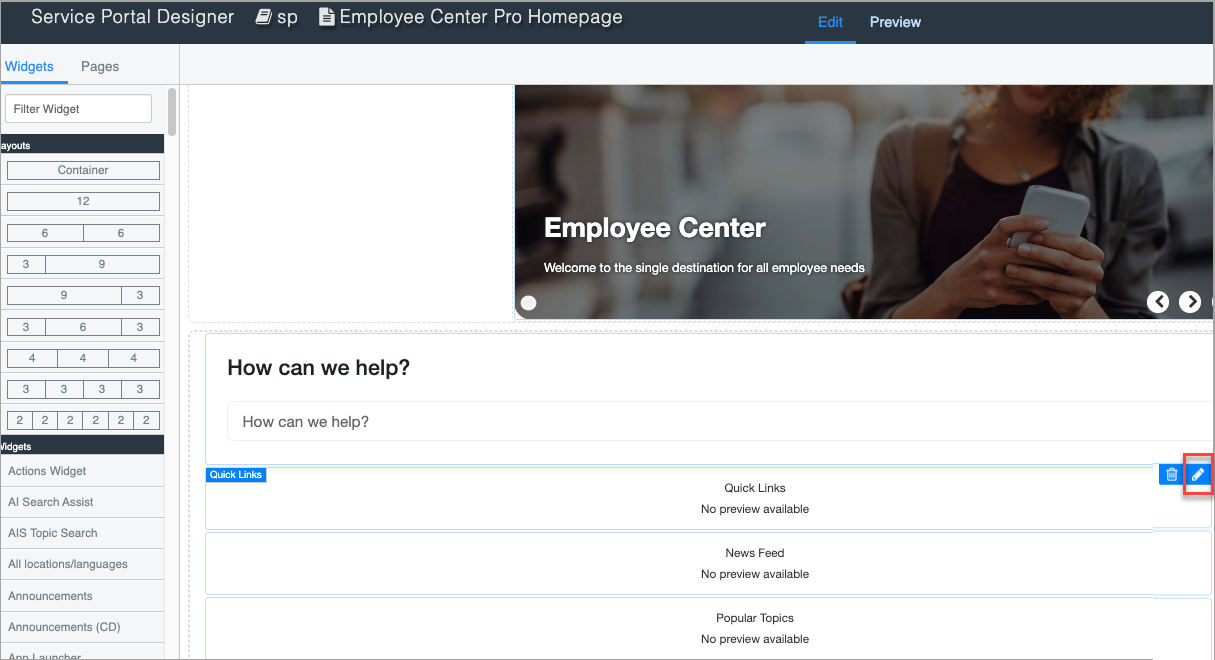
Select the
Pencilicon in the Quick Links widget. If the widget is not already listed on your homepage, search for it in theWidgetslist on the left-hand side and add it to the page.Screenshot
-
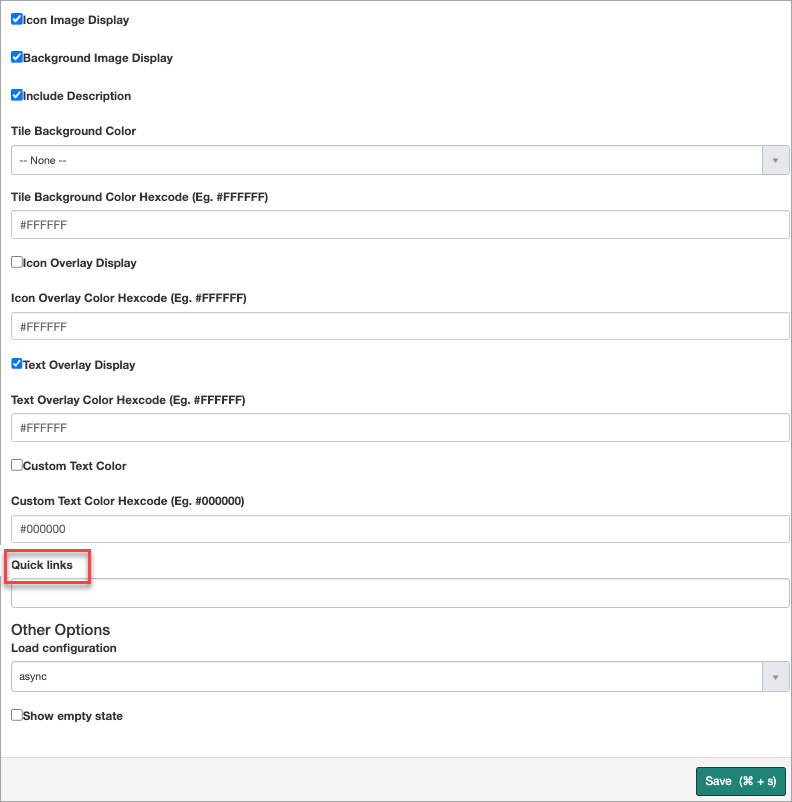
In the widget instance pop-up, look for Quick links.
Screenshot
-
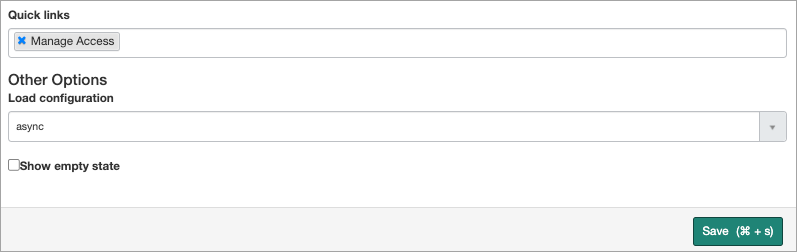
Search for the newly created Quick links entry and select Save.
Screenshot
-
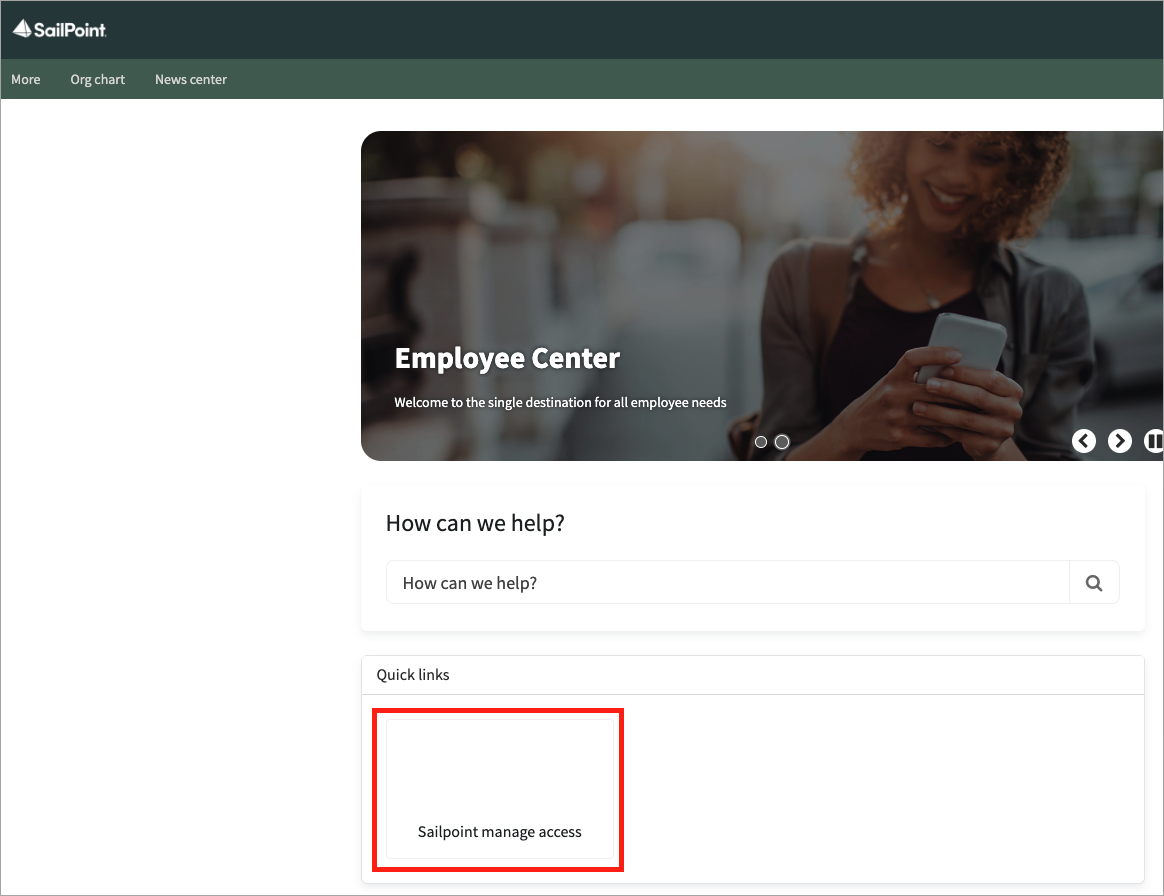
Confirm that the Manage Access quick link is available on the homepage.
Screenshot
Reports, Debug and Error Handlers
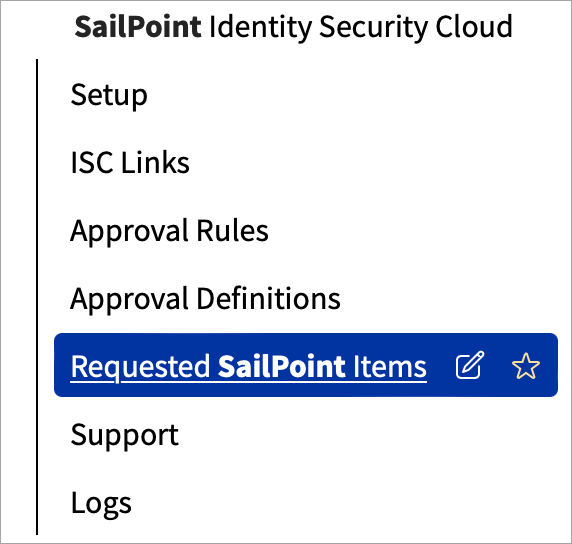
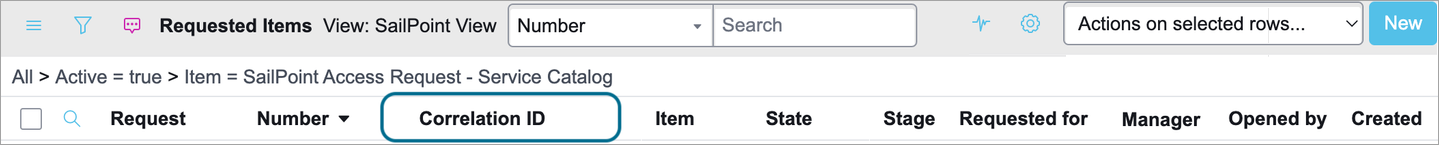
Admins and users with appropriate access to SailPoint Access Request - Service Catalog can reference end user requests via the Requested SailPoint Items report. To access the report, go to SailPoint Identity Security Cloud > Requested SailPoint Items in the fulfiller view. A list will display the active user requests and their SailPoint correlation IDs that were created within the instance for SailPoint Access Request - Service Catalog.
Screenshot
Visible columns include Correlation ID, which stores the request ID generated in SailPoint, along with all the variables displayed as columns.
Screenshot
Pages using widgetized code introduced from v4.0 will have the ability to display a varying level of debug and error messages. These play a crucial role to pinpoint bugs, troubleshoot issues, and ensure the stability.
Log levels can be configured to Debug, Info, Warn and Error. The default and suggested value is Warn.
ServiceNow displays a specific error type along with all error types that are higher in the hierarchy. The default error log hierarchy is as follows: Error > Warn > Info > Debug. Therefore, when the default value is set to Warn, both errors and warnings will be recorded in the ServiceNow logs table.
Setting the property to Debug will lead to an increased number of messages appearing in the logs table. It is recommended to use this setting judiciously, particularly when diagnosing a specific issue.
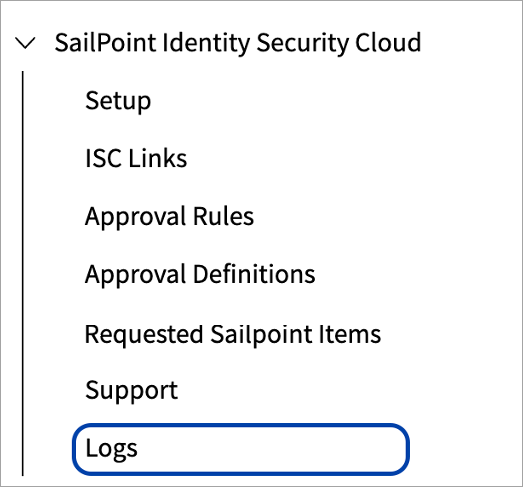
Admins have the option to select the Logs link to specifically identify errors associated with this application, in addition to the standard ServiceNow system logs table.
Screenshot
This table lists the specific errors that the widgetized SailPoint Service Connector code, implemented in version 4.0, will log.
| Code | Type | Message | Resolution details |
|---|---|---|---|
| ISC0001 | ERROR | Catalog item is missing, please check with your administrator | Verify that the necessary catalog item - 'Sailpoint Access Request - Service Catalog' (sys-id: xxxx) is present, active and requestable in your instance. |
| ISC0002 | ERROR | Missing connection parameters, please check with your administrator | Verify that all the connection properties including 'x_sap_intidn.x_sp_spnt_snow_int.spnt_endpoint_url', 'x_sap_intidn.x_sp_spnt_snow_int.spnt_client_id', and 'x_sap_intidn.x_sp_spnt_snow_int.spnt_client_secret' are present and correctly filled in. |
| ISC0003 | ERROR | Cannot connect to the target instance, please check with your administrator | There is an issue connecting to the target instance with the provided client_id and client_secret. Ensure that the provided values are correct. |
| ISC0004 | ERROR | Method failed to complete | A specific error/exception has occurred while execution. Refer to the details attribute logged along with the error to debug further. |
| ISC0005 | ERROR | Incorrect field name | An incorrect field name was encountered while trying to fetch user details. Verify the set-up in user display widgets where an incorrect field name was specified. |
| ISC0006 | ERROR | Could not find UI Handler | UI Handler is used for communicating between ServiceNow widgets and server side code. Verify that an Extension Point - ISCUIHandler exists and there is at least one active implementation present under it. |
| ISC0007 | WARNING | Incomplete details received | Incomplete access object details received from SailPoint. Verify the configuration on the SailPoint tenant. |
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.