Connecting SailPoint and Microsoft Entra ID SaaS
To connect SailPoint with Microsoft Entra ID, perform the following tasks:
Adding the Source in SailPoint
To connect to SailPoint, perform the following steps. Once the connection is made, you can configure it to meet your company's needs.
Important
By default, the provisioning feature is disabled, and the connector only supports read-only operations. To support provisioning operations, you must manually enable the feature in the source configuration.
To configure a new source:
- Sign in to SailPoint.
- Go to Admin > Connections > Sources.
- Select Create New.
- Search for the connector by entering the name in the search box, and then select Actions.
-
In the Actions dropdown list, select the setup method:
-
Express Setup - Quickly create a read-only connection to your target system by providing minimal configurations and authentication. On completion, aggregation is automatically started.
Note
Express Setup supports Credential Providers. For information on supported credential providers and configuration, refer to Credential Providers. For more information, contact your SailPoint Customer Service Manager.
-
Standard Setup - Provide detailed basic configuration to create the source. Once the source is created, continue with source setup.
-
Configuring a Source Using Express Setup
Express Setup minimizes the initial configuration process so you can quickly connect the application and immediately begin aggregating user account and entitlement data.
- Review the directions and select Start Express Setup.
-
Review the pre-populated Source Name, Source Owner, and Description. To update, select Edit.
Note
The source name must be unique. You can change these settings later in the source configuration.
-
(Optional) If enabled for your organization, select the Use a Credential Provider checkbox to manage the source's authentication using a credential provider.
Note
To add a Credential Provider in SailPoint, go to Admin > Connections > Credential Providers. For more information about credential providers, refer to Credential Providers.
-
Configure the authentication to allow SailPoint to connect to the source. For more information, refer to the Connection Settings section.
-
Select Finish.
After a successful test connection, the system creates your source and prompts you to run an aggregation.
-
If you want to aggregate now, select Aggregate.
- To see the latest account aggregation history, go to Account Management > Account Aggregation.
- To see the list of aggregated source accounts, go to Account Management > Accounts.
-
If you want to aggregate later, select Exit. This returns you to the Sources page. Your new source is listed, but contains no accounts or aggregation history yet.
-
Configuring a Source Using Standard Setup
Use Standard Setup to configure the connector for full feature support.
- In the Source Name field, enter a unique and descriptive name for your source. Source names cannot exceed 128 characters.
- In the Description field, provide additional details about the source to help distinguish it from similar sources. This field allows a maximum of 2,000 characters.
- In the Source Owner field, begin typing the name of an owner. Matches appear after you type two or more letters. For more information, refer to Assigning a Source Owner.
- (Optional) Select a governance group to grant its members source or role sub-admin level oversight of the source and its access. For more information, refer to Creating and Managing Governance Groups.
- If this source represents a primary system containing your organization's personnel records, select the Authoritative Source checkbox. For more information, refer to Creating Identity Profiles.
- Select Continue. The source is created, and you are navigated to the Source Setup > Base Configuration page. Continue to configure your connected source there.
Base Configuration
Provide the base configuration parameters. Information you entered in the Create New Source dialog is automatically entered into the fields in the Base Configuration page. You can edit this information if necessary.
- Enter a unique name and description for the source.
-
In the Source Owner dropdown list, select the identity that owns this source.
- To find a source owner, begin entering their name.
-
(Optional) If enabled for your organization, select the Use a Credential Provider checkbox to manage the source's authentication using a credential provider.
Note
To add a credential provider, go to Admin > Connections > Credential Providers. For more information about credential providers, refer to Credential Providers.
-
Configure the authentication to allow SailPoint to connect to the source. Refer to Connection Settings for more information.
-
(Optional) In the Governance Group for Source Management dropdown list, select a governance group to associate with this source. For more information about governance groups, refer to Associating Governance Groups with a Source.
-
(Optional) Choose whether to enable or disable provisioning for the source. Provisioning is disabled by default.
-
Enable Provisioning - Set the toggle to Enabled to allow the source to create, update, and deactivate accounts in the connected source system.
-
Disable Provisioning - Set the toggle to Disabled to disable provisioning for the source. Disabling provisioning will prevent the creation, updating, or deactivating of accounts on this source.
-
-
Select Save.
Connection Settings
Provide the information required to connect to the Microsoft Entra instance based on the selected Grant Type for OAuth 2.0 authentication:
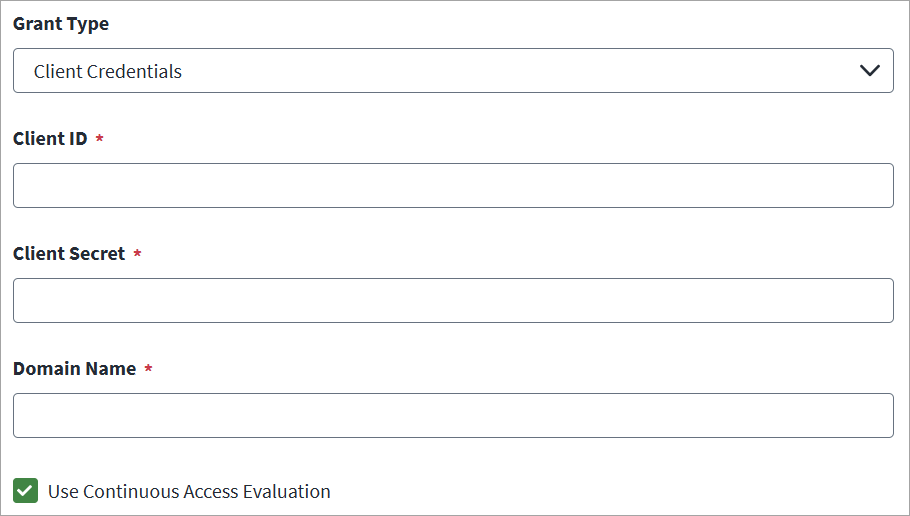
Client Credentials
Screenshot
-
In Client ID and Client Secret, enter the Microsoft Entra API details for OAuth2 authentication.
-
In Domain Name, enter the name of the Microsoft Entra domain to be managed. For example,
contoso.onmicrosoft.com.Important
If you are using SailPoint CIEM, you must add the Entra domain under Client Credentials in the Domain Name field. It must end in
.onmicrosoft.comor.onmicrosoft.us. Custom domain names are not supported. -
(Optional) Select the Use Continuous Access Evaluation checkbox to enable the connector to leverage the Microsoft Entra real-time enforcement of Conditional Access location and risk policies along with instant enforcement of token revocation events for an enterprise application (service principal).
-
Select Save.
Refresh Token
Screenshot
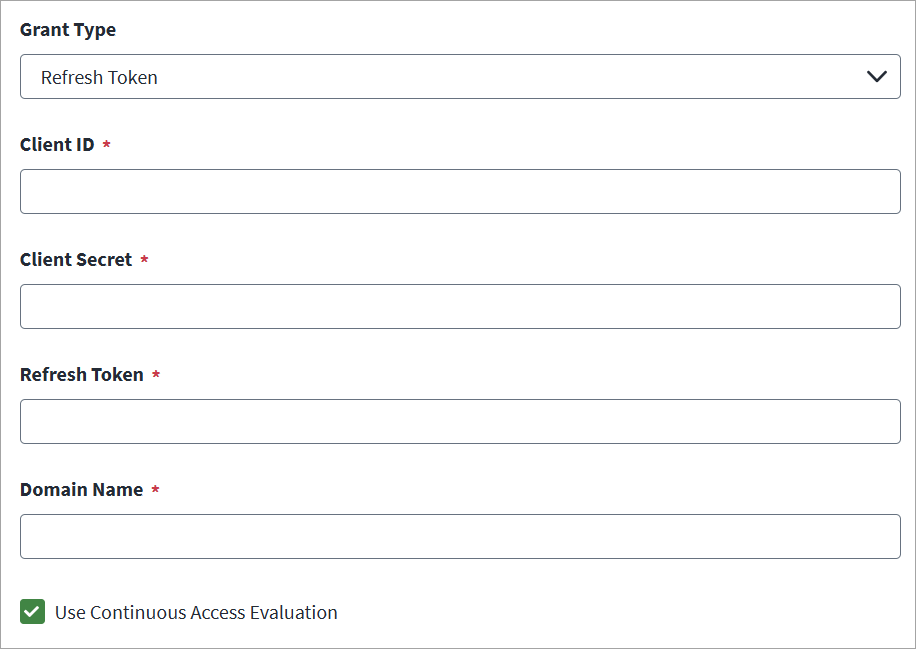
- In Client ID and Client Secret, enter the Microsoft Entra API details for OAuth2 authentication.
- Enter the valid Refresh Token.
- Enter the Domain Name of the Microsoft Entra domain to be managed. For example, contoso.onmicrosoft.com.
- (Optional) Select the Use Continuous Access Evaluation checkbox to enable the connector to leverage the Microsoft Entra real-time enforcement of Conditional Access location and risk policies along with instant enforcement of token revocation events for an enterprise application (service principal).
- Select Save.
JWT Certificate Credentials
Screenshot
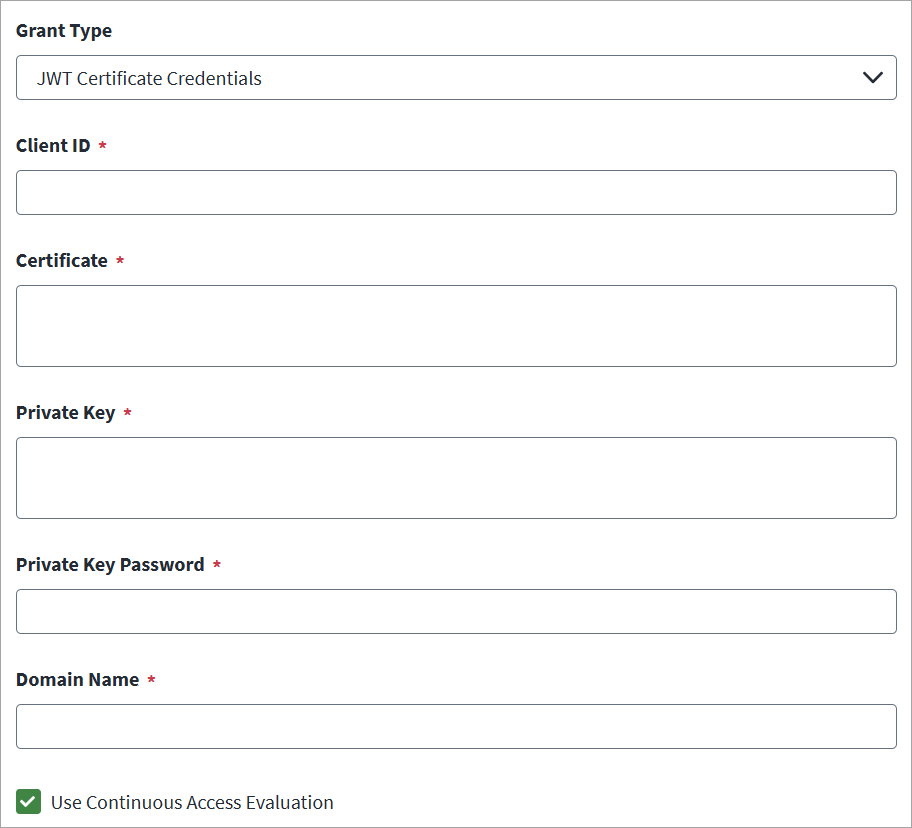
To generate the JWT certificate credentials, refer to Creating OAuth 2.0 JWT Certificate Credentials.
- In the Client ID field, enter the Microsoft Entra API Client ID for OAuth2 authentication.
- In the Certificate field, provide the unique alpha-numeric value of certificate used to sign the JWT assertion.
- Enter the Private Key text used for encrypting the JWT assertion.
- Enter the Private Key Password that is used for decrypting the private key.
- In the Domain Name field, enter the name of the Microsoft Entra domain to be managed. For example, contoso.onmicrosoft.com.
- (Optional) Select the Use Continuous Access Evaluation checkbox to enable the connector to leverage the Microsoft Entra real-time enforcement of Conditional Access location and risk policies along with instant enforcement of token revocation events for an enterprise application (service principal).
- Select Save.
Activity Insights Settings
SailPoint pulls in activity data in the form of events like user logins, password changes, and content updates within the application. You can view an identity’s activity data within an application to discover trends for that user.
Important
Contact your SailPoint Customer Success Manager (CSM) for more information on Activity Insights. For more information on utilizing activity data, refer to Activity Insights.
Activity Insights Settings allows you to gather account information and activity data from Microsoft Entra ID. To enable Activity Insights for the Microsoft Entra ID application, refer to Prerequisites for more information.
To configure Activity Insights, complete the following:
Screenshot
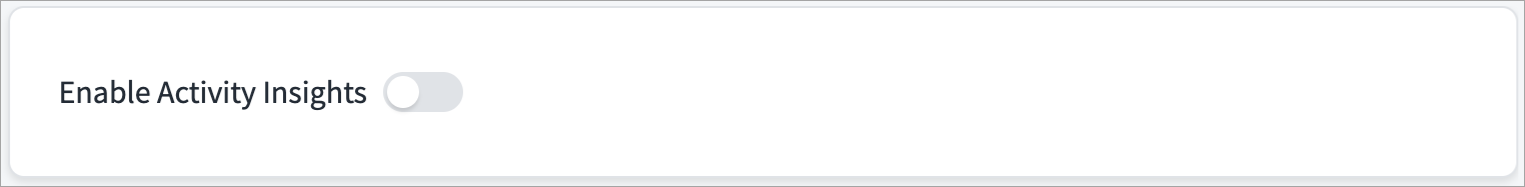
- Go to Activity Insights Settings.
- Select Enable Activity Insights to view access to data insights on source and application activity such as logins and other app-specific events.
- Select Save.
Aggregation and Filter Settings
Aggregation Settings
This section contains the configuration parameters for aggregation and filter settings.
For more information about aggregation, refer to Loading Account Data.
For more information on the key factors to consider when choosing between Full Aggregation and Delta Aggregation, refer to FAQs.
Screenshot
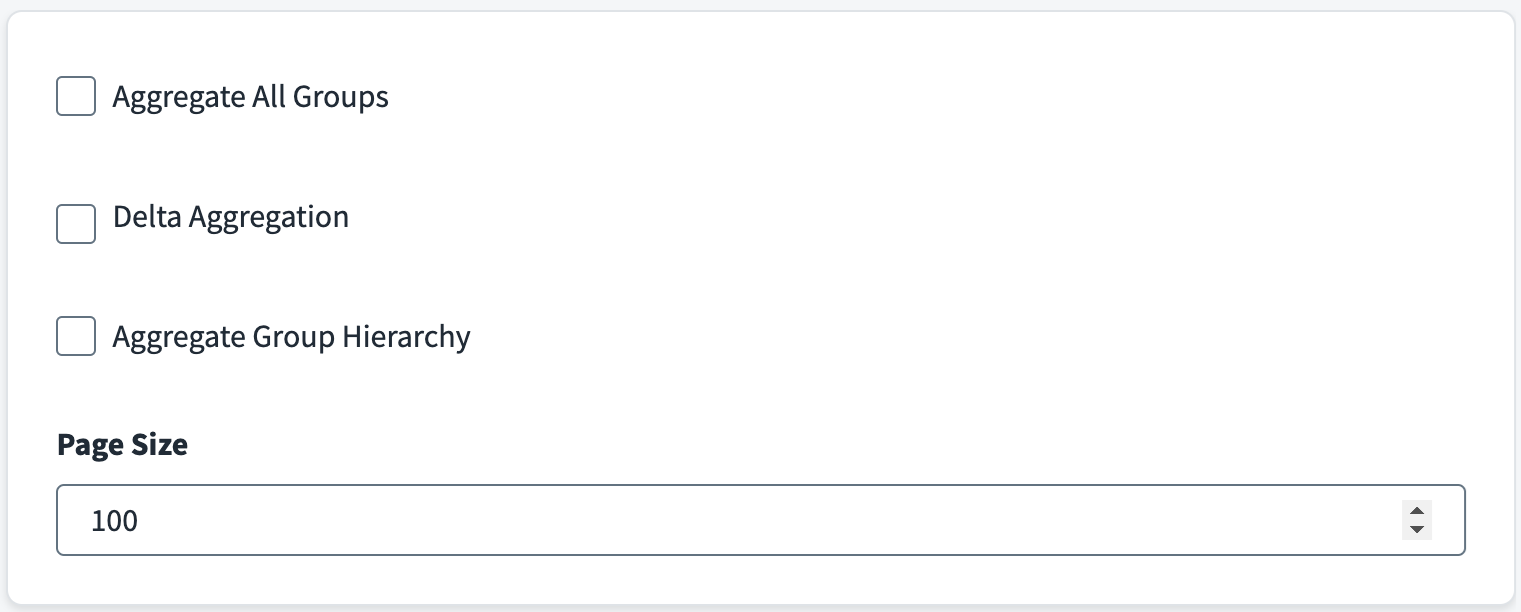
- Select the Aggregate All Groups checkbox to aggregate Security, Microsoft 365, Distribution List, and Mail Enabled Security Groups. If this option is not selected, only Security Groups are aggregated.
- Select the Delta Aggregation checkbox to aggregate delta changes for accounts and groups.
- Select the Aggregate Group Hierarchy checkbox to read the parent and child group hierarchical information for Microsoft Entra groups.
- Select Exclude Inherited App Role Assignments to exclude inherited appRoleAssignments during account aggregation. Only application roles assigned directly to the account are aggregated.
- Enter the value of Page Size for the number of objects to be fetched in a single page when iterating over large data sets. The default value is 100.
Note
The connector uses paging and processes the retrieved accounts in parallel, improving account aggregation performance. The default configuration of the connector considers various level of rate limits set by the Microsoft Entra ID managed system. However, you can adjust the connector's aggregation performance by fine tuning the specific data set within your environment using Batch Size Configuration.
You can configure Batch Size Configuration in your existing sources by adding the userAggregationBatchSize attribute to your source XML using the following REST API:
POST https://{orgName}.api.identitynow.com/v3/sources/{source ID}
In the body of the POST, use the form-data as shown below:
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
Filter Settings
When configuring the filters, consider that the connector prioritizes account filters over group filters during aggregation. For example, the connector aggregates groups, which fall outside of the group filter, if the group is associated with an account included within the account filter.
Screenshot

-
Set the User Filters to define the scope of Accounts applied during account aggregation. For example, to aggregate those Microsoft Entra ID users who are active, use
accountEnabled eq true. For more information on filters, refer to the Microsoft documentation. -
Select Advanced User Filter to include advanced filter queries such as
endsWith,NOT, andNEduring aggregation processes.To use the extension attributes from
onPremisesExtensionAttributese.g.extensionAttribute1,extensionAttribute4etc. as user filter, please use the below syntax:onPremisesExtensionAttributes/extensionAttribute1 eq '21'Screenshot

Note
Select the “Advanced User Filter” checkbox as it is advanced query filter.
-
Set the Group Filters to define the scope of Groups applied during group aggregation. Group filters apply during entitlement aggregation. For example, to only aggregate Microsoft Entra ID groups whose display name is starting with letter A, use
startswith(displayName,'A'). For more information on filters, refer to the Microsoft documentation. -
Select Advanced Group Filter to include advanced filter queries such as endsWith, NOT, and NE during group aggregation processes.
-
Select the Group Membership Filters to define the scope of the group memberships included in account aggregation. These filters apply during the account aggregation and are only applicable to memberships belonging to
objectType = group. These are only applicable to the Security, Office 365, Mail Enabled Security, and Distributed type of group memberships. For more information on filters, refer to the Microsoft documentation.Note
You can provide filters as mentioned in the examples above, and the connector ensures the formation of an appropriate advanced filter query. This field supports advanced filter queries such as
endsWith,NOT, andNE.For example,
- To aggregate only group memberships with group display name starting with 'A', use
startswith(displayName,'A'). - To aggregate only group memberships with groups not belonging to on-premises AD (or to only include cloud group memberships), use
onPremisesSyncEnabled ne true. - To exclude dynamic group memberships during account aggregation , use
NOT groupTypes/any(c:c eq 'DynamicMembership')
Important
SailPoint recommends excluding membership information is not a best practice from a governance and security standpoint. You should have full visibility into users and devices, including their groups, assigned permissions, and how these configurations impact access to resources. The group membership filter should be used carefully and only when necessary, ensuring that access is managed and only the right individuals have access to sensitive information or resources.
- To aggregate only group memberships with group display name starting with 'A', use
-
In the Directory Roles Filter field, when the entitlement schema "roles" is present in the source, enter filter statements to ensure that only the specified roles are aggregated during entitlement aggregation. For example,
isBuiltIn eq true. For more information on filtering conditions and values, refer to the Microsoft documentation. -
Select Save.
Note
-
If the filter (either Group Filter or User Filter) uses any advanced query filter (per the Microsoft documentation), then Advanced User Filter and Advanced Group Filter should also be selected.
-
The connector supports advanced query filters like
endsWith,NOT, andNEduring aggregation. The Azure API does not support the advanced query filters while also using an expanded attribute such asmanagerin the URL. When using the advanced filters, ensure that you remove themanagerattribute from the account schema and remove theownersattribute from the group schema. -
If you're using the advanced filters you must add the
supportsAdvancedAccountFilterattribute to the source XML using the SailPoint REST API. The connector will then automatically add the required header (ConsistencyLevel:eventual) in the header and add&$count=trueFor example:
POST https://{orgName}.api.identitynow.com/cc/api/source/update/{source ID}In the body of the POST, use the form-data as follows:
- Key:
supportsAdvancedAccountFilter - Value:
true
- Key:
Machine Identity Governance Settings
Important
You must have a SailPoint Agent Identity Security license to enable the Agent governance features. Contact your SailPoint Customer Success Manager for more details on obtaining the necessary license.
To enable agents aggregation, follow these steps:
Screenshot
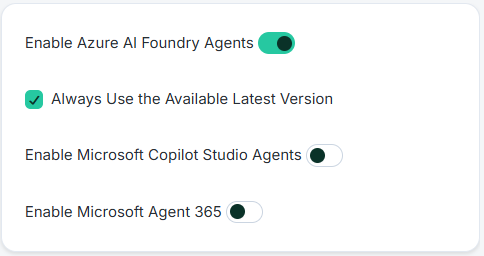
- Go to Microsoft Entra ID SaaS source configuration page within SailPoint.
- Select Machine Identity Governance Settings tab.
- Select Enable Azure AI Foundry Agents. This enables Azure AI Foundry agents aggregation for your environment. For more information, refer to Azure AI Foundry Agents Management.
- Select Always Use the Available Latest Version if you want to use the latest available version of Azure Foundry AI agents for your environment. To select this option, ensure you have selected Enable Azure AI Foundry Agents.
- Select Enable Microsoft Copilot Studio Agents. This enables Copilot agent aggregation for your environment. For more information, refer to Microsoft Copilot Studio Agents Management.
- Select Enable Microsoft Agent 365 when your tenant is licensed for Microsoft Agent 365. When you turn this toggle on, all catalog platform checkboxes below default to checked. If your source uses Client Credentials authentication, you need to provide a refresh token with the required permissions. For more information, refer to Microsoft Agent 365 Catalog Management.
- Select Save.
Additional Configurations
Additional Configuration Parameters
You must add the following attributes in the connector using the SailPoint REST API. Refer to Best Practices: REST API Authentication and REST API - Update Source (Partial).
| Parameter | Description |
|---|---|
| createAppTemplateSPNDelay | (Only applicable for create service principals and applications that are created making use of gallery templates). The time, in seconds, to wait after the create service principal and application, and before making the update for basic SAML configuration. The default is 24 seconds. For example, <entry key="createAppTemplateSPNDelay" value="30"/> |
| performGetObjectForEXOAttributes | To enable / disable reading of exchange online attributes from exchange system (real time exchange online attribute values) during explicit get object call for specified user, set the value of performGetObjectForEXOAttributes attribute to true.Note This configuration parameter is applicable only for get object call. Enabling this configuration parameter will degrade performance of get object calls. |
| createAccountTimelag | Time in seconds to wait after create account and before calling get account. The default is 20 seconds. |
| fetchB2CMembership | (Applicable for B2C tenant only) If set to true B2C user memberships is fetched for all users. The default value is false. |
| useMSGraphAPI | Enables use of Microsoft Graph API for all connector operations. To use the latest attributes and features supported by Microsoft Graph API, add the useMSGraphAPI attribute using the REST API and set it to true. |
| msgraph-api-version | The Microsoft Graph API version is configurable. You must add the msgraph-api-version attribute in the source using the REST API.The value of the attribute must be a valid version stated by Microsoft for MS Graph APIs. |
| skipEncodingImmutableId | Enable to skip encoding of ImmutableID while creating a federated user. Enable this feature by using the REST API to set the skipEncodingImmutableID parameter to true. The default value is false. |
| fetchServicePlan | To disable fetching of service plans during account and group aggregation, set the value of fetchServicePlan to false using the REST APIs. For example:curl -L -X PATCH 'https:// |
| sleepBetweenAssignedPlans | Time in seconds to wait between adding or removing assignedPlans. The default is 3 seconds.Add the sleepBetweenAssignedPlans attribute using the REST API and set it as required. |
Review and Test
Perform a test to confirm the connection to SailPoint.
- Go to Review and Test.
-
Confirm that the entries in each field are correct.
If you note any mistakes, return to the section and make corrections.
-
Select Test Connection.
SailPoint Application Onboarding
SailPoint application onboarding enables you to easily onboard new applications and create sources following the successful onboarding of a discovery source. To use this feature, continue to Discovered Applications in the SailPoint user interface.
For more information, refer to Application Onboarding in the SailPoint SaaS documentation.
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.