Feature Management
This section describes the various features that you can enable or disable for your configuration. Feature management enables you to select or deselect features on demand as your need for their services arises.
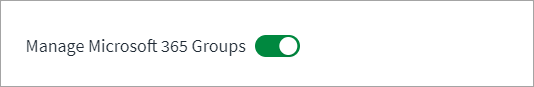
Manage Microsoft 365 Groups
Screenshot
-
Go to Feature Management.
-
Select Manage Microsoft 365 Groups if you want to enable the option to manage Office 365 Groups.
Important
If you are utilizing Data Access Services (DAS) to manage access to cloud applications like Microsoft 365, you must enable the Manage Microsoft 365 Groups. This ensures that DAS can properly synchronize and manage Microsoft 365 groups, which control access to various collaborative resources within the Microsoft 365 ecosystem.
-
Select Save.
Managed Identities Settings
Screenshot
-
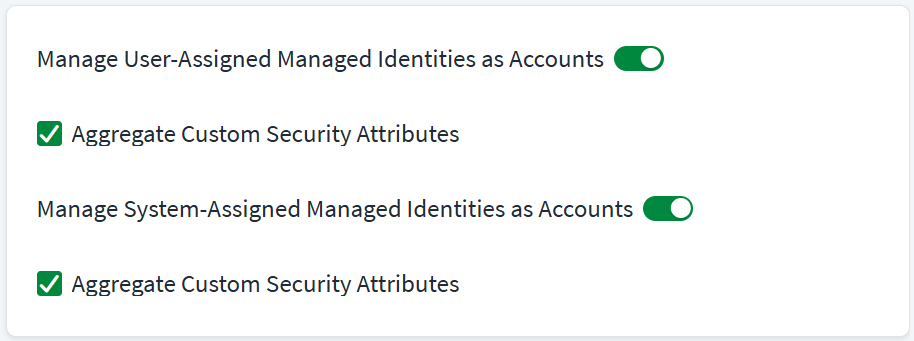
Go to Feature Management > Managed Identities Settings.
-
Enable the setting that corresponds to the identity type you want to manage:
- For User-Assigned Managed Identities: Enable Manage User-Assigned Managed Identities as Accounts.
- For System-Assigned Managed Identities: Enable Manage System-Assigned Managed Identities as Accounts.
- For Microsoft Entra Service Principals: Go to Feature Management > Manage Microsoft Entra Service Principals as Accounts. Enable Manage Microsoft Entra Service Principals as Accounts.
Select Aggregate Custom Security Attribute checkbox to aggregate custom attributes for respective identities. For more information, refer to Custom Security Attributes.
Manage Microsoft Entra Service Principals As Accounts
Screenshot
-
Go to Feature Management.
-
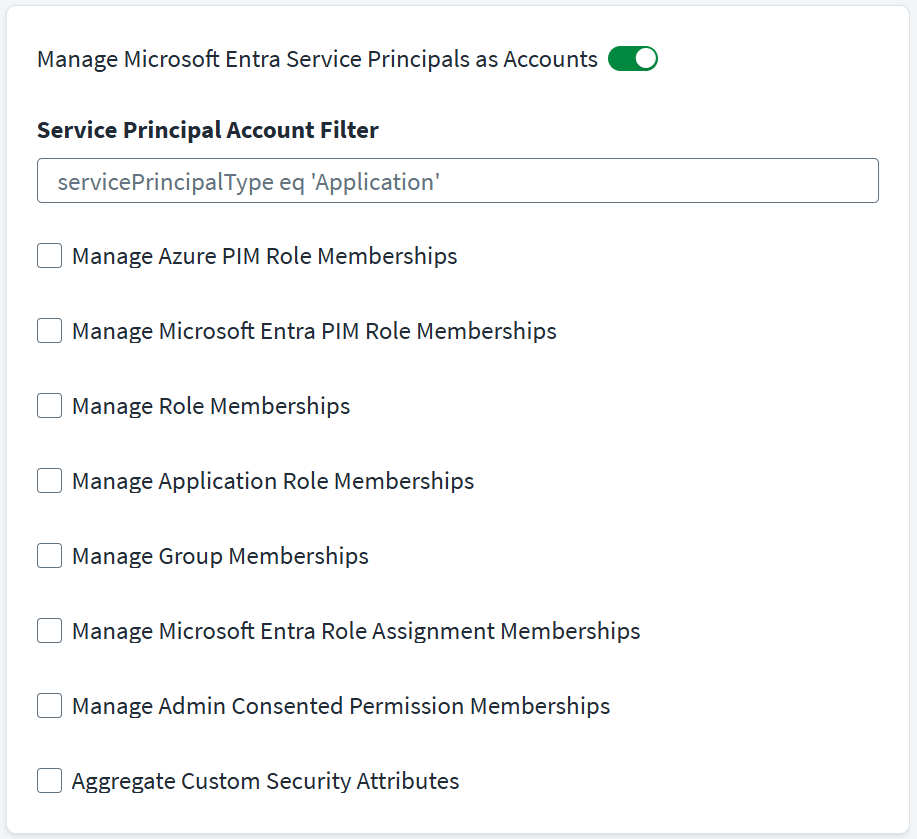
Select Manage Microsoft Entra Service Principals as Accounts to aggregate Azure Service Principals along with Users during the account aggregation process. By default, when this is enabled, entitlements are not fetched. You must select the entitlements you want to fetch from the available list.
Note
To automate the process of adding Service Principal account attributes to the account schema during Account Schema configuration, select Include Attributes in Schema for managing azure Service Principal as account . For more information, refer to Service Principal as Accounts Attributes.
-
In the Service Principal Account Filter field, enter filter statements to ensure only the correct Azure Service Principals are included in the aggregation process. The default filter is
servicePrincipalType eq 'Application'Note
Advanced queries are not supported.
Example filters:
-
For a filter to match the Enterprise Application default view on the Azure portal use the following:
tags/Any(x: x eq 'WindowsAzureActiveDirectoryIntegratedApp')
-
-
Select the Manage Role Memberships checkbox to manage Directory Role memberships for Service Principal.
-
Select the Manage Application Role Memberships checkbox to manage Azure Application Role memberships for Service Principal.
-
Select the Manage Group Memberships checkbox to manage Microsoft Entra Group memberships for Service Principal.
-
Select the Manage Microsoft Entra Role Assignment Memberships checkbox to manage Azure Cloud Group memberships for Service Principals.
-
Select the Manage Admin Consented Permission Memberships checkbox to manage Azure admin consented permissions for Service Principals.
Note
This is for delegated permissions.
-
Select the Aggregate Custom Security Attribute checkbox to aggregate custom security attributes for Service Principals. For more information, refer to Custom Security Attributes.
-
Select Save.
Manage Exchange Online
-
Go to Feature Management.
-
Select Manage Exchange Online to enable aggregation of Exchange mailbox attributes. This includes Shared Mailboxes, User Mailbox properties, Distribution Lists, and Mail-Enabled Security Groups.
-
Select one of the following from the Authentication Method dropdown list:
-
Basic Authentication
Screenshot
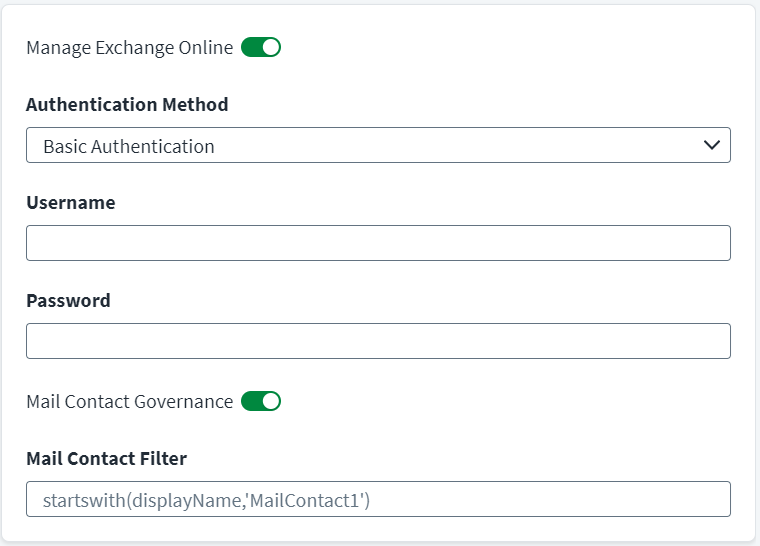
- Select Basic Authentication from the dropdown list.
- Enter the Username (UserPricipalName) and associated Password of a user that has the Exchange Administrator role.
- Select Save.
Certificate Based Authentication
Screenshot
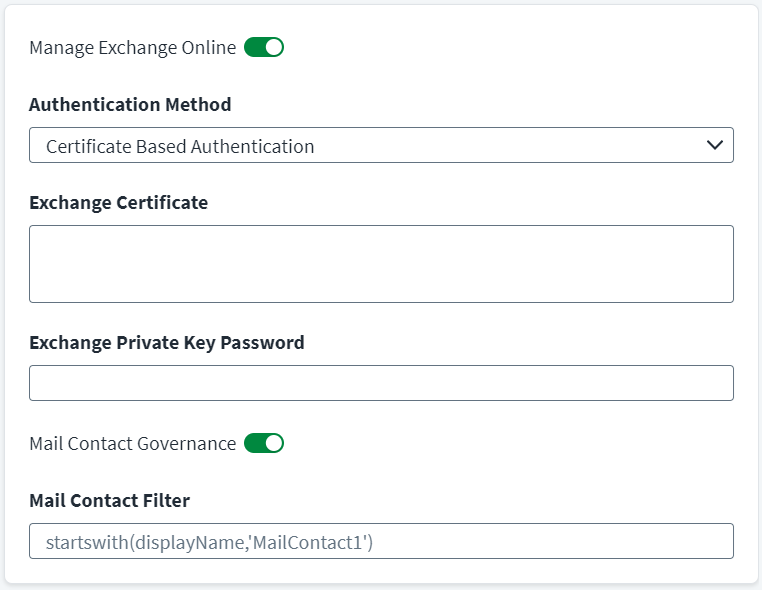
- Select Certificate Based Authentication from the drop dropdown list.
- In Exchange Certificate, provide the unique alpha-numeric value of the certificate used to sign the JWT assertion. The same certificate must also be uploaded to the respective Microsoft Entra application.
- Enter the Exchange Private Key Password that is used for decrypting the private key.
- Select Save.
-
-
Select Mail Contact Governance to manage mail contacts as accounts. For more information, refer to Azure Mail Contact Management.
-
In the Mail Contact Filter field, enter any filter statements used to define the scope of mail contacts for aggregation. For example,
startswith(displayName,'MailContact1')
Manage Azure Privileged Identity Management
Privileged Identity Management (PIM) enables you to manage, control, and monitor access to important resources in your organization. These resources include resources in Microsoft Entra ID, Azure, and other Microsoft Online Services such as Microsoft 365 or Microsoft Intune.
For more information, refer to Azure Privileged Identity Management (PIM).
Screenshot
-
Go to Feature Management.
-
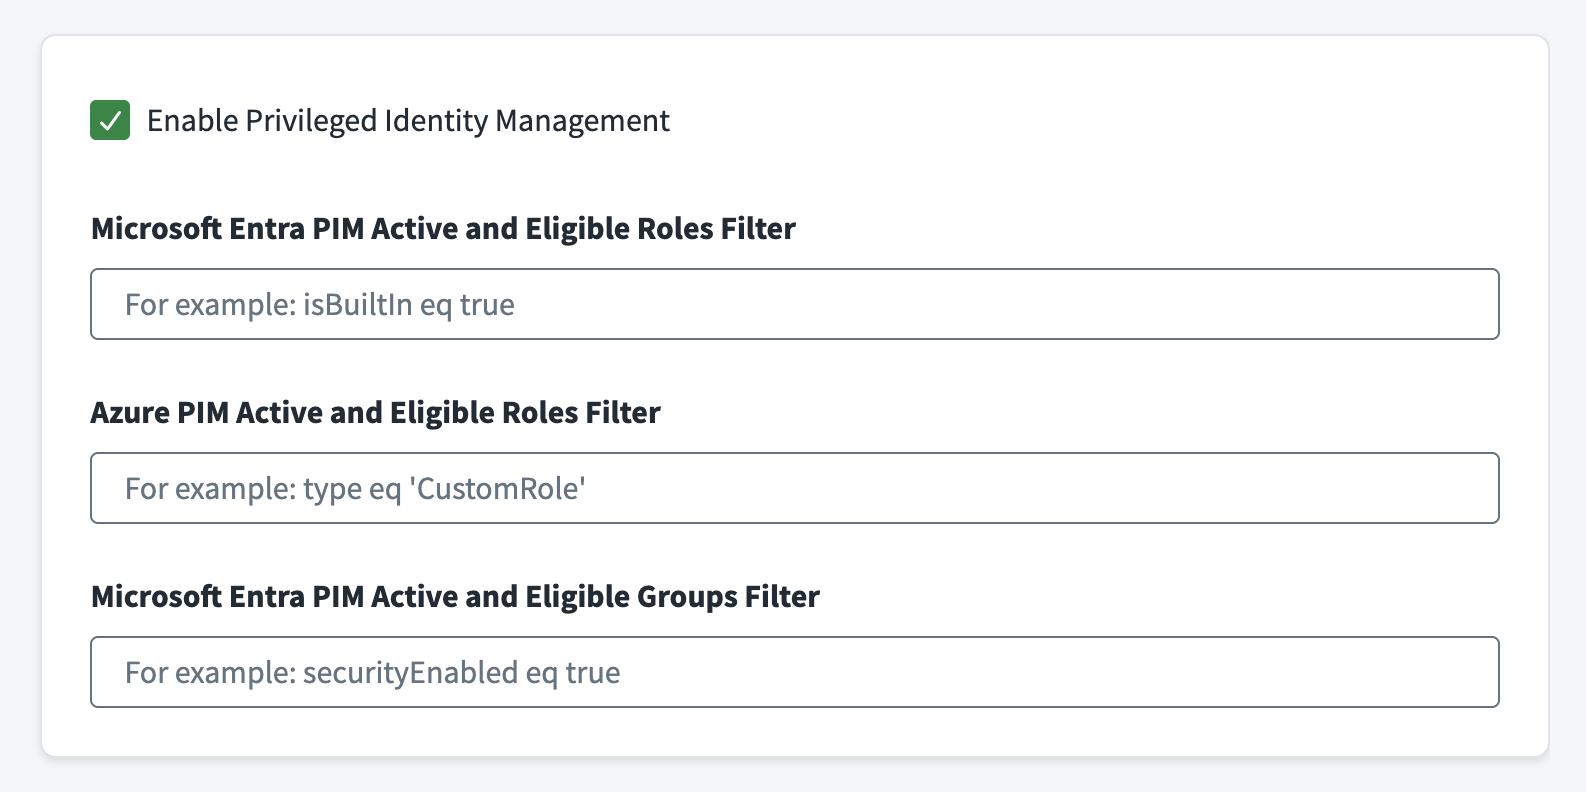
Select the Enable Privileged Identity Management checkbox to define the scope of the Microsoft Entra PIM roles (Microsoft Entra as well as Azure). For more information on privileged identity management, refer to the Microsoft documentation.
-
In the Microsoft Entra PIM Active and Eligible Roles Filter field, enter a filter to define the scope of the Microsoft Entra PIM roles aggregated during entitlement aggregation. For example,
isBuiltIn eq trueFor more information on filtering conditions and values, refer to the Microsoft Documentation.
-
In the Azure PIM Active and Eligible Roles Filter field, enter a filter to define the scope of the Azure PIM roles aggregated during entitlement aggregation. For example,
type eq 'CustomRole'For more information on filtering conditions and values, refer to the Microsoft Documentation.
-
In the Microsoft Entra PIM Active and Eligible Groups Filter field, enter a filter to define the scope of the Azure PIM groups aggregated during entitlement aggregation. For example,
securityEnabled eq trueImportant
User-defined filter expressions in this field cannot be combined with the connector's internal group type filter, which restricts groups to Office 365 and Security types. The internal filter is always applied. Any value you enter in this field functions as an additional standalone filter on the PIM group catalog and does not combine with the internal filter.
For more information on filtering conditions and values, refer to the Microsoft Documentation.
-
Select Save.
Access Package Management Settings
An access package is a bundle of all the resources with the access a user needs to work on a project or perform their task. Access packages are used to govern access for your internal employees, and also users outside your organization. For more information, refer to Access Package Management.
Screenshot
- Go to Feature Management.
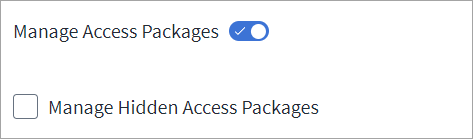
- Select Manage Access Packages to turn this feature on or off. When this is turned off, you see a black X. If it is turned on, you see a blue ✔. The default is off.
- Select the Manage Hidden Access Packages checkbox to manage access packages hidden from end users in the My Access portal.
- Select Save.
Administrative Unit Management Settings
Screenshot
- Go to Feature Management.
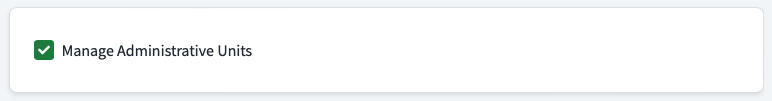
- Select Manage Administrative Units to manage administrative units.
- Select Save.
Account Disable Settings
To configure Account Disable Settings:
Screenshot
- Go to Feature Management.
- Under Account Disable Settings, select Revoke Session after Disabling User Account to sign the user out of all existing sessions when their account is disabled.
- Select Save.
Note
- For newly created sources, this is enabled by default to align with security best practices.
- For existing sources, this is disabled by default. When required, ensure to enable this option.
For more information about this feature, including the required permissions, refer to Revoke Session After Disabling User Account.
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.