Connecting SailPoint and ServiceNow Identity Governance SaaS
To connect SailPoint with ServiceNow Identity Governance, perform the following tasks:
Adding the Source in SailPoint
To connect to SailPoint, perform the following steps. Once the connection is made, you can configure it to meet your company's needs.
Important
By default, the provisioning feature is disabled, and the connector only supports read-only operations. To support provisioning operations, you must manually enable the feature in the source configuration.
To configure a new source:
- Sign in to SailPoint.
- Go to Admin > Connections > Sources.
- Select Create New.
- Search for the connector by entering the name in the search box, and then select Actions.
-
In the Actions dropdown list, select the setup method:
-
Express Setup - Quickly create a read-only connection to your target system by providing minimal configurations and authentication. On completion, aggregation is automatically started.
Note
Express Setup supports Credential Providers. For information on supported credential providers and configuration, refer to Credential Providers. For more information, contact your SailPoint Customer Service Manager.
-
Standard Setup - Provide detailed basic configuration to create the source. Once the source is created, continue with source setup.
-
Configuring a Source Using Express Setup
Express Setup minimizes the initial configuration process so you can quickly connect the application and immediately begin aggregating user account and entitlement data.
- Review the directions and select Start Express Setup.
-
Review the pre-populated Source Name, Source Owner, and Description. To update, select Edit.
Note
The source name must be unique. You can change these settings later in the source configuration.
-
(Optional) If enabled for your organization, select the Use a Credential Provider checkbox to manage the source's authentication using a credential provider.
Note
To add a Credential Provider in SailPoint, go to Admin > Connections > Credential Providers. For more information about credential providers, refer to Credential Providers.
-
Configure the authentication to allow SailPoint to connect to the source. For more information, refer to the Connection Settings section.
-
Select Finish.
After a successful test connection, the system creates your source and prompts you to run an aggregation.
-
If you want to aggregate now, select Aggregate.
- To see the latest account aggregation history, go to Account Management > Account Aggregation.
- To see the list of aggregated source accounts, go to Account Management > Accounts.
-
If you want to aggregate later, select Exit. This returns you to the Sources page. Your new source is listed, but contains no accounts or aggregation history yet.
-
Configuring a Source Using Standard Setup
Use Standard Setup to configure the connector for full feature support.
- In the Source Name field, enter a unique and descriptive name for your source. Source names cannot exceed 128 characters.
- In the Description field, provide additional details about the source to help distinguish it from similar sources. This field allows a maximum of 2,000 characters.
- In the Source Owner field, begin typing the name of an owner. Matches appear after you type two or more letters. For more information, refer to Assigning a Source Owner.
- (Optional) Select a governance group to grant its members source or role sub-admin level oversight of the source and its access. For more information, refer to Creating and Managing Governance Groups.
- If this source represents a primary system containing your organization's personnel records, select the Authoritative Source checkbox. For more information, refer to Creating Identity Profiles.
- Select Continue. The source is created, and you are navigated to the Source Setup > Base Configuration page. Continue to configure your connected source there.
Base Configuration
Provide the base configuration parameters. Information you entered in the Create New Source dialog is automatically entered into the fields in the Base Configuration page. You can edit this information if necessary.
- Enter a unique name and description for the source.
-
In the Source Owner dropdown list, select the identity that owns this source.
- To find a source owner, begin entering their name.
-
(Optional) If enabled for your organization, select the Use a Credential Provider checkbox to manage the source's authentication using a credential provider.
Note
To add a credential provider, go to Admin > Connections > Credential Providers. For more information about credential providers, refer to Credential Providers.
-
Configure the authentication to allow SailPoint to connect to the source. Refer to Connection Settings for more information.
-
(Optional) In the Governance Group for Source Management dropdown list, select a governance group to associate with this source. For more information about governance groups, refer to Associating Governance Groups with a Source.
-
(Optional) Choose whether to enable or disable provisioning for the source. Provisioning is disabled by default.
-
Enable Provisioning - Set the toggle to Enabled to allow the source to create, update, and deactivate accounts in the connected source system.
-
Disable Provisioning - Set the toggle to Disabled to disable provisioning for the source. Disabling provisioning will prevent the creation, updating, or deactivating of accounts on this source.
-
-
Select Save.
Connection Settings
Choose the appropriate authentication type and provide the information required to connect and interact with the source.
Note
Each time you change the Authentication Type for the ServiceNow connector, you must select Test Connection.
You can configure your source using the following authentication types:
- Configure the Connection with Basic Authentication
- Configure the Connection with OAuth 2.0 Authentication
Configure the Connection with Basic Authentication
Screenshot
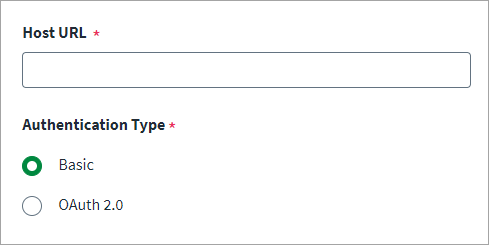
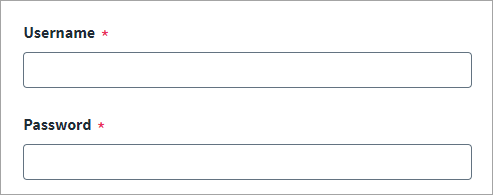
- Enter the Host URL for the ServiceNow instance that is used for communication.
- Select Basic as the Authentication Type.
- Enter the Username and Password that have the appropriate permissions. For more information, refer to Required Permissions.
- Select Save.
Configure the Connection with OAuth 2.0 Authentication
Screenshot
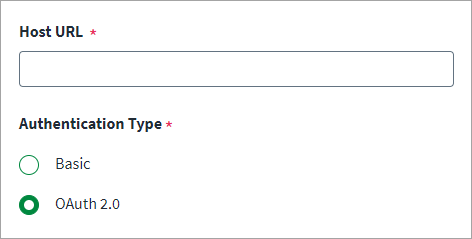
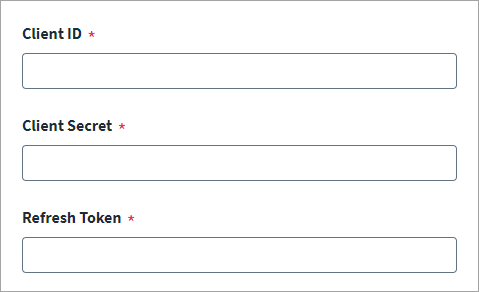
- Enter the Host URL for the ServiceNow instance that is used for communication.
- Select OAuth 2.0 as the Authentication Type.
- Enter the Client ID and Client Secret for OAuth 2.0 authentication.
-
Enter the Refresh Token for OAuth 2.0 authentication. For more information on creating an OAuth 2.0 profile on your ServiceNow instance, refer to ServiceNow: Create an endpoint for clients to access instance.
To create a refresh token use the following curl command:
$ curl -d "grant_type=password&client_id=be3aeb583ace210011c15b24a43e25d8
&client_secret=client_password
&username=admin&password=admin"
POST https://instancename.service-now.com/oauth_token.do
For more information, refer to ServiceNow: OAuth API request parameters.
-
Select Save.
OAuth 2.0 Authentication
Configure OAuth 2.0 authentication to secure your connection to the source. The connector supports both Client Credentials and Refresh Token grant types.
Screenshot
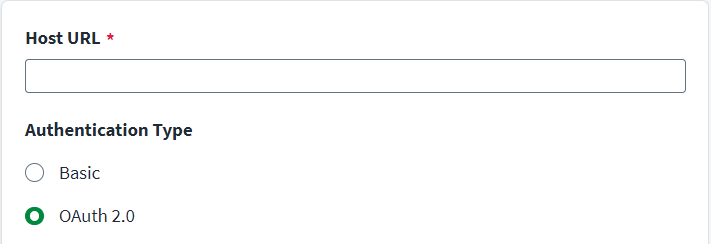
- Enter the Host URL for the ServiceNow instance that is used for communication.
- Select OAuth 2.0 as the authentication type.
-
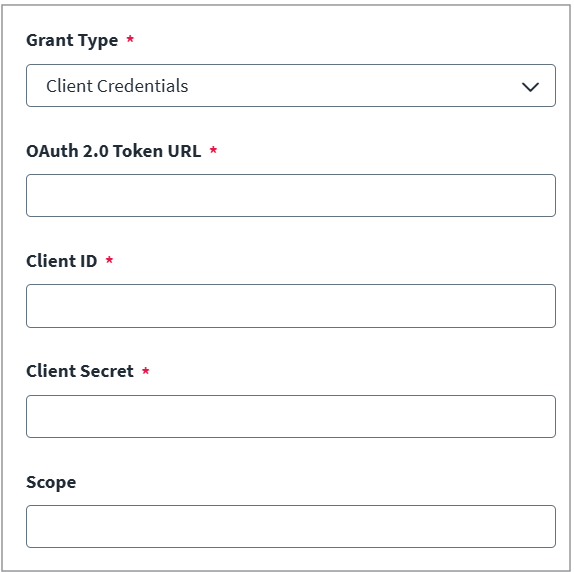
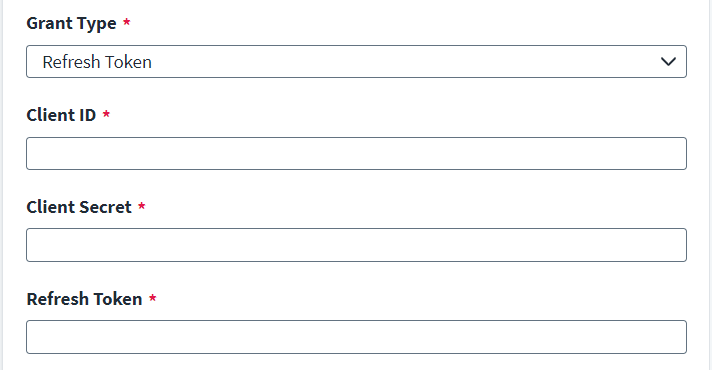
Select Client Credentials or Refresh Token from the Grant Type dropdown.
Client Credentials
Screenshot
Note
- The Okta External OIDC Provider in ServiceNow is supported with the Client Credentials Grant Type.
- ServiceNow also supports Microsoft Entra ID as an External OIDC Provider using the Client Credentials grant type.
- To configure OAuth 2.0 in the SailPoint Identity Governance connector, you must provide the OAuth 2.0 Token URL, Client ID, Client Secret, and Scope. These values are specific to the External OIDC Provider configured in ServiceNow. For example, Okta or Microsoft Entra ID.
- For configuration in ServiceNow, refer to Product Documentation | ServiceNow.
-
Enter the Oauth 2.0 Token URL. This URL depends on the External OIDC Provider configured in ServiceNow. For example:
- Okta External OIDC Provider:
{yourOktaDomain.com}/oauth2/{authorizationServerId}/v1/token- Microsoft Entra ID (Azure AD):
https://login.microsoftonline.com/{tenantId}/oauth2/v2.0/token- ServiceNow Inbound Client Credentials (local OAuth provider):
https://{yourInstanceName}.service-now.com/oauth_token.do -
Enter the Client ID.
- Enter the Client Secret.
- Enter the Scope.
- Select Save.
Refresh Token
Screenshot
Note
To configure OAuth 2.0 in the SailPoint Identity Governance connector, a Client ID, Client Secret, and Refresh Token are required. The Client ID, Client Secret, and Refresh Token are specific to the ServiceNow instance and configured while enabling OAuth 2.0 in your ServiceNow instance. Contact your ServiceNow Administrator to obtain the Client ID, Client Secret, and Refresh Token.
- Enter the Client ID and Client Secret.
-
Enter the Refresh Token. For more information on creating an OAuth 2.0 profile on your ServiceNow instance, refer to ServiceNow: Create an endpoint for clients to access instance.
To create a refresh token, use the following cURL command:
$ curl -d "grant_type=password&client_id=be3aeb583ace210011c15b24a43e25d8
&client_secret=client_password
&username=admin&password=admin"
POST https://instancename.service-now.com/oauth_token.do
For more information on token generation, refer to ServiceNow: OAuth API request parameter.
-
Select Save.
Configuration in ServiceNow for Client Credentials Grant Type
The SailPoint Identity Governance connector for ServiceNow supports External OpenID Connect (OIDC) Providers using the Client Credentials grant type. This includes providers such as Okta, Microsoft Entra ID (Azure AD), or ServiceNow's native OAuth provider.
Perform the following steps to configure the SailPoint Identity Governance connector for the ServiceNow application using the Client Credentials grant type:
Screenshot
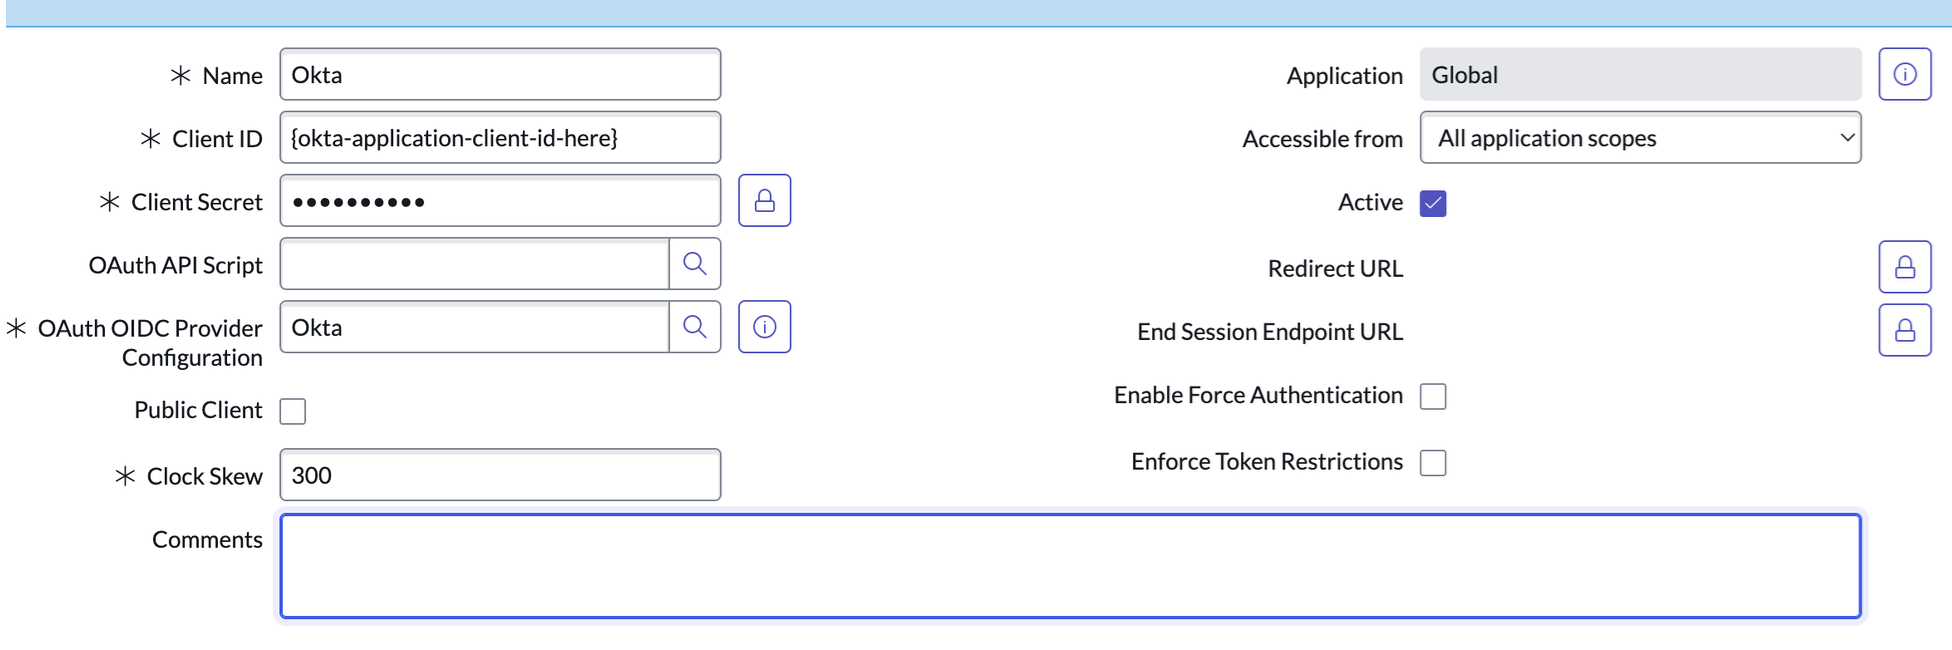
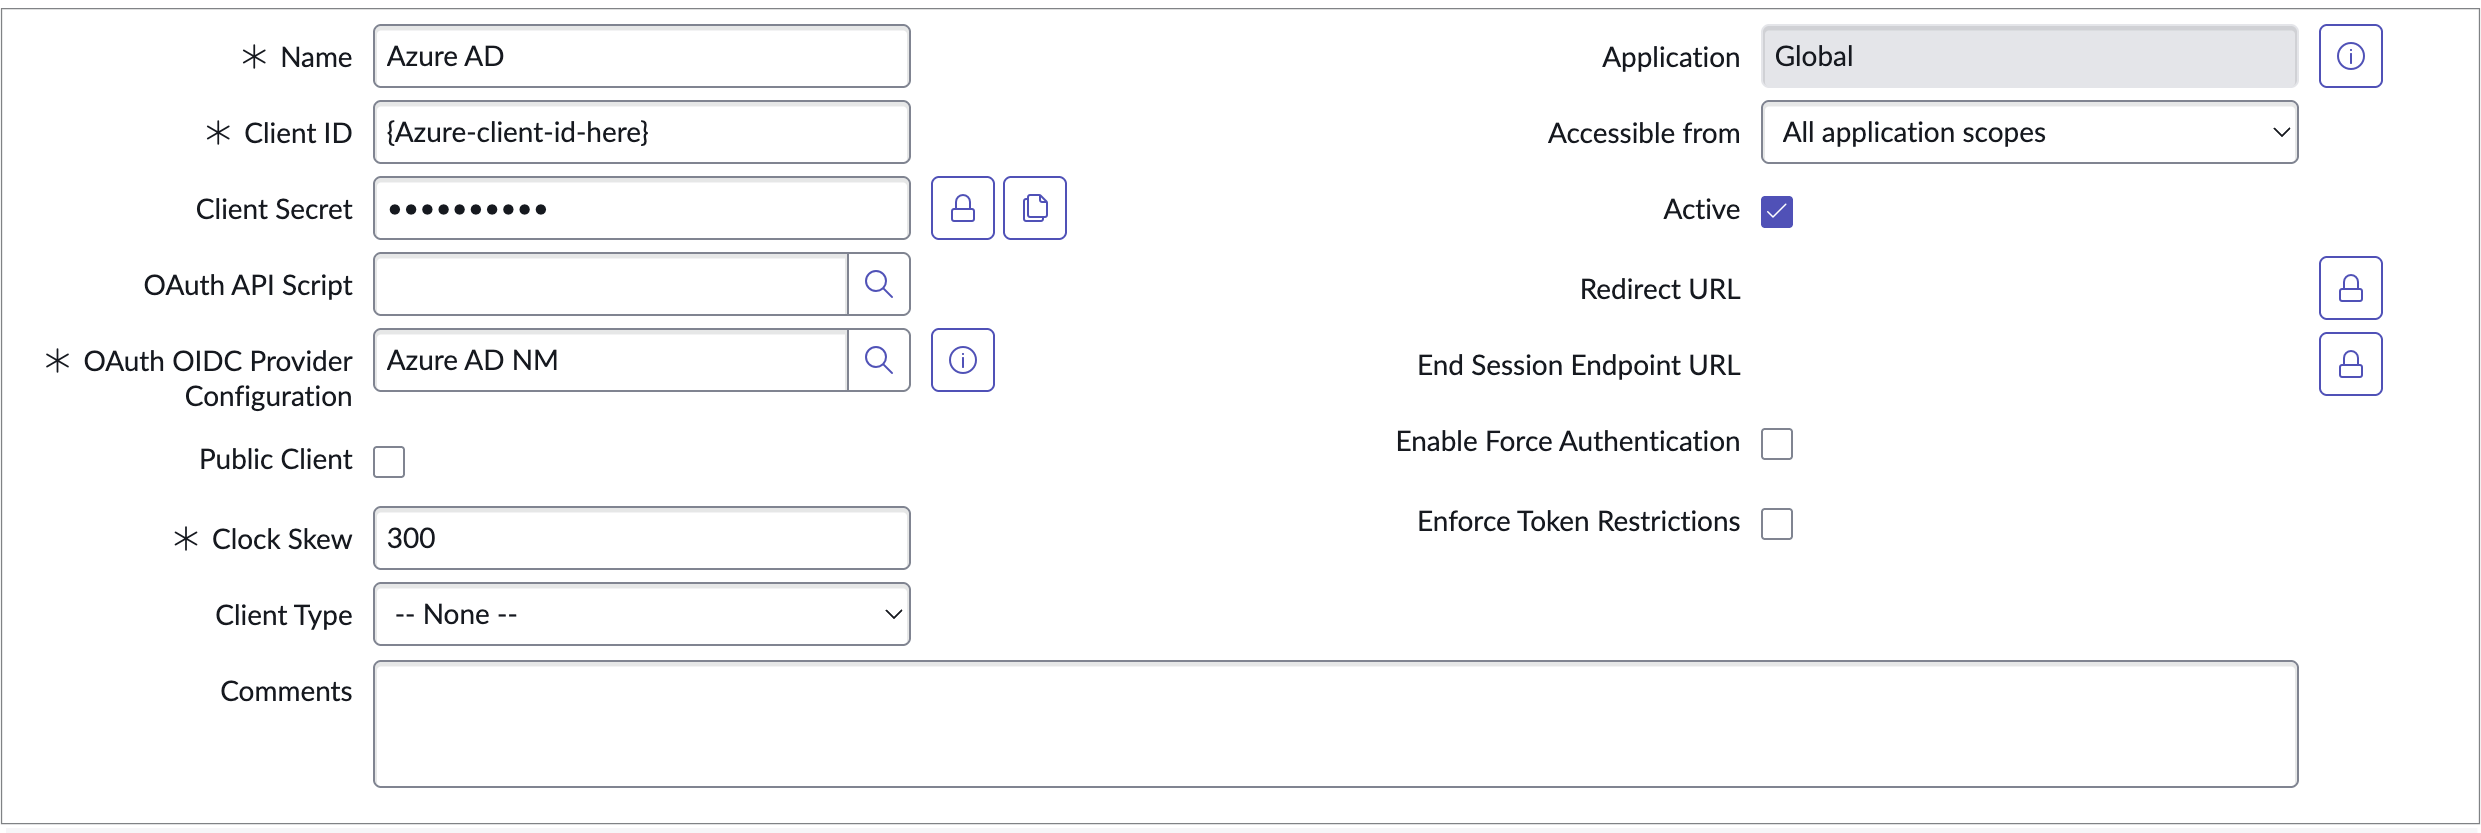
- Go to System OAuth > Application Registry and open the configuration for your External OIDC Provider. For example, Okta OIDC configuration or Entra ID OIDC configuration.
-
Enter the Client ID and Client Secret of the application registered in your External OIDC Provider.
Note
For Okta, enter the Authorization Server's Audience value. If required, enter this value in Client ID.
-
Open the OAuth OIDC Provider Configuration preview.
Note
The connector validates the received access token in ServiceNow using the OIDC Provider configuration.
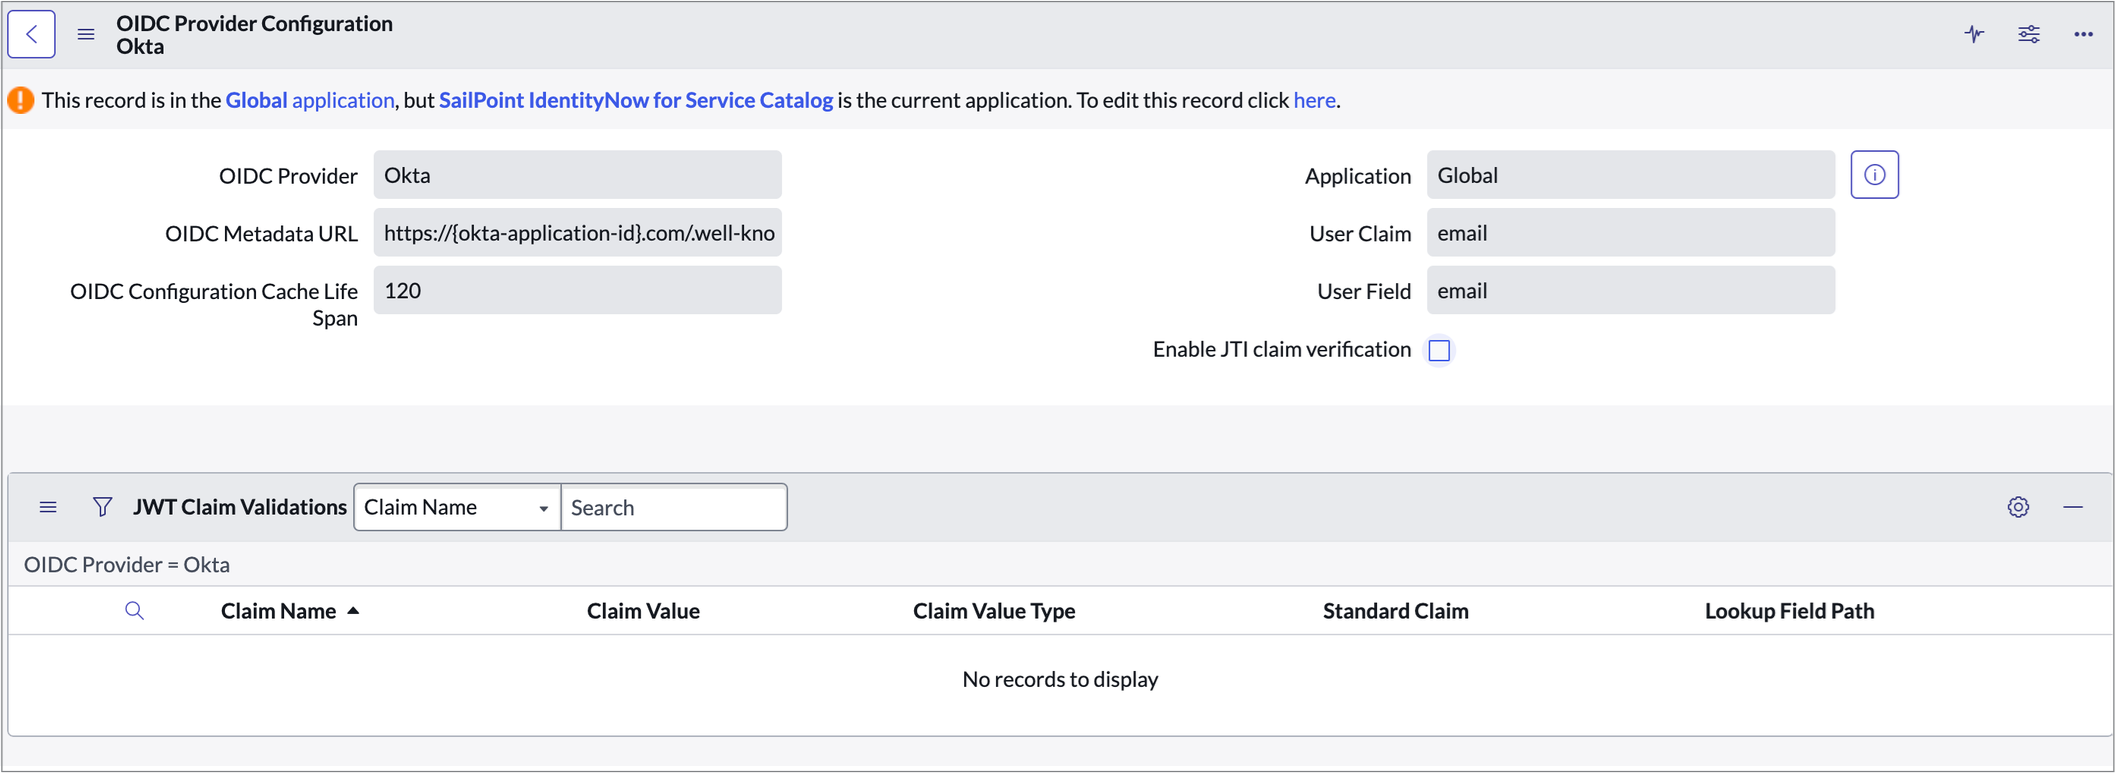
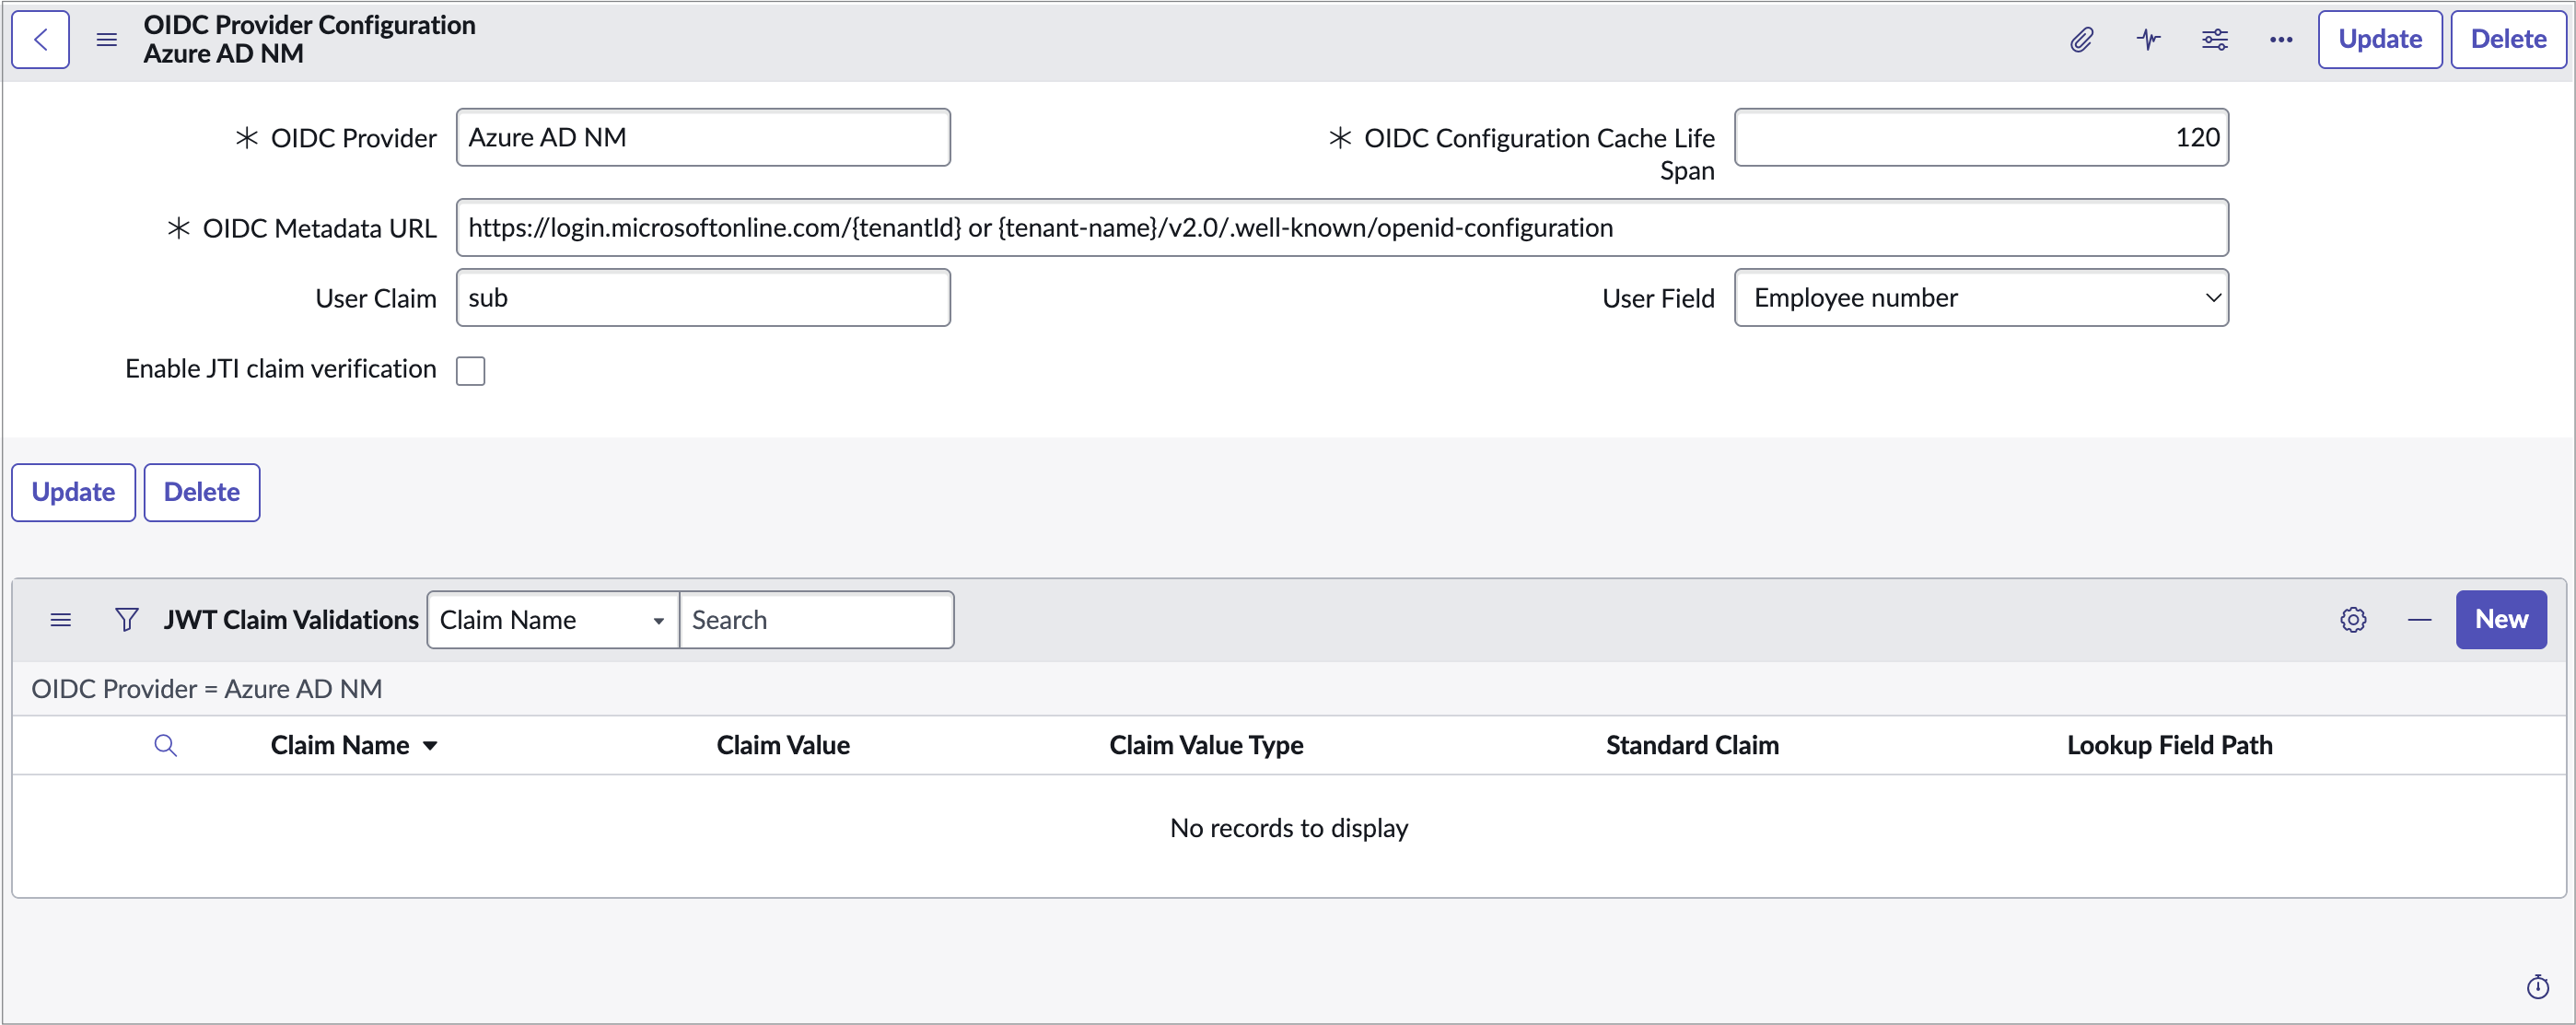
Provide the following details in the OAuth OIDC Provider Configuration for access token validation:
Screenshot
-
Enter the OIDC Metadata URL, where it returns the OpenID Connect metadata about your authorization server. This information is used to configure connector interaction with Okta or Entra ID. For example,
- Okta:
https://{yourOktaDomain.com}/oauth2/{authorizationServerId}/.well-known/openid-configuration- Microsoft Entra ID:
https://login.microsoftonline.com/{tenantId}/v2.0/.well-known/openid-configuration -
Update the User Claim and User Field mappings to correlate users and validate access to resource endpoints.
Note
The matched user should have the
x_sapo_iiq_connect.adminrole to execute governance application APIs. -
Deselect the Enable JTI claim verification checkbox.
- Update the required fields under JWT Claims Validations to validate the received access token based on the policies of your OIDC Provider.
Note
If you want to use the Client Credentials grant type for Inbound OAuth by native ServiceNow, refer to Client Credentials grant type for Inbound OAuth. Get the Client ID, Client Secret and Token URL value as per the OAuth Client application created on the ServiceNow instance.
-
Aggregation Settings
On the Aggregation Settings page, configure the filter settings, delta aggregation settings, and additional settings.
For more information about aggregation, refer to Loading Account Data.
Note
The SailPoint Identity Governance connector for ServiceNow aggregates sysparm_fields attributes during single account aggregation.
Filter Settings
Screenshot
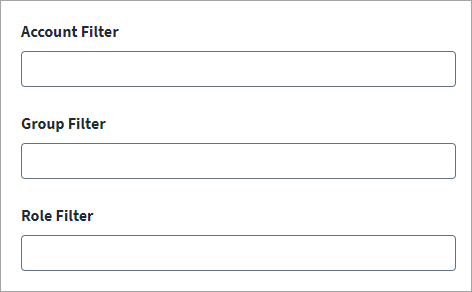
- Enter an Account Filter to filter accounts during aggregation. For multiple conditions, use
^. For example,active=true^locked_out=false. - Enter a Group Filter to filter groups during aggregation. For example,
active=true. - Enter a Role Filter to filter roles during aggregation. For example,
sys_Scope=Global.
ServiceNow Filter
To use the complex filters in ServiceNow, you must know the encoded query for the filter conditions that you can get from any list view in ServiceNow.
To retrieve a list view in ServiceNow complete the following:
- Create a filter on the ServiceNow managed system.
-
Right-click the filter link and select the Copy Query option. Enter the copied query (only) in Aggregation Filter Settings on the UI and select Save.
- For an AND operator, use
^. - For an OR operator, use
^OR.
For example, the following query will fetch all the active records with their respective locations, as mentioned in the encoded query:
active=true^location=dbf3b4790a0a0a6501a7673fb1b28f7f^ORlocation=dbf440100a0a0a65006618f752ee74b5 - For an AND operator, use
Delta Aggregation
The SailPoint Identity Governance connector for ServiceNow supports the delta aggregation of accounts.
Screenshot
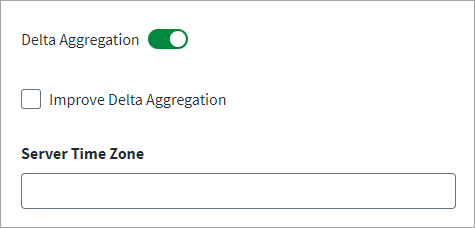
- Enable Delta Aggregation if you want to aggregate accounts that have changed since the last execution.
-
Select Improve Delta Aggregation to speed up the delta aggregation performance. This enables you to read only the deleted events (such as removing the group/role) of the user's connection from the x_sapo_iiq_connect_user_roles_and_group_deletes table.
Important
- To improve the delta aggregation, you must upgrade to ServiceNow SailPoint Identity Governance Connector version 1.0.6 or later from ServiceNow store.
- For improved delta aggregation performance, configure the Deleting With Table Cleanup Policies on the x_sapo_iiq_connect_user_roles_and_group_deletes table. For more information on table cleanup policies, refer to Deleting With Table Cleanup Policies.
Refer to Delta Aggregation for more information.
-
Enter the valid Server Time Zone for which the ServiceNow system server is configured. This timezone is used for performing delta aggregation. For example, you can use GMT or PST. If a time zone value is not provided the default value will be UTC.
Prerequisites
To support the delta aggregation, you must create the following Access Control List (ACL) in global scope and assign it to the x_sapo_iiq_connect.admin role:
| ACL | Type | Operation | Name | Attribute |
|---|---|---|---|---|
| sys_audit_delete | record | read | Audit Deleted Record [sys_audit_delete] |
None |
Delta Aggregation does not detect the deleted accounts. SailPoint recommends performing a full aggregation to detect the deleted accounts on ServiceNow.
Note
- The delta aggregation will not fail when the sys_user_grmember table returns bad data. For example, if a record in sys_user_grmember table had a missing value for Group or User column the delta aggregation completes operation.
- Delta aggregation is not supported for groups.
- If this ACL is not created, then deleted connections from the users are not detected during delta aggregation.
- For delta aggregation, your system reads the deleted user's connection from the sys_audit_delete table in SailPoint Identity Governance Connector version 1.0.5 or prior.
Partitioning Aggregation
The ServiceNow connector supports partitioning aggregation for accounts. The connector uses a User Partitioning Scheme made up of partitioning values to determine how it partitions accounts during aggregation.
Screenshot
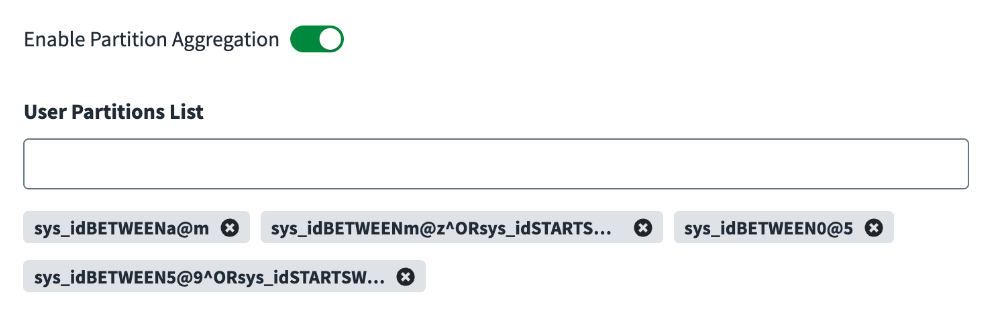
The default partitioning values available are as follows:
sys_idBETWEENa@msys_idBETWEENm@z^ORsys_idSTARTSWITHzsys_idBETWEEN0@5sys_idBETWEEN5@9^ORsys_idSTARTSWITH9
Note
If partitioning is enabled and custom User Partitions are not defined, the connector uses the default partitioning values.
The following is an example of custom partitioning:
employee_numberSTARTSWITH1, employee_numberSTARTSWITH2, employee_numberSTARTSWITH3, employee_numberSTARTSWITH4, employee_numberSTARTSWITH5, employee_numberSTARTSWITH6, employee_numberSTARTSWITH7, employee_numberSTARTSWITH8, employee_numberSTARTSWITH9, employee_numberSTARTSWITH0
To define a custom User Partition Scheme list:
- In the User Partitions List, define a partitioning value.
- Press Enter to add the partitioning value to a growing list. Repeat steps 1 and 2 as needed to build the User Partitioning Scheme.
- Select Save.
Additional Settings
Screenshot
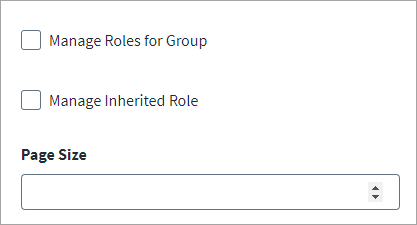
- Select Manage Roles for Group to aggregate roles by group.
- Select Manage Inherited Role to aggregate accounts where the inherited role is a member.
-
Enter the Page Size to specify the number of entries displayed on a page.
- Default: 50
- Minimum: 1
- Maximum: 1000
Note
Aggregation does not stop if the records received from the API response are less than the specified page size.
Advanced Settings
Use the advanced settings page to configure the following:
Account Unlocking
Screenshot
- Select Unlock Account while Enabling to unlock accounts while enabling them through the source.
Use Sys ID Reference
Screenshot
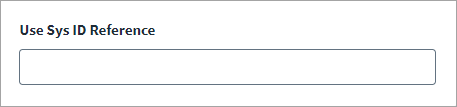
- Select Use Sys ID Reference and specify the user's reference field. Press Enter to add multiple entries. If the user's reference field is listed under this configuration, the user's record in SailPoint displays the Sys ID instead of the reference field's display name. For example, if you enter
active, users with a reference field of active now display the Sys ID.
Retry Error List
Screenshot
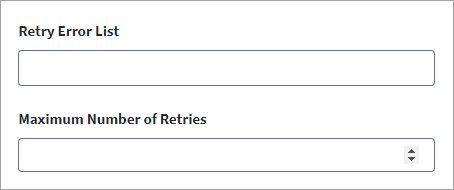
- Select Retry Error List and specify the error to retry during aggregation. Press Enter to add multiple entries.
- Select Maximum Number of Retries and enter the number of aggregation attempts.
Request Parameter Map
Screenshot
Note
For the SailPoint Identity Governance connector for ServiceNow, aggregation does not fail when big keys for sysparm_fields are provided in the Request Parameter Map for a ServiceNow key with a period (for example: manager.name or manager.user_name).
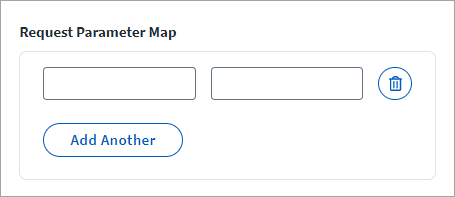
- In the Request Parameter Map fields, specify the additional request parameters that are added to the endpoint URL when the request is sent. For example, to use
sysparm_display_value, use the value astrue. To usesysparm_query_category, enter the value as per your requirement. - Select Add Another to add multiple entries.
- Select Save.
Review and Test
Perform a test to confirm the connection to SailPoint.
- Go to Review and Test.
-
Confirm that the entries in each field are correct.
If you note any mistakes, return to the section and make corrections.
-
Select Test Connection.
SailPoint Application Onboarding
SailPoint application onboarding enables you to easily onboard new applications and create sources following the successful onboarding of a discovery source. To use this feature, continue to Discovered Applications in the SailPoint user interface.
For more information, refer to Application Onboarding in the SailPoint SaaS documentation.
Activity Insights Settings
SailPoint pulls in activity data in the form of events like user logins, password changes, and content updates within the application. You can view an identity’s activity data within an application to discover trends for that user.
Important
Contact your SailPoint Customer Success Manager (CSM) for more information on Activity Insights. For more information on utilizing activity data, refer to Activity Insights.
Activity Insights Settings allows you to gather account information and activity data from ServiceNow Identity Governance. To enable Activity Insights for the ServiceNow Identity Governance application, refer to Prerequisites for more information.
To configure Activity Insights, complete the following:
Screenshot
- Go to Activity Insights Settings.
- Select Enable Activity Insights to view access to data insights on source and application activity such as logins and other app-specific events.
- Select Save.
Ensure the ServiceNow application has necessary scopes to utilize the Activity Insights. Refer to Required Permissions for the requested scopes for Activity Insights from ServiceNow.
Machine Identity Governance Settings
Note
Your organization must have SailPoint Agentic Fabric to use this feature. Contact your Customer Success team for more information. For more information, refer to SailPoint Agentic Fabric.
Screenshot
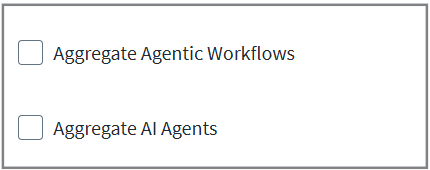
- Select Aggregate Agentic Workflows to include ServiceNow Agentic Workflows in governance.
- Select Aggregate AI Agents to include ServiceNow AI Agents in governance.
- Select Save.
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.