Connecting SailPoint and Microsoft Active Directory
To connect SailPoint with Microsoft Active Directory, perform the following tasks:
Adding the Source in SailPoint
To connect to SailPoint, perform the following steps. Once the connection is made, you can configure it to meet your company's needs.
Important
By default, the provisioning feature is disabled, and the connector only supports read-only operations. To support provisioning operations, you must manually enable the feature in the source configuration.
To configure a new source:
- Sign in to SailPoint.
- Go to Admin > Connections > Sources.
- Select Create New.
- Search for the connector by entering the name in the search box, and then select Configure.
- In the Source Name field, enter a unique and descriptive name for your source. Source names cannot exceed 128 characters.
- In the Description field, provide additional details about the source to help distinguish it from similar sources. This field allows a maximum of 2,000 characters.
- In the Source Owner field, begin typing the name of an owner. Matches appear after you type two or more letters. For more information, refer to Assigning a Source Owner.
-
Under Connection Type, select Direct Connection or Flat File.
- Direct Connection - A direct connection fetches data from the Virtual Appliance Cluster you choose as the application connector for the source. A direct connection configuration allows for real-time updates. For more information about configuring and deploying virtual appliances, refer to the Virtual Appliance Reference Guide.
- Flat File - Select the flat file if no connector is available, or if another system restricts the connection. This option allows only reading and aggregating data as a generic/delimited application. Provisioning activity is unsupported, and additional configuration pages like connection settings and aggregation settings are unavailable.
-
If you selected Direct Connection, in Virtual Appliance Cluster, select the virtual appliance cluster that will be used as the application connector for the source.
- (Optional) Select a governance group to grant its members source or role sub-admin level oversight of the source and its access. For more information, refer to Creating and Managing Governance Groups.
- If this source represents a primary system containing your organization's personnel records, select the Authoritative Source checkbox. For more information, refer to Creating Identity Profiles.
- Select Continue. The source is created, and you are navigated to the Source Setup > Base Configuration page. Continue to configure your connected source there.
Base Configuration
Provide the base configuration parameters. Information you entered in the Create New Source dialog is automatically entered into the fields in the Base Configuration page. You can edit this information if necessary.
- Enter a unique name and description for the source.
-
In the Source Owner dropdown list, select the identity that owns this source.
- To find a source owner, begin entering their name.
-
In the Virtual Appliance Cluster dropdown list, select the virtual appliance to use when communicating with your organization's systems. For more information, refer to SailPoint Virtual Appliances.
-
(Optional) If enabled for your organization, select the Use a Credential Provider checkbox to manage the source's authentication using a credential provider.
Note
To add a credential provider, go to Admin > Connections > Credential Providers. For more information about credential providers, refer to Credential Providers.
-
Configure the authentication to allow SailPoint to connect to the source. Refer to Forest Settings for more information.
-
(Optional) In the Governance Group for Source Management dropdown list, select a governance group to associate with this source. For more information about governance groups, refer to Associating Governance Groups with a Source.
-
(Optional) Choose whether to enable or disable provisioning for the source. Provisioning is disabled by default.
-
Enable Provisioning - Set the toggle to Enabled to allow the source to create, update, and deactivate accounts in the connected source system.
-
Disable Provisioning - Set the toggle to Disabled to disable provisioning for the source. Disabling provisioning will prevent the creation, updating, or deactivating of accounts on this source.
-
-
Select Save.
Forest Settings
An Active Directory forest is a set of all the directory partitions in a particular Active Directory instance that includes all domain, configuration, schema, and optional application information. Multiple forests can share the Active Directory responsibilities across an enterprise. To support a multi-forest configuration for the Active Directory source, configure multiple forests.
You can find the details of your existing configuration by using PowerShell commands. For more information, refer to Active Directory PowerShell Commands.
Screenshot
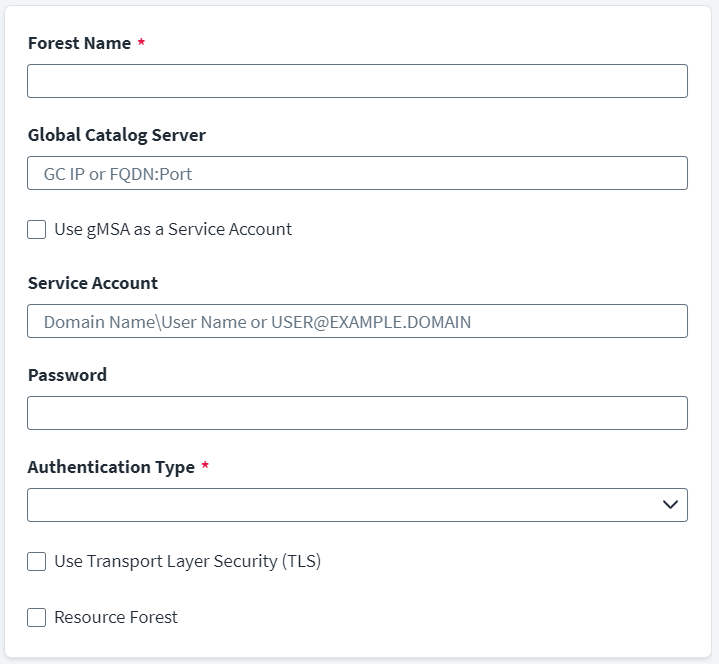
To configure forest settings, complete the following:
- Enter the Forest Name you want to set for a new forest to use in an organization. For example,
corp.exampleorg.com. -
(Optional) Enter the Global Catalog Server information using the following format:
IP address or FQDN:Port Number.Note
The Active Directory connector validates the configuration of global catalog during the test connection and health check operations.
-
(Optional) Select Use gMSA as a Service Account to use group Managed Service Account (gMSA) as a Service Account and provide the Service Account in UPN format. For more information, refer to Group Managed Service Accounts (gMSA) Cache Settings.
Note
Ensure you select Strong (SASL) as the Authentication Type. IQService configuration is also mandatory to use gMSA as a Service Account. For more information, refer to Configuring IQService to use gMSA as a service account for Active Directory.
-
(Optional) Enter the Service Account User with the required permissions using the following format:
Domain Name\User Name. - (Not required when Use gMSA as a Service Account is selected) Enter the Password for the service account.
-
(Optional) Select the Authentication Type from the drop-down menu.
- Simple - The account to authenticate is identified by the DN of the entry for that account, and the proof identity comes in the form of a password. SailPoint recommends that you Use Transport Layer Security (TLS) with simple authentication as this encrypts data during transit.
-
Strong (SASL) - Strong (SASL) authentication bind is performed, which uses kerberos or NTLM depending upon whether the SailPoint system is in a network (of service account domain) or outside network. Strong (SASL) has implicit security layer for data encryption.
For Strong (SASL) authentication to work, you must use the following format:
UserName@DNSDomainName.com. For more information, refer to Strong (SASL) Authentication Requirements.
-
(Not required when Use gMSA as a Service Account is selected) By default, the Use Transport Layer Security (TLS) checkbox is selected. When selected, you must also specify the TLS port in the Global Catalog Server field. For more information on TLS communication, refer to Securing the Active Directory Application.
- (Optional) Select the Resource Forest checkbox if this is a dedicated resource forest to manage Microsoft Exchange resources. For more information, refer to Active Directory Resource Forest Topology Exchange Management.
- (Optional) To create another forest, select Add Another + Add Forest Configuration and repeat the previous steps. To delete the Forest configuration that is not required, use the bin icon.
- Select Save.
Domain Settings
This page displays the list of forests that you have configured and enables you to configure domains.
Screenshot
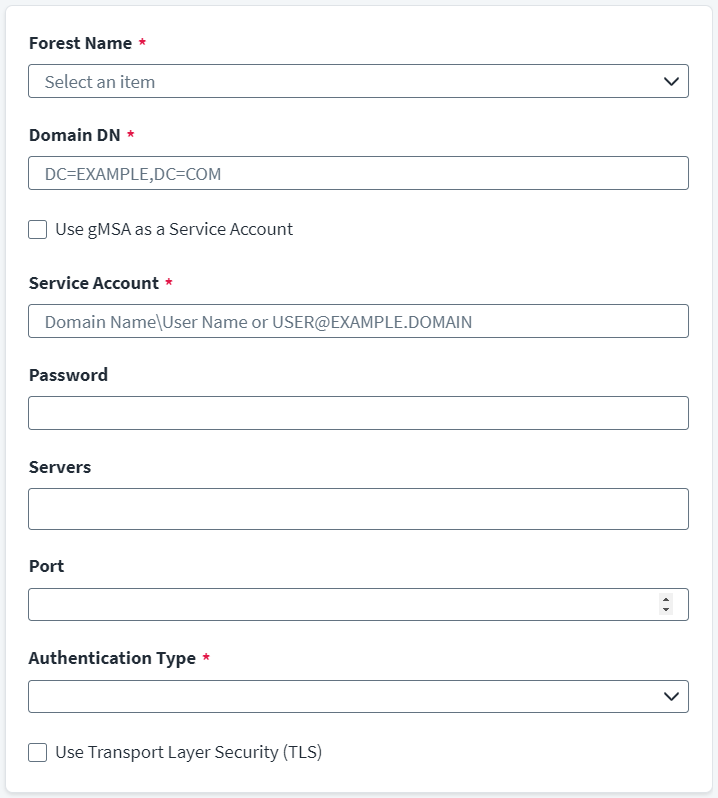
Important
To manage users, groups and their memberships across different domains, ensure there is a two-way trust between those domains. Also, ensure that IQService Service Account has the necessary permissions to access them.
To create and set up a new domain, complete the following:
- Select the Forest Name you want to configure for this domain from the drop-down menu.
- Enter the Domain DN.
-
(Optional) Select Use gMSA as a Service Account to use group Managed Service Account (gMSA) as a Service Account and provide the Service Account in UPN format.
Note
Ensure you select Strong (SASL) as the Authentication Type. IQService configuration is also mandatory to use gMSA as a service account. For more information, refer to Configuring IQService to use gMSA as a service account for Active Directory.
-
Enter the Service Account with the required permissions.
- When you are using Simple authentication, use:
Domain Name\User Name. - When you are using Strong (SASL) authentication, use:
UserName@DNSDomainName.com
- When you are using Simple authentication, use:
-
(Not required when Use gMSA as a Service Account is selected) Enter the Service Account Password.
-
(Optional) Enter the Servers information for the domain controller servers that you want to configure using the following format:
IP Address or FQDN. To configure multiple servers, enter a server and then press the Enter key. If you have configured two or more servers and the connection to the first server fails, the source attempts to bind to the next domain controller server in the list.Note
If you do not provide the IP or FQDN information, it is a server-less bind that requires the correct DNS configuration.
-
(Optional) Enter the Port number.
-
Select the Authentication Type from the drop-down menu.
- Simple - The account to authenticate is identified by the DN of the entry for that account, and the proof identity comes in the form of a password. SailPoint recommends that you Use Transport Layer Security (TLS) with simple authentication as this encrypts data during transit.
-
Strong (SASL) - Strong (SASL) authentication bind is performed, which uses kerberos or NTLM depending upon whether the SailPoint system is in a network (of service account domain) or outside network. Strong (SASL) has implicit security layer for data encryption.
For Strong (SASL) authentication to work, you must use the following format:
UserName@DNSDomainName.com. For more information, refer to Strong (SASL) Authentication Requirements.
-
(Not required when Use gMSA as a Service Account is selected) By default, the Use Transport Layer Security (TLS) checkbox is selected. When selected, you must specify the TLS port in the Port field. A valid SSL certificate must be placed on the virtual appliances in the following path:
/home/sailpoint/certificates/ad-resource.cer. For more information, refer to TLS Configuration on Virtual Appliances. - (Optional) To configure another domain, select Add Another + Add Domain Configuration and repeat the previous steps. To delete the Domain configuration that is not required, use the bin icon.
- Select Save.
Account and Group Settings
This page enables you to configure account, user, contact, managed service account, and group search options. The search DNs define the list of distinguished names of the containers along with other relevant attributes the define the scope for this connector. The search scope defines how far down in the tree to search from the base DN.
Note
DN/OU paths are case-sensitive.
Important
Connector-level partitioning for aggregation is supported for accounts only and does not apply to other object types.
If auto partitioning is not enabled, each of these search DNs is also considered as a partition for partitioned full aggregation. Users, Contacts, Managed Service Accounts, and Groups can have different sets of searchDNs to define different scope for each of them. In cases where the scope is not defined for Groups, it follows the Account's Search Scope. Defining one search DN to the minimum is required to successfully configure the connector.
User Search Scope
If the Group Membership Search DN attribute is not defined then the connector brings all the group memberships associated with the respective account, which are returned by APIs instead of falling back to the scope defined by Search DN.
Screenshot
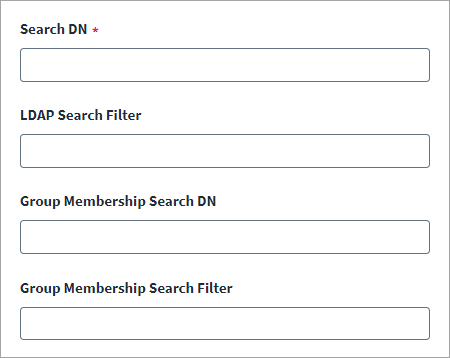
To configure the user's search, complete the following:
- In the Search DN field, enter the distinguished name of the domain or OU that defines the scope for users.
- (Optional) Specify an Iterate LDAP Search Filter string to limit the results returned by the search DN. For more information on the search syntax, refer to the Microsoft Active Directory: LDAP Syntax Filters wiki.
- (Optional) Specify Group Membership Search DN to determine the group membership of the users that you are loading. Separate multiple entries with a semicolon.
- (Optional) Specify a Group Membership Search Filter as an LDAP search filter string that applies while fetching the user's group membership.
- (Optional) Select Add Another + Add User Search Scope to create another search filter or select Delete to remove a search filter.
- Once you have configured all the search scopes, select Save.
Contact Search Scope
Screenshot
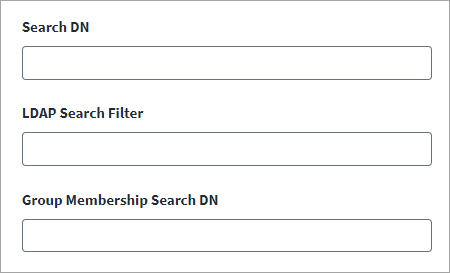
To configure the contact's search, complete the following:
- (Optional) In the Search DN field, enter the distinguished name of the domain or OU that defines the scope for contacts.
- (Optional) Specify an Iterate LDAP Search Filter string to limit the results returned by the search DN. For more information on the search syntax, refer to the Microsoft Active Directory: LDAP Syntax Filters wiki.
- (Optional) Specify Group Membership Search DN to determine the group membership of the contacts that you are loading. Separate multiple entries with a semicolon.
- (Optional) Select Add Another + Add Contact Search Scope to create another search filter or select Delete to remove a search filter.
- Once you have configured all the search scopes, select Save.
Managed Service Account Search Scope
Screenshot
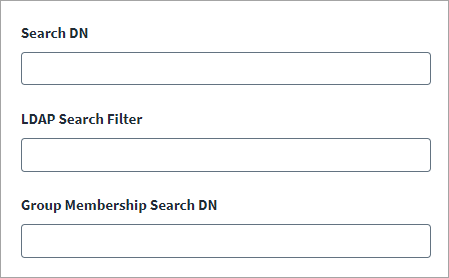
To configure the managed service account's search, complete the following:
- (Optional) In the Search DN field, enter the distinguished name of the domain or OU that defines the scope for the managed service account.
- (Optional) Specify an Iterate LDAP Search Filter string to limit the results returned by the search DN. For more information on the search syntax, refer to the Microsoft Active Directory: LDAP Syntax Filters wiki.
- (Optional) Specify Group Membership Search DN to determine the group membership of the managed service accounts that you are loading. Separate multiple entries with a semicolon.
- (Optional) Select Add Another + Add Managed Service Account Search Scope to create another search filter or select Delete to remove a search filter.
- Once you have configured all the search scopes, select Save.
Group Search Scope
Note
If you don't define the search scope for Groups, the connector uses the same search scope it uses for Accounts.
Screenshot
To configure the group's search, complete the following:
- (Optional) In the Search DN field, enter the distinguished name of a container for a group to define the search scope of groups.
- (Optional) Specify an Iterate LDAP Search Filter string to limit the results returned by the search DN.
- (Optional) Select Add Another + Add Group Search Scope to create another search filter or select Delete to remove a search filter.
- Once you have configured all the search scopes, select Save.
IQService Settings
Install IQService to support execution of provisioning operations and native rules. IQService is required by the Active Directory connector for all provisioning, and for reading certain fields from a user's entry, including Terminal Services and Lync attributes.
For more information, refer to IQService Settings.
Exchange Settings
Use this page to configure the exchange server.
Screenshot
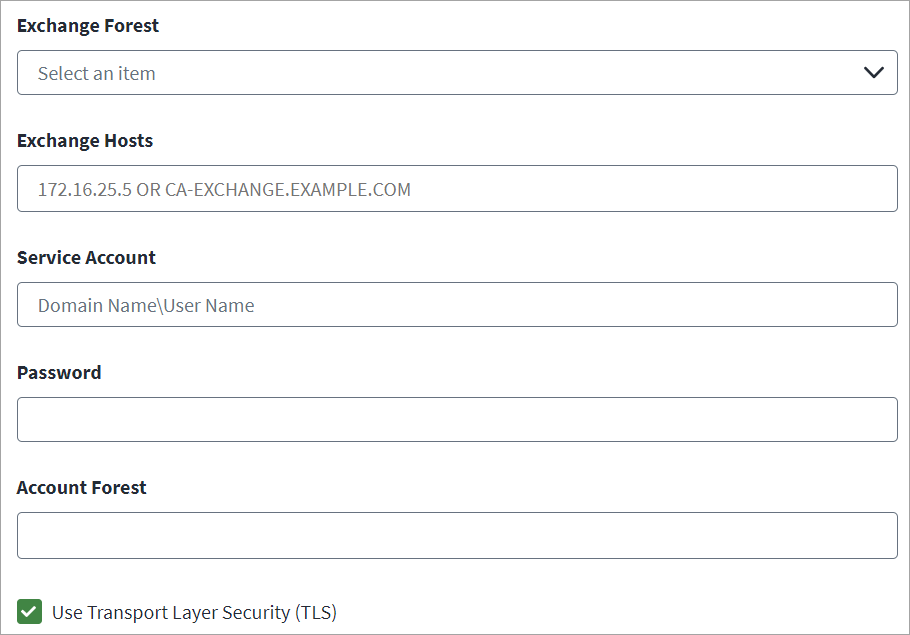
To configure the exchange settings, complete the following:
-
(Optional) Select the Exchange Forest where the exchange servers are installed from the drop-down menu.
Important
If you select an exchange forest, the Exchange Host, Service Account, Password, and Account Forest fields are mandatory.
-
(Optional) In the Exchange Host field, enter the exchange host name or IP address of the system where IQService is installed.
- (Optional) Enter the Service Account user with the required permissions using the following format:
Domain Name\User Name. - (Optional) Enter the Service Account Password.
- (Optional) In the Account Forest field, enter the name of the account's or user's forests served by this exchange server.
- (Optional) By default, the Use Transport Layer Security (TLS) checkbox is selected.
- (Optional) To configure another exchange server, select Add Another + Add Exchange Configuration and repeat the previous steps.
- Select Save.
Note
If your user belongs to a particular domain, ensure to mention that forest name in the accountForestList.
Review and Test
Perform a test to confirm the connection to SailPoint.
- Go to Review and Test.
-
Confirm that the entries in each field are correct.
If you note any mistakes, return to the section and make corrections.
-
Select Test Connection.
SailPoint Application Onboarding
SailPoint application onboarding enables you to easily onboard new applications and create sources following the successful onboarding of a discovery source. To use this feature, continue to Discovered Applications in the SailPoint user interface.
For more information, refer to Application Onboarding in the SailPoint SaaS documentation.
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.