Troubleshooting
If you encounter any of the following issues or errors, SailPoint recommends that you follow the guidance provided below to resolve the error before contacting SailPoint Support.
For issues or errors that are not addressed in this connector guide, refer to the following resources for troubleshooting information:
- SailPoint Identity Services Documentation
- SailPoint Support Knowledge Base
- SailPoint Developer Community
Group Fetch Requests Fail Immediately After Creation
Group fetch requests may fail immediately after creation because cloud synchronization delays prevent the newly created group from being reflected.
Resolution: Add the createGroupTimelag attribute via the SailPoint REST API to specify a delay (in seconds) between creating and fetching the group. The default delay is 5 seconds and can be modified as needed. For more information, refer to createAccountTimelag.
Exception Occurred in Iterate Objects - populateRiskyUsersDetails
This error occurs when the Risky User feature is disabled in Microsoft Entra ID.
Resolution: Choose one of the following solutions to complete account aggregation:
Option 1: Delete these four attributes from the connector's Account Schema:
- riskLevel
- riskState
- riskDetail
- riskLastUpdatedDateTime
Option 2: Grant the necessary permission to read Risky User Alerts in Entra ID.
Account Creation Is Slow During Single Account Aggregation
This performance issue occurs because the connector makes numerous API calls to the Microsoft Graph API to retrieve Privileged Identity Management (PIM) membership data associated with the account.
Resolution: To improve performance, you can configure the connector to skip the retrieval of PIM membership data during the initial account creation. Set skipPIMMembershipOnCreateAccount parameter value to true. For more information, refer to skipPIMMembershipOnCreateAccount.
Provisioning Fails With a 409 Conflict Error for License Assignment Requests
When a provisioning plan includes requests to add multiple assignedLicence values for a single user, the operation fails returning an API error code of 409. This occurs because the Microsoft cannot process simultaneous license assignment requests for the same user, treating it as a concurrency conflict.
Resolution: To resolve this issue, you can configure the connector to automatically retry the failed license assignment request. This allows a brief delay for the Microsoft tenant to process the initial request before the connector attempts the operation again. For more information, refer to Configuring Errors and Retries.
Authentication Fails With "AADSTS70011 Invalid Scope" During Provisioning
When attempting to provision Exchange Online, the operation fails with an error message:
AADSTS70011 Invalid scope. The scope has to be of the form "[https://resourceUrl/.default]""Mitigation: change the scope to be as expectedA configuration issue is preventing authentication - check the error message from the server for details.
Resolution: To resolve this authentication failure, you must verify that the application registration and permissions are correctly configured in both the source and Azure AD.
Follow these steps:
-
Verify App ID and Certificate Alignment
- Confirm that the certificate used for authentication is uploaded to the correct Azure AD Application Registration Portal.
- Ensure the Client ID configured in the source matches the Application (client) ID of the Azure AD application where the certificate is uploaded. A mismatch is a common cause of this failure.
-
Confirm Permissions
- In Azure AD, go to the App Registration Portal used for Exchange Online.
- Verify that the application has been granted the Exchange Administrator role and
Exchange.ManageAsApppermission.
Entitlement Aggregation Fails With a sailpoint.object.ManagedAttribute Insert Error
Entitlements having emojis in its name cause the issue during its insertion/processing in the database.
Resolution: Remove the emojis in the entitlements name on the managed system.
Unable to Aggregate Azure PIM Role Membership
Resolution: To successfully aggregate Azure PIM role memberships, ensure that the Owner or User Access Administrator role is assigned to the Tenant Root Group/Subscription level within the Azure AD portal.
Exchange Online Provisioning Fails With "Invalid Provider Type Specified"
When the Manage Exchange Online checkbox is selected, provisioning fails with the following error:
Exception during Connect-ExchangeOnline: System.Management.Automation.RemoteException: Invalid provider type specified.
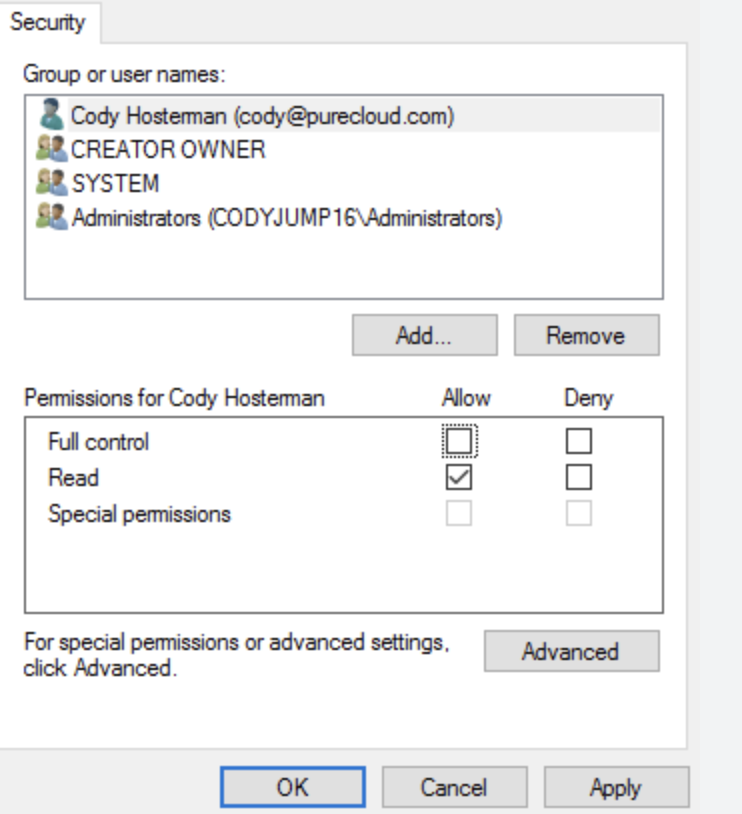
This error indicates that the IQService, operating under a specific service account, lacks the necessary permissions to access the private key of the certificate used for connecting to Exchange Online.
Resolution:
To resolve this, grant the IQService's service account full control over the certificate's private key.
Screenshot
-
Open the Certificate Manager:
- Press Win + R to open the Run dialog.
- Type
certmgr.mscand press Enter.
-
Go to Personal > Certificates.
-
Select and right-click the certificate.
-
Go to All Tasks, and then select Manage Private Keys.
-
In the Permissions dialog box, click Add.
-
Enter the name of the service account under which IQService is running.
-
For the added service account, ensure Full control and Read permissions are granted.
-
Click Apply, then OK to save the changes.
-
Restart IQService for the new permissions to take effect.
Test Connection Fails When the Manage Exchange Online Checkbox Is Selected
The test connection fails and displays the following error:
Error returned from IQService. One or more errors occurred
Resolution: Complete the following: Verify that all of the prerequisites for the Microsoft Exchange Online Mailbox attributes are in place. For more information, refer to Prerequisites. Once you have verified the prerequisites have been met, run the following PowerShell command on the IQService machine to verify connectivity:
Test Connection Fails
Test Connection fails with the following error message when Microsoft Entra ID application is checked for SAML Bearer Assertion Grant Type:
OAuth2Exception [toString()=connector.common.oauth2.OAuth2Exception: Unable to generate access token. Response returned:
{"error":"invalid_grant","error_description":"AADSTS50008: The SAML token is invalid.\r\nTrace ID: a74df376-3ede-4c17-ba34-b352079e3300\r\nCorrelation ID: f8c370ec-4ef6-48a4-a393-0297a5ce3b20\r\nTimestamp: 2020-05-04 05:58:16Z","error_codes":[50008],"timestamp":"2020-05-04 05:58:16Z","trace_id":"a74df376-3ede-4c17-ba34-b352079e3300","correlation_id":"f8c370ec-4ef6-48a4-a393-0297a5ce3b20","error_uri":"https://login.microsoftonline.com/error?code=50008"}
]
Resolution: Verify if the time zone of ADFS machine is in synchronize with Azure time zone, that is, UTC. If not, change the ADFS machine time and re-start the ADFS services.
Test Connection / Account Aggregation Fails
Test Connection/ Account Aggregation fails with the following error message when Microsoft Entra ID application is checked for SAML Bearer Assertion Grant Type:
Error - invalid_grant: AADSTS5000811: Unable to verify token signature. The signing key identifier does not match any valid registered keys.
Resolution: Microsoft recommends to execute the following command from PowerShell running on ADFS server to manually renew token signing certificates:
Provisioning of Exchange Attribute Fails
Provisioning of Exchange attribute fails if account aggregation is in progress. Exchange online module supports maximum three sessions per user hence limiting the parallel operations in execution.
Resolution: Connector uses all the three sessions while performing aggregation. Hence to improve the aggregation performance no other operation must be performed using the configured user.
Account Aggregation Fails
When new attributes are added in account schema, Get Object / Account Aggregation fails with the following error message:
Error - 501 This operation target is not yet supported
Resolution: Microsoft Graph API supports some of the following attributes only for retrieving single user:
aboutMebirthdayhireDateinterestsmySitepastProjectspreferredNameresponsibilitiesschoolsskillsmailboxSettings
The addition of these attributes while retrieving collection of users leads to aggregation failure. Verify if the newly added attributes are in the list of these attributes and remove them from the schema.
Unexpected Errors Occur During Provisioning
An unexpected 'PrimitiveValue' node was found when reading from the JSON reader. A 'StartArray' node was expected.
Or
Invalid value for the Property
Resolution: Ensure that the data type of the attribute is added correctly to the provisioning policy. For more information, refer to the Microsoft Documentation.
Note
For update account operation, the businessPhones attribute accepts only single value with the data type as String collection.
Delta Aggregation With the userFilters Scope Fails With an Aggregation Timeout
Resolution: Many users could be out of the defined userFilter scope. Add the returnNullROAfter attribute using SailPoint API. Value is number of the out of scope users, the default value is 50.
Note
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
Account Fetch After Create Request May Fail Due to Cloud Delay
Resolution: Add the createAccountTimelag attribute, using the SailPoint REST API, to create a delay (in seconds) that will occur after the create request and before the connector fetches the account. The time can be modified as needed. The value could be number of the seconds, the default value is 20 seconds.
Note
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
Full Account Aggregation Takes a Long Time to Complete
In cases where the entitlement attributes (like groups, roles, and servicePrincipals) are present in the account schema, add the following entry in the source XML using the SailPoint REST APIs max-thread-account-membership with a value of 6, 8, or 10 in accordance with your requirements. The default value is 4.
Note
This entry is not valid/used during delta aggregation.
For example:
key: max-thread-account-membership
value: 8
Note
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
Full Account Aggregation Is Slow and Pulls in Unwanted Schema Attributes
Resolution: Remove the unwanted attributes from schema using the SailPoint REST APIs.
Note
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
-
Use the following API to get the account schema:
curl --location 'https://<tenanturl>.api.cloud.sailpoint.com/v3/sources/<sourceID>/schemas/<schemaID>' \ --header 'Authorization: Bearer eyJhbGc'For example,
curl --location'https://tenanturl.api.cloud.sailpoint.com/v3/sources/2fb65f6328cf/schemas/f2bdf68e851' \ --header 'Authorization: Bearer eyJhbGc' -
Get the response from the above API and remove the unwanted attributes and set the body in the following PUT API:
PUT API Reference
curl --location --request PUT 'https://tenanturl.api.cloud.sailpoint.com/v3/sources/2fb65f6328cf43a2a95b49cdeb0778dd/schemas/f2bdf68fec764156b58ba41520cbe851' \ --header 'Content-Type: application/json' \ --header 'Authorization: Bearer acbdEFG123' \ --data-raw '{ "id": "f2bdf68fec", "nativeObjectType": "User", "identityAttribute": "distinguishedName", "displayAttribute": "sAMAccountName", "hierarchyAttribute": null, "includePermissions": false, "features": [], "configuration": {}, "attributes": [ { "name": "businessCategory", "type": "STRING", "schema": null, "description": "business category", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "carLicense", "type": "STRING", "schema": null, "description": "vehicle license or registration plate", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "cn", "type": "STRING", "schema": null, "description": "common name(s) for which the entity is known by", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "departmentNumber", "type": "STRING", "schema": null, "description": "identifies a department within an organization", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "destinationIndicator", "type": "STRING", "schema": null, "description": "destination indicator", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "displayName", "type": "STRING", "schema": null, "description": "preferred name to be used when displaying entries", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "distinguishedName", "type": "STRING", "schema": null, "description": "distinguished name for which the entity is known by", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "employeeNumber", "type": "STRING", "schema": null, "description": "numerically identifies an employee within an organization", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "employeeType", "type": "STRING", "schema": null, "description": "type of employment for a person", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "facsimileTelephoneNumber", "type": "STRING", "schema": null, "description": "Facsimile (Fax) Telephone Number", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "givenName", "type": "STRING", "schema": null, "description": "first name(s) for which the entity is known by", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "homePhone", "type": "STRING", "schema": null, "description": "home telephone number", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "homePostalAddress", "type": "STRING", "schema": null, "description": "home postal address", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "initials", "type": "STRING", "schema": null, "description": "initials of some or all of names, but not the surname(s).", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "internationaliSDNNumber", "type": "STRING", "schema": null, "description": "international ISDN number", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "l", "type": "STRING", "schema": null, "description": "city", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "mail", "type": "STRING", "schema": null, "description": "RFC822 Mailbox", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "manager", "type": "STRING", "schema": null, "description": "DN of manager", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "mobile", "type": "STRING", "schema": null, "description": "mobile telephone number", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "o", "type": "STRING", "schema": null, "description": "organization this object belongs to", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "ou", "type": "STRING", "schema": null, "description": "organizational unit this object belongs to", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "pager", "type": "STRING", "schema": null, "description": "pager telephone number", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "physicalDeliveryOfficeName", "type": "STRING", "schema": null, "description": "Physical Delivery Office Name", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "postOfficeBox", "type": "STRING", "schema": null, "description": "Post Office Box", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "postalAddress", "type": "STRING", "schema": null, "description": "postal address", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "postalCode", "type": "STRING", "schema": null, "description": "postal code", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "preferredDeliveryMethod", "type": "STRING", "schema": null, "description": "preferred delivery method", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "preferredLanguage", "type": "STRING", "schema": null, "description": "preferred written or spoken language for a person", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "registeredAddress", "type": "STRING", "schema": null, "description": "registered postal address", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "roomNumber", "type": "STRING", "schema": null, "description": "room number", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "secretary", "type": "STRING", "schema": null, "description": "DN of secretary", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "seeAlso", "type": "STRING", "schema": null, "description": "DN of related object", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "sn", "type": "STRING", "schema": null, "description": "last (family) name(s) for which the entity is known by", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "st", "type": "STRING", "schema": null, "description": "state or province which this object resides in", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "street", "type": "STRING", "schema": null, "description": "street address of this object", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "telephoneNumber", "type": "STRING", "schema": null, "description": "Telephone Number", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "teletexTerminalIdentifier", "type": "STRING", "schema": null, "description": "Teletex Terminal Identifier", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "telexNumber", "type": "STRING", "schema": null, "description": "Telex Number", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "title", "type": "STRING", "schema": null, "description": "title associated with the entity", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "uid", "type": "STRING", "schema": null, "description": "user identifier", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "objectClass", "type": "STRING", "schema": null, "description": "object classes of the entity", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "memberOf", "type": "STRING", "schema": { "type": "CONNECTOR_SCHEMA", "id": "361378963168", "name": "group" }, "description": "Group Membership", "isMulti": true, "isEntitlement": true, "isGroup": true }, { "name": "objectSid", "type": "STRING", "schema": null, "description": "Windows Security Identifier", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "objectguid", "type": "STRING", "schema": null, "description": "Object globally unique identifier ", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "sAMAccountName", "type": "STRING", "schema": null, "description": "sAMAccountName", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "primaryGroupID", "type": "STRING", "schema": null, "description": "RID of users primary group", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "primaryGroupDN", "type": "STRING", "schema": null, "description": "DN of users primary group", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "accountFlags", "type": "STRING", "schema": null, "description": "List of the flags enabled on an account", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "department", "type": "STRING", "schema": null, "description": "User'\''s department", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "msNPCallingStationID", "type": "STRING", "schema": null, "description": "CallingStationID", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "msRADIUSFramedRoute", "type": "STRING", "schema": null, "description": "Static Routes for Dial-In connection", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "msNPAllowDialin", "type": "STRING", "schema": null, "description": "Is dial-in allowed", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "msRADIUSCallbackNumber", "type": "STRING", "schema": null, "description": "Callback Number", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "msRADIUSFramedIPAddress", "type": "STRING", "schema": null, "description": "Define Static IP Address", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "mailNickname", "type": "STRING", "schema": null, "description": "Exchange Alias", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "homeMDB", "type": "STRING", "schema": null, "description": "Exchange Database", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "msExchHideFromAddressLists", "type": "STRING", "schema": null, "description": "Hide from Exchange address lists", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "msRTCSIP-UserEnabled", "type": "BOOLEAN", "schema": null, "description": "User enabled for Lync Server", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "SipAddress", "type": "STRING", "schema": null, "description": "Lync sipAddress", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "RegistrarPool", "type": "STRING", "schema": null, "description": "Lync Registrar pool", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "LyncPinSet", "type": "STRING", "schema": null, "description": "Lync user pin set status", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "LyncPinLockedOut", "type": "STRING", "schema": null, "description": "Lync user pin lock status", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "pwdLastSet", "type": "STRING", "schema": null, "description": "Time of last password reset", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "msDS-PrincipalName", "type": "STRING", "schema": null, "description": "Name of the entity in the format \"NetBIOS domain name\\sAMAccountName\"", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "userPrincipalName", "type": "STRING", "schema": null, "description": "The unique name of the entity within the domain, in the format \"name@domain\"", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "externalEmailAddress", "type": "STRING", "schema": null, "description": "External email address of Mail User", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "dNSHostName", "type": "STRING", "schema": null, "description": "Fully Qualified Domain Name for the Service Account", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "msDS-ManagedPasswordInterval", "type": "STRING", "schema": null, "description": "Password change interval in days for the Managed Service Account", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "msDS-SupportedEncryptionTypes", "type": "STRING", "schema": null, "description": "Supported Encryption Types for the Managed Service Account", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "msDS-GroupMSAMembership", "type": "STRING", "schema": null, "description": "Principals allowed to use Group Managed Service Account", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "msDS-AllowedToActOnBehalfOfOtherIdentity", "type": "STRING", "schema": null, "description": "Principals that can act on the behalf of Group Managed Service Account", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "servicePrincipalName", "type": "STRING", "schema": null, "description": "Service principal names for the Service Account", "isMulti": true, "isEntitlement": false, "isGroup": false }, { "name": "objectType", "type": "STRING", "schema": null, "description": "Type of Active Directory object", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "shadowAccountDN", "type": "STRING", "schema": null, "description": "DistinguishedName of the Linked Mailbox shadow account", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "shadowAccountGuid", "type": "STRING", "schema": null, "description": "ObjectGuid of the Linked Mailbox shadow account", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "msExchRecipientTypeDetails", "type": "STRING", "schema": null, "description": "Type of the Microsoft Exchange recipient object", "isMulti": false, "isEntitlement": false, "isGroup": false }, { "name": "memberOfSharedMailbox", "type": "STRING", "schema": { "type": "CONNECTOR_SCHEMA", "id": "dd43485", "name": "sharedMailbox" }, "description": "List of Shared Mailboxes to which user has permissions", "isMulti": true, "isEntitlement": true, "isGroup": true } ], "id": "f2bdf68f", "name": "account", "created": "2023-10-09T17:22:35.174Z", "modified": "2023-10-09T17:22:35.174Z" }'
Account Aggregation Fails With Duplicate 'ImmutableId' and 'immutableId' Keys
This error occurs when there is a duplication of attribute immutableID in the ResourceObject(RO).
Resolution: Add the entry skipProcessLegacyIdentifiers in the source XML using SailPoint REST API and set the value as true. By default this value is false.
Note
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
Account Aggregation Gets Stuck for Days When Manage Exchange Online Is Enabled
Since there is no timeout limit set for the IQService's response, the current setting defaults to 0. This means it will wait indefinitely if IQService doesn't respond.
Resolution: Add the following entry to the source XML using PATCH:
The value is in seconds and depends on how long IQService takes to fetch the sharedMailbox AND/OR EXO attributes.
Note
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
SharedMailbox Displays Alphanumeric Values Instead of a User-Friendly Display Name
Resolution: If SharedMailbox displays Globally Unique Identifier (GUID) value instead of a readable DisplayName, add the useDisplayNameForSharedMailbox entry to the source XML using PATCH and set the value to true. For example,
Note
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
Numeric Value Displayed for SPN Account Names
When managing users and Service Principal Names (SPNs) as accounts under a single source, if the displayName attribute of the Account Schema is set to UserPrincipalName, you may encounter numeric values for SPN accounts instead of readable names.
Resolution: To display the correct SPN displayName, ensure that the mapSPNDisplayNameToUPN is added to the source XML using PATCH and set the value to true. For example,
Note
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
Property usageLocation Is Invalid
The connector may return a 400 error or a message stating "Property usageLocation is invalid" when attempting to remove the usageLocation attribute.
Resolution:
To resolve this, configure the connector to wait after license operations are performed, ensuring they are fully processed before the connector attempts to modify the usageLocation. To do so, add the waitAfterLicenseOperations attribute to the source configuration using the following REST API PATCH call :
Endpoint: PATCH /v3/sources/:id
Body:
Note
For more information on SailPoint's REST APIs, refer to Best Practices: REST API Authentication and REST API - Update Source (Partial) in the SailPoint Developer Community.
where, value equals to 15 represents the wait time in seconds.
DeltaLink Older Than 30 Days Is Not Supported
Resolution: This error occurs because delta token has expired. Run a full aggregation to reset it to the latest delta token.
400 Bad Request on Microsoft Graph API Filter
Resolution: Replace dirSyncEnabled with onPremisesSyncEnabled to check if a user is synced from on-premises directory.
For example, onPremisesSyncEnabled eq true
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.