Configuring AWS
Configuring AWS Manually
If you cannot access CloudFormation, you can manually add AWS accounts within your organization.
SailPoint gathers information from your AWS Organization in two steps:
- First, it uses a role in the management account to get a list of all your AWS Accounts.
- Then, it uses a role with the same name and external ID in each member account to collect the resources.
Collecting AWS Resources Manually
You must create an identity and access management role on your Amazon Web Services source account. This is where you will attach the policy defining what data SailPoint AWS SaaS can read. If you’re using manual IAM roles with an AWS organization, you must repeat this process to create a role in each subaccount.
-
Sign in to the Amazon Web Services Management console, and search for IAM.
-
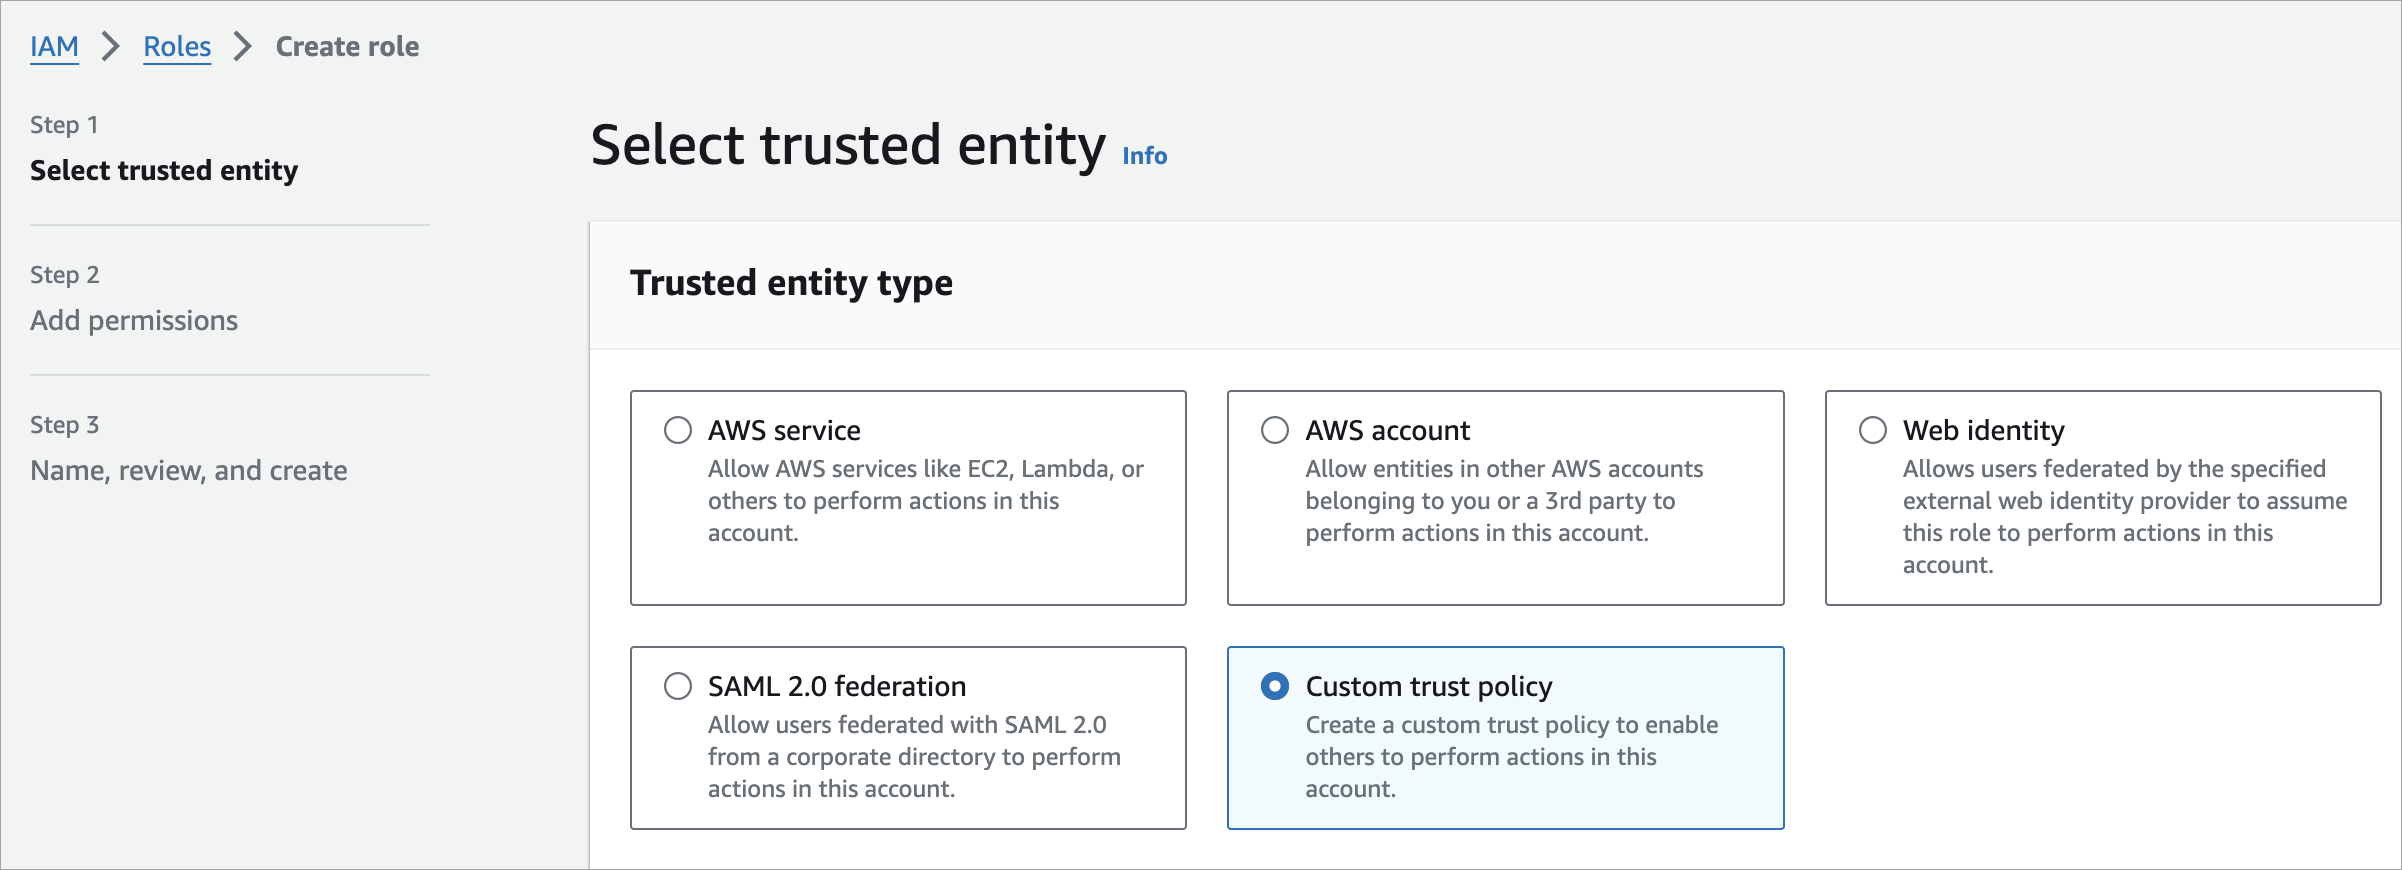
Select Roles, then select Create role.
-
Select the Custom trust policy option.
Screenshot
-
Paste the following code in the Custom trust policy window, replacing
<externalId>with the External ID provided by SailPoint in Connection Settings: -
Confirm the trust policy contains the correct role ARN:
- Commercial accounts:
arn:aws:iam::874540850173:role/ciem_universal - GovCloud accounts:
arn:aws-us-gov:iam::229634586956:role/ciem_universal
- Commercial accounts:
-
Select Require external ID and enter the same External ID provided by SailPoint.
-
Select Next to be taken to Add Permissions.
-
Select Create policy and then select the JSON tab.
-
Replace the JSON text with the required permissions for:
-
Select Next: Tags. Tags are optional.
-
Select Next: Review. Enter an appropriate name and description for the role.
-
Select Create policy. The new policy will be displayed in the list of IAM policies.
-
Select the new policy checkbox and select Next.
-
Enter a role name and details. Review the information and select Create Role. You will be redirected to the roles page.
-
Search for and select the new role to find its role name. You will need this role name to connect your AWS source accounts with the SailPoint AWS SaaS Source.
-
If you are creating manual IAM roles to work in an AWS organization, repeat the IAM role creation process for each subaccount.
Caution
- If you do not include a new role in every subaccount you may have gaps in your data.
- All roles must use the same external ID provided by SailPoint in the connection settings of the AWS SaaS source.
Important
You must verify your configuration before connecting your source. Refer to Verifying Your AWS Configuration for the verification steps.
Configuring AWS Automatically
SailPoint provides CloudFormation templates to automate the creation of IAM roles and policies, a CloudTrail trail, and an S3 Bucket. Depending on your configuration preference and existing infrastructure, different templates are available.
Collecting Data from All AWS Accounts
SailPoint gathers information from your AWS Organization in two steps:
-
First, it uses a role in the management account to get a list of all your AWS Accounts.
-
Then, it uses a role with the same name and external ID in each member account to collect the resources.
Note
To ensure CIEM data processing works correctly, the role names used for both StackSets and Stacks must be consistent.
Automated Setup with CloudFormation
SailPoint offers CloudFormation templates to simplify the setup. These templates create the necessary roles with the minimum required permissions:
- A primary role is created in the management account to list all other accounts.
- Identical roles are created in each member account for SailPoint to assume.
To successfully configure everything using CloudFormation, you must follow all the steps for both StackSets (for multiple accounts) and Stacks (for single accounts). For more information, refer to CloudFormation Deployment Methods.
CloudFormation Deployment Methods
Collecting Resources from All AWS Accounts Using StackSet
The following process creates a role and policies with minimum privileges in the management account.
Create an in-line policy on the role for reading resource data from your AWS cloud.
To enable inventory collection in all accounts:
-
Follow the AWS directions to create a StackSet with service-managed permissions.
-
Upload the appropriate cloud formation template:
AWS accounts only
{
  "AWSTemplateFormatVersion": "2010-09-09",
  "Parameters": {
    "RoleName": {
      "Default": "SailPointAWSRole",
      "Description": "Role with this name will be created.",
      "Type": "String"
    },
    "ExternalId": {
      "Description": "Unique external ID needed for assuming role.",
      "Type": "String"
    },
    "RolePolicyName": {
      "Default": "SailPointAWSPolicy",
      "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.",
      "Type": "String"
    },
    "BucketName": {
      "Description": "Name of existing Bucket with CloudTrail logs.",
      "Type": "String"
    }
  },
  "Resources": {
    "SailPointAWSPolicy": {
      "Type": "AWS::IAM::ManagedPolicy",
      "DeletionPolicy": "Retain",
      "Properties": {
        "Description": "Policy for created for AWS Organizations",
        "Path": "/",
        "Roles": [
          {
            "Ref": "SailPointAWSRole"
          }
        ],
        "PolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Action": [
                "s3:GetBucketLocation",
                "s3:ListBucket"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  ":",
                  [
                    "arn:aws:s3::",
                    {
                      "Ref": "BucketName"
                    }
                  ]
                ]
              }
            },
            {
              "Action": [
                "s3:GetObject"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  "/",
                  [
                    {
                      "Fn::Join": [
                        ":",
                        [
                          "arn:aws:s3::",
                          {
                            "Ref": "BucketName"
                          }
                        ]
                      ]
                    },
                    ""
                  ]
                ]
              }
            }
          ]
        }
      }
    },
    "SailPointAWSRole": {
      "Type": "AWS::IAM::Role",
      "DeletionPolicy": "Retain",
      "Properties": {
        "RoleName": {
          "Ref": "RoleName"
        },
        "AssumeRolePolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Effect": "Allow",
              "Principal": {
                "AWS": "arn:aws:iam::874540850173:role/ciem_universal"
              },
              "Action": "sts:AssumeRole",
              "Condition": {
                "StringEquals": {
                  "sts:ExternalId": {
                    "Ref": "ExternalId"
                  }
                }
              }
            }
          ]
        },
        "Policies": [
          {
            "PolicyName": "SailPointAWSPolicy",
            "PolicyDocument": {
              "Version": "2012-10-17",
              "Statement": [
                {
                  "Effect": "Allow",
                  "Resource": "",
                  "Action": [
                    "iam:GetPolicyVersion",
                    "iam:ListServiceSpecificCredentials",
                    "iam:ListMFADevices",
                    "iam:ListSigningCertificates",
                    "iam:GetGroup",
                    "iam:ListSSHPublicKeys",
                    "iam:ListAttachedRolePolicies",
                    "iam:ListAttachedUserPolicies",
                    "iam:ListAttachedGroupPolicies",
                    "iam:ListRolePolicies",
                    "iam:ListAccessKeys",
                    "iam:ListPolicies",
                    "iam:GetRole",
                    "iam:GetPolicy",
                    "iam:ListGroupPolicies",
                    "iam:ListRoles",
                    "iam:ListUserPolicies",
                    "iam:GetUserPolicy",
                    "iam:ListGroupsForUser",
                    "iam:ListAccountAliases",
                    "iam:ListUsers",
                    "iam:ListGroups",
                    "iam:GetGroupPolicy",
                    "iam:GetUser",
                    "iam:GetRolePolicy",
                    "iam:GetLoginProfile",
                    "iam:ListEntitiesForPolicy",
                    "iam:GetAccessKeyLastUsed",
                    "iam:ListUserTags",
                    "iam:ListRoleTags",
                    "iam:ListPolicyTags",
                    "iam:UpdateLoginProfile",
                    "iam:UpdateAccessKey",
                    "iam:CreateUser",
                    "iam:CreateAccessKey",
                    "iam:CreateLoginProfile",
                    "iam:RemoveUserFromGroup",
                    "iam:AddUserToGroup",
                    "iam:DeleteLoginProfile",
                    "iam:AttachUserPolicy",

"organizations:ListPoliciesForTarget",
      "organizations:ListAccountsForParent",
      "organizations:ListRoots",
      "organizations:ListAccounts",
      "organizations:ListTargetsForPolicy",
      "organizations:DescribeOrganization",
      "organizations:DescribeOrganizationalUnit",
      "organizations:DescribeAccount",
      "organizations:ListParents",
      "organizations:ListOrganizationalUnitsForParent",
      "organizations:DescribePolicy",
    "organizations:ListPolicies",
     "organizations:ListTagsForResource",
     "iam:DeleteGroup",
     "iam:DeleteGroupPolicy"
                  ]
                }
              ]
            }
          }
        ],
        "Path": "/"
      }
    }
  },
  "Outputs": {
    "SailPointAWSRoleARN": {
      "Description": "SailPoint AWS Role ARN",
      "Value": {
        "Fn::GetAtt": [
          "SailPointAWSRole",
          "Arn"
        ]
      }
    },
    "SailPointAWSRoleExternalId": {
      "Description": "SailPoint AWS Role External ID",
      "Value": {
        "Ref": "ExternalId"
      }
    }
  }
}
AWS accounts with Activity Insights
{
  "AWSTemplateFormatVersion": "2010-09-09",
  "Parameters": {
    "RoleName": {
      "Default": "SailPointAWSRole",
      "Description": "Role with this name will be created.",
      "Type": "String"
    },
    "ExternalId": {
      "Description": "Unique external ID needed for assuming role.",
      "Type": "String"
    },
    "RolePolicyName": {
      "Default": "SailPointAWSPolicy",
      "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.",
      "Type": "String"
    },
    "BucketName": {
      "Description": "Name of existing Bucket with CloudTrail logs.",
      "Type": "String"
    }
  },
  "Resources": {
    "SailPointAWSPolicy": {
      "Type": "AWS::IAM::ManagedPolicy",
      "DeletionPolicy": "Retain",
      "Properties": {
        "Description": "Policy for created for AWS Organizations",
        "Path": "/",
        "Roles": [
          {
            "Ref": "SailPointAWSRole"
          }
        ],
        "PolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Action": [
                "s3:GetBucketLocation",
                "s3:ListBucket"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  ":",
                  [
                    "arn:aws:s3::",
                    {
                      "Ref": "BucketName"
                    }
                  ]
                ]
              }
            },
            {
              "Action": [
                "s3:GetObject"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  "/",
                  [
                    {
                      "Fn::Join": [
                        ":",
                        [
                          "arn:aws:s3::",
                          {
                            "Ref": "BucketName"
                          }
                        ]
                      ]
                    },
                    ""
                  ]
                ]
              }
            }
          ]
        }
      }
    },
    "SailPointAWSRole": {
      "Type": "AWS::IAM::Role",
      "DeletionPolicy": "Retain",
      "Properties": {
        "RoleName": {
          "Ref": "RoleName"
        },
        "AssumeRolePolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Effect": "Allow",
              "Principal": {
                "AWS": "arn:aws:iam::874540850173:role/ciem_universal"
              },
              "Action": "sts:AssumeRole",
              "Condition": {
                "StringEquals": {
                  "sts:ExternalId": {
                    "Ref": "ExternalId"
                  }
                }
              }
            }
          ]
        },
        "Policies": [
          {
            "PolicyName": "SailPointAWSPolicy",
            "PolicyDocument": {
              "Version": "2012-10-17",
              "Statement": [
                {
                  "Effect": "Allow",
                  "Resource": "",
                  "Action": [
                    "iam:GetPolicyVersion",
                    "iam:ListServiceSpecificCredentials",
                    "iam:ListMFADevices",
                    "iam:ListSigningCertificates",
                    "iam:GetGroup",
                    "iam:ListSSHPublicKeys",
                    "iam:ListAttachedRolePolicies",
                    "iam:ListAttachedUserPolicies",
                    "iam:ListAttachedGroupPolicies",
                    "iam:ListRolePolicies",
                    "iam:ListAccessKeys",
                    "iam:ListPolicies",
                    "iam:GetRole",
                    "iam:GetPolicy",
                    "iam:ListGroupPolicies",
                    "iam:ListRoles",
                    "iam:ListUserPolicies",
                    "iam:GetUserPolicy",
                    "iam:ListGroupsForUser",
                    "iam:ListAccountAliases",
                    "iam:ListUsers",
                    "iam:ListGroups",
                    "iam:GetGroupPolicy",
                    "iam:GetUser",
                    "iam:GetRolePolicy",
                    "iam:GetLoginProfile",
                    "iam:ListEntitiesForPolicy",
                    "iam:GetAccessKeyLastUsed",
                    "iam:ListUserTags",
                    "iam:ListRoleTags",
                    "iam:ListPolicyTags",
                    "iam:UpdateLoginProfile",
                    "iam:UpdateAccessKey",
                    "iam:CreateUser",
                    "iam:CreateAccessKey",
                    "iam:CreateLoginProfile",
                    "iam:RemoveUserFromGroup",
                    "iam:AddUserToGroup",
                    "iam:DeleteLoginProfile",
                    "iam:AttachUserPolicy",
                    "cloudtrail:Get*",
                    "cloudtrail:Describe*",
                    "cloudtrail:List*",
                    "cloudtrail:LookupEvents",

"organizations:ListPoliciesForTarget",
      "organizations:ListAccountsForParent",
      "organizations:ListRoots",
      "organizations:ListAccounts",
      "organizations:ListTargetsForPolicy",
      "organizations:DescribeOrganization",
      "organizations:DescribeOrganizationalUnit",
      "organizations:DescribeAccount",
      "organizations:ListParents",
      "organizations:ListOrganizationalUnitsForParent",
      "organizations:DescribePolicy",
    "organizations:ListPolicies",
     "organizations:ListTagsForResource",
     "iam:DeleteGroup",
     "iam:DeleteGroupPolicy"
                  ]
                }
              ]
            }
          }
        ],
        "Path": "/"
      }
    }
  },
  "Outputs": {
    "SailPointAWSRoleARN": {
      "Description": "SailPoint AWS Role ARN",
      "Value": {
        "Fn::GetAtt": [
          "SailPointAWSRole",
          "Arn"
        ]
      }
    },
    "SailPointAWSRoleExternalId": {
      "Description": "SailPoint AWS Role External ID",
      "Value": {
        "Ref": "ExternalId"
      }
    }
  }
}
AWS accounts with Agent Discovery
{
  "AWSTemplateFormatVersion": "2010-09-09",
  "Parameters": {
    "RoleName": {
      "Default": "SailPointAWSRole",
      "Description": "Role with this name will be created.",
      "Type": "String"
    },
    "ExternalId": {
      "Description": "Unique external ID needed for assuming role.",
      "Type": "String"
    },
    "RolePolicyName": {
      "Default": "SailPointAWSPolicy",
      "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.",
      "Type": "String"
    },
    "BucketName": {
      "Description": "Name of existing Bucket with CloudTrail logs.",
      "Type": "String"
    }
  },
  "Resources": {
    "SailPointAWSPolicy": {
      "Type": "AWS::IAM::ManagedPolicy",
      "DeletionPolicy": "Retain",
      "Properties": {
        "Description": "Policy for created for AWS Organizations",
        "Path": "/",
        "Roles": [
          {
            "Ref": "SailPointAWSRole"
          }
        ],
        "PolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Action": [
                "s3:GetBucketLocation",
                "s3:ListBucket"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  ":",
                  [
                    "arn:aws:s3::",
                    {
                      "Ref": "BucketName"
                    }
                  ]
                ]
              }
            },
            {
              "Action": [
                "s3:GetObject"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  "/",
                  [
                    {
                      "Fn::Join": [
                        ":",
                        [
                          "arn:aws:s3::",
                          {
                            "Ref": "BucketName"
                          }
                        ]
                      ]
                    },
                    ""
                  ]
                ]
              }
            }
          ]
        }
      }
    },
    "SailPointAWSRole": {
      "Type": "AWS::IAM::Role",
      "DeletionPolicy": "Retain",
      "Properties": {
        "RoleName": {
          "Ref": "RoleName"
        },
        "AssumeRolePolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Effect": "Allow",
              "Principal": {
                "AWS": "arn:aws:iam::874540850173:role/ciem_universal"
              },
              "Action": "sts:AssumeRole",
              "Condition": {
                "StringEquals": {
                  "sts:ExternalId": {
                    "Ref": "ExternalId"
                  }
                }
              }
            }
          ]
        },
        "Policies": [
          {
            "PolicyName": "SailPointAWSPolicy",
            "PolicyDocument": {
              "Version": "2012-10-17",
              "Statement": [
                {
                  "Effect": "Allow",
                  "Resource": "",
                  "Action": [
                    "iam:GetPolicyVersion",
                    "iam:ListServiceSpecificCredentials",
                    "iam:ListMFADevices",
                    "iam:ListSigningCertificates",
                    "iam:GetGroup",
                    "iam:ListSSHPublicKeys",
                    "iam:ListAttachedRolePolicies",
                    "iam:ListAttachedUserPolicies",
                    "iam:ListAttachedGroupPolicies",
                    "iam:ListRolePolicies",
                    "iam:ListAccessKeys",
                    "iam:ListPolicies",
                    "iam:GetRole",
                    "iam:GetPolicy",
                    "iam:ListGroupPolicies",
                    "iam:ListRoles",
                    "iam:ListUserPolicies",
                    "iam:GetUserPolicy",
                    "iam:ListGroupsForUser",
                    "iam:ListAccountAliases",
                    "iam:ListUsers",
                    "iam:ListGroups",
                    "iam:GetGroupPolicy",
                    "iam:GetUser",
                    "iam:GetRolePolicy",
                    "iam:GetLoginProfile",
                    "iam:ListEntitiesForPolicy",
                    "iam:GetAccessKeyLastUsed",
                    "iam:ListUserTags",
                    "iam:ListRoleTags",
                    "iam:ListPolicyTags",
                    "iam:UpdateLoginProfile",
                    "iam:UpdateAccessKey",
                    "iam:CreateUser",
                    "iam:CreateAccessKey",
                    "iam:CreateLoginProfile",
                    "iam:RemoveUserFromGroup",
                    "iam:AddUserToGroup",
                    "iam:DeleteLoginProfile",
                    "iam:AttachUserPolicy",
                    "bedrock:ListAgents",
                    "bedrock:GetAgent",
                    "bedrock:ListAgentActionGroups",
                    "bedrock:GetAgentActionGroup",
                    "bedrock:ListAgentKnowledgeBases",
                    "bedrock:GetAgentKnowledgeBase",
                    "bedrock:ListKnowledgeBases",
                    "bedrock:GetKnowledgeBase",
                    "bedrock:ListAgentAliases",
                    "bedrock:GetAgentAlias",
                    "bedrock:ListAgentVersions",
                    "bedrock:GetAgentVersion",
                    "bedrock:ListDataSources",
                    "bedrock:GetDataSource",
                    "bedrock:ListAgentCollaborators",
                    "bedrock:GetAgentCollaborator",
                    "kms:Decrypt",
                    "kms:GenerateDataKey",
                    "bedrock-agentcore:ListAgentRuntimes",
                    "bedrock-agentcore:GetAgentRuntime",
                    "bedrock-agentcore:ListAgentRuntimeEndpoints",
                    "bedrock-agentcore:GetAgentRuntimeEndpoint",
                    "bedrock-agentcore:ListAgentRuntimeVersions",
                    "bedrock-agentcore:ListWorkloadIdentities",
                    "bedrock-agentcore:GetWorkloadIdentity",
                    "bedrock-agentcore:ListOauth2CredentialProviders",
                    "bedrock-agentcore:GetApiKeyCredentialProvider",
                    "bedrock-agentcore:ListApiKeyCredentialProviders",
                    "bedrock-agentcore:GetOauth2CredentialProvider",

"organizations:ListPoliciesForTarget",
      "organizations:ListAccountsForParent",
      "organizations:ListRoots",
      "organizations:ListAccounts",
      "organizations:ListTargetsForPolicy",
      "organizations:DescribeOrganization",
      "organizations:DescribeOrganizationalUnit",
      "organizations:DescribeAccount",
      "organizations:ListParents",
      "organizations:ListOrganizationalUnitsForParent",
      "organizations:DescribePolicy",
    "organizations:ListPolicies",
     "organizations:ListTagsForResource",
     "iam:DeleteGroup",
     "iam:DeleteGroupPolicy"
                  ]
                }
              ]
            }
          }
        ],
        "Path": "/"
      }
    }
  },
  "Outputs": {
    "SailPointAWSRoleARN": {
      "Description": "SailPoint AWS Role ARN",
      "Value": {
        "Fn::GetAtt": [
          "SailPointAWSRole",
          "Arn"
        ]
      }
    },
    "SailPointAWSRoleExternalId": {
      "Description": "SailPoint AWS Role External ID",
      "Value": {
        "Ref": "ExternalId"
      }
    }
  }
}
AWS accounts with CIEM and Activity Insights
{
  "AWSTemplateFormatVersion": "2010-09-09",
  "Parameters": {
    "RoleName": {
      "Default": "SailPointAWSRole",
      "Description": "Role with this name will be created.",
      "Type": "String"
    },
    "ExternalId": {
      "Description": "Unique external ID needed for assuming role.",
      "Type": "String"
    },
    "RolePolicyName": {
      "Default": "SailPointAWSPolicy",
      "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.",
      "Type": "String"
    },
    "BucketName": {
      "Description": "Name of existing Bucket with CloudTrail logs.",
      "Type": "String"
    }
  },
  "Resources": {
    "SailPointAWSPolicy": {
      "Type": "AWS::IAM::ManagedPolicy",
      "DeletionPolicy": "Retain",
      "Properties": {
        "Description": "Policy for created for AWS Organizations",
        "Path": "/",
        "Roles": [
          {
            "Ref": "SailPointAWSRole"
          }
        ],
        "PolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Action": [
                "s3:GetBucketLocation",
                "s3:ListBucket"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  ":",
                  [
                    "arn:aws:s3::",
                    {
                      "Ref": "BucketName"
                    }
                  ]
                ]
              }
            },
            {
              "Action": [
                "s3:GetObject"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  "/",
                  [
                    {
                      "Fn::Join": [
                        ":",
                        [
                          "arn:aws:s3::",
                          {
                            "Ref": "BucketName"
                          }
                        ]
                      ]
                    },
                    "*"
                  ]
                ]
              }
            }
          ]
        }
      }
    },
    "SailPointAWSRole": {
      "Type": "AWS::IAM::Role",
      "DeletionPolicy": "Retain",
      "Properties": {
        "RoleName": {
          "Ref": "RoleName"
        },
        "AssumeRolePolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Effect": "Allow",
              "Principal": {
                "AWS": "arn:aws:iam::874540850173:role/ciem_universal"
              },
              "Action": "sts:AssumeRole",
              "Condition": {
                "StringEquals": {
                  "sts:ExternalId": {
                    "Ref": "ExternalId"
                  }
                }
              }
            }
          ]
        },
        "Policies": [
          {
            "PolicyName": "SailPointAWSPolicy",
            "PolicyDocument": {
              "Version": "2012-10-17",
              "Statement": [
                {
                  "Effect": "Allow",
                  "Resource": "*",
                  "Action": [
                    "organizations:Describe*",
                    "organizations:List*",
                    "iam:Get*",
                    "iam:List*",
                    "iam:UpdateLoginProfile",
                    "iam:CreateGroup",
                    "iam:DeleteAccessKey",
                    "iam:AttachUserPolicy",
                    "iam:DeleteUserPolicy",
                    "iam:UpdateAccessKey",
                    "iam:AttachRolePolicy",
                    "iam:DeleteUser",
                    "iam:CreateUser",
                    "iam:CreateAccessKey",
                    "iam:CreatePolicy",
                    "iam:CreateLoginProfile",
                    "iam:RemoveUserFromGroup",
                    "iam:AddUserToGroup",
                    "iam:DetachRolePolicy",
                    "iam:DeleteSigningCertificate",
                    "iam:AttachGroupPolicy",
                    "iam:DeleteRolePolicy",
                    "iam:DetachGroupPolicy",
                    "iam:DetachUserPolicy",
                    "iam:DeleteLoginProfile",
                    "cloudtrail:DescribeTrails",
                    "cloudtrail:GetEventSelectors",
                    "cloudtrail:GetTrailStatus",
                    "cloudtrail:ListTags",
                    "cloudtrail:LookupEvents",
                    "cloudtrail:Get*",
                    "cloudtrail:Describe*",
                    "cloudtrail:List*",
                    "cloudwatch:Describe*",
                    "cloudwatch:ListTagsForResource",
                    "dynamodb:DescribeGlobalTable",
                    "dynamodb:DescribeTable",
                    "dynamodb:DescribeTimeToLive",
                    "dynamodb:ListGlobalTables",
                    "dynamodb:ListStreams",
                    "dynamodb:ListTables",
                    "dynamodb:ListTagsOfResource",
                    "ec2:Describe*",
                    "ec2:DescribeTransitGatewayAttachments",
                    "ec2:DescribeTransitGatewayMulticastDomains",
                    "ec2:DescribeTransitGatewayPeeringAttachments",
                    "ec2:DescribeTransitGatewayRouteTables",
                    "ec2:DescribeTransitGatewayVpcAttachments",
                    "ec2:DescribeTransitGateways",
                    "ec2:GetManagedPrefixListAssociations",
                    "ec2:GetManagedPrefixListEntries",
                    "ec2:GetTransitGatewayAttachmentPropagations",
                    "ec2:GetTransitGatewayMulticastDomainAssociations",
                    "ec2:GetTransitGatewayPrefixListReferences",
                    "ec2:GetTransitGatewayRouteTableAssociations",
                    "ec2:GetTransitGatewayRouteTablePropagations",
                    "elasticloadbalancing:Describe*",
                    "kms:Describe*",
                    "kms:Get*",
                    "kms:List*",
                    "lambda:GetFunctionConfiguration",
                    "lambda:GetFunctionEventInvokeConfig",
                    "lambda:GetLayerVersionPolicy",
                    "lambda:GetPolicy",
                    "lambda:List*",
                    "rds:Describe*",
                    "rds:ListTagsForResource",
                    "s3:GetAccessPoint",
                    "s3:GetAccessPointPolicy",
                    "s3:GetAccessPointPolicyStatus",
                    "s3:GetAccountPublicAccessBlock",
                    "s3:GetAnalyticsConfiguration",
                    "s3:GetBucket*",
                    "s3:GetEncryptionConfiguration",
                    "s3:GetInventoryConfiguration",
                    "s3:GetObjectAcl",
                    "s3:GetObjectVersionAcl",
                    "s3:GetReplicationConfiguration",
                    "s3:ListAccessPoints",
                    "s3:ListAllMyBuckets",
                    "sns:GetTopicAttributes",
                    "sns:ListSubscriptions",
                    "sns:ListSubscriptionsByTopic",
                    "sns:ListTagsForResource",
                    "sns:ListTopics",
                    "sqs:GetQueueAttributes",
                    "sqs:ListDeadLetterSourceQueues",
                    "sqs:ListQueueTags",
                    "sqs:ListQueues",
                    "tag:GetResources",
                    "tag:GetTagKeys",
                    "iam:GenerateCredentialReport",
                    "iam:GenerateServiceLastAccessedDetails",
                    "iam:SimulateCustomPolicy",
                    "iam:SimulatePrincipalPolicy",
                    "bedrock-agentcore:GetAgentRuntime",
                    "bedrock-agentcore:GetGateway",
                    "bedrock-agentcore:GetGatewayTarget",
                    "bedrock-agentcore:ListAgentRuntimeEndpoints",
                    "bedrock-agentcore:ListAgentRuntimes",
                    "bedrock-agentcore:ListAgentRuntimeVersions",
                    "bedrock-agentcore:ListGateways",
                    "bedrock-agentcore:ListGatewayTargets",
                    "bedrock:GetAgent",
                    "bedrock:GetAgentAlias",
                    "bedrock:GetKnowledgeBase",
                    "bedrock:ListAgentActionGroups",
                    "bedrock:ListAgentAliases",
                    "bedrock:ListAgentKnowledgeBases",
                    "bedrock:ListAgents",
                    "bedrock:ListAgentVersions",
                    "iam:DeleteGroup",
                    "iam:DeleteGroupPolicy"
                  ]
                }
              ]
            }
          }
        ],
        "Path": "/"
      }
    }
  },
  "Outputs": {
    "SailPointAWSRoleARN": {
      "Description": "SailPoint AWS Role ARN",
      "Value": {
        "Fn::GetAtt": [
          "SailPointAWSRole",
          "Arn"
        ]
      }
    },
    "SailPointAWSRoleExternalId": {
      "Description": "SailPoint AWS Role External ID",
      "Value": {
        "Ref": "ExternalId"
      }
    }
  }
}
{ "AWSTemplateFormatVersion" : "2010-09-09", "Parameters": { "RoleName": { "Default": "SailPointAWSRole", "Description": "Role with this name will be created.", "Type": "String" }, "ExternalId": { "Description": "Unique external ID needed for assuming role.", "Type": "String" }, "RolePolicyName": { "Default": "SailPointAWSPolicy", "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.", "Type": "String" }, "BucketName": { "Description": "Name of existing Bucket with CloudTrail logs.", "Type": "String" } }, "Resources" : { "SailPointAWSPolicy": { "Type": "AWS::IAM::ManagedPolicy", "DeletionPolicy": "Retain", "Properties": { "Description": "Policy for created for AWS Organizations", "Path": "/", "Roles": [ { "Ref": "SailPointAWSRole" } ], "PolicyDocument": { "Version": "2012-10-17", "Statement": [ { "Action": [ "s3:GetBucketLocation", "s3:ListBucket" ], "Effect": "Allow", "Resource": { "Fn::Join": [ ":", [ "arn:aws:s3::", { "Ref": "BucketName" } ] ] } }, { "Action": [ "s3:GetObject" ], "Effect": "Allow", "Resource": { "Fn::Join": [ "/", [ { "Fn::Join": [ ":", [ "arn:aws:s3::", { "Ref": "BucketName" } ] ] }, "*" ] ] } } ] } } }, "SailPointAWSRole": { "Type": "AWS::IAM::Role", "DeletionPolicy": "Retain", "Properties": { "RoleName": { "Ref": "RoleName" }, "AssumeRolePolicyDocument": { "Version": "2012-10-17", "Statement": [ { "Effect": "Allow", "Principal": { "AWS": [ "arn:aws-us-gov:iam::229634586956:role/ciem_universal" ] }, "Action": "sts:AssumeRole", "Condition": { "StringEquals": { "sts:ExternalId": { "Ref": "ExternalId" } } } } ] }, "Policies": [ { "PolicyName" : "SailPointAWSPolicy", "PolicyDocument" : { "Version":"2012-10-17", "Statement":[ { "Effect":"Allow", "Resource":"*", "Action":[ "organizations:Describe*", "organizations:List*", "iam:Get*", "iam:List*", "iam:UpdateLoginProfile", "iam:CreateGroup", "iam:DeleteAccessKey", "iam:AttachUserPolicy", "iam:DeleteUserPolicy", "iam:UpdateAccessKey", "iam:AttachRolePolicy", "iam:DeleteUser", "iam:CreateUser", "iam:CreateAccessKey", "iam:CreatePolicy", "iam:CreateLoginProfile", "iam:RemoveUserFromGroup", "iam:AddUserToGroup", "iam:DetachRolePolicy", "iam:DeleteSigningCertificate", "iam:AttachGroupPolicy", "iam:DeleteRolePolicy", "iam:DetachGroupPolicy", "iam:DetachUserPolicy", "iam:DeleteLoginProfile", "cloudtrail:DescribeTrails", "cloudtrail:GetEventSelectors", "cloudtrail:GetTrailStatus", "cloudtrail:ListTags", "cloudtrail:LookupEvents", "cloudtrail:Get*", "cloudtrail:Describe*", "cloudtrail:List*", "cloudwatch:Describe*", "cloudwatch:ListTagsForResource", "dynamodb:DescribeGlobalTable", "dynamodb:DescribeTable", "dynamodb:DescribeTimeToLive", "dynamodb:ListGlobalTables", "dynamodb:ListStreams", "dynamodb:ListTables", "dynamodb:ListTagsOfResource", "ec2:Describe*", "ec2:DescribeTransitGatewayAttachments", "ec2:DescribeTransitGatewayMulticastDomains", "ec2:DescribeTransitGatewayPeeringAttachments", "ec2:DescribeTransitGatewayRouteTables", "ec2:DescribeTransitGatewayVpcAttachments", "ec2:DescribeTransitGateways", "ec2:GetManagedPrefixListAssociations", "ec2:GetManagedPrefixListEntries", "ec2:GetTransitGatewayAttachmentPropagations", "ec2:GetTransitGatewayMulticastDomainAssociations", "ec2:GetTransitGatewayPrefixListReferences", "ec2:GetTransitGatewayRouteTableAssociations", "ec2:GetTransitGatewayRouteTablePropagations", "elasticloadbalancing:Describe*", "kms:Describe*", "kms:Get*", "kms:List*", "lambda:GetFunctionConfiguration", "lambda:GetFunctionEventInvokeConfig", "lambda:GetLayerVersionPolicy", "lambda:GetPolicy", "lambda:List*", "rds:Describe*", "rds:ListTagsForResource", "s3:GetAccessPoint", "s3:GetAccessPointPolicy", "s3:GetAccessPointPolicyStatus", "s3:GetAccountPublicAccessBlock", "s3:GetAnalyticsConfiguration", "s3:GetBucket*", "s3:GetEncryptionConfiguration", "s3:GetInventoryConfiguration", "s3:GetObjectAcl", "s3:GetObjectVersionAcl", "s3:GetReplicationConfiguration", "s3:ListAccessPoints", "s3:ListAllMyBuckets", "sns:GetTopicAttributes", "sns:ListSubscriptions", "sns:ListSubscriptionsByTopic", "sns:ListTagsForResource", "sns:ListTopics", "sqs:GetQueueAttributes", "sqs:ListDeadLetterSourceQueues", "sqs:ListQueueTags", "sqs:ListQueues", "tag:GetResources", "tag:GetTagKeys", "iam:GenerateCredentialReport", "iam:GenerateServiceLastAccessedDetails", "iam:SimulateCustomPolicy", "iam:SimulatePrincipalPolicy", "bedrock-agentcore:GetAgentRuntime", "bedrock-agentcore:GetGateway", "bedrock-agentcore:GetGatewayTarget", "bedrock-agentcore:ListAgentRuntimeEndpoints", "bedrock-agentcore:ListAgentRuntimes", "bedrock-agentcore:ListAgentRuntimeVersions", "bedrock-agentcore:ListGateways", "bedrock-agentcore:ListGatewayTargets", "bedrock:GetAgent", "bedrock:GetAgentAlias", "bedrock:GetKnowledgeBase", "bedrock:ListAgentActionGroups", "bedrock:ListAgentAliases", "bedrock:ListAgentKnowledgeBases", "bedrock:ListAgents", "bedrock:ListAgentVersions", "iam:DeleteGroup", "iam:DeleteGroupPolicy" ] } ] } } ], "Path": "/" } } }, "Outputs": { "SailPointAWSRoleARN": { "Description": "SailPoint AWS Role ARN", "Value": { "Fn::GetAtt": [ "SailPointAWSRole", "Arn" ] } }, "SailPointAWSRoleExternalId": { "Description": "SailPoint AWS Role External ID", "Value": { "Ref": "ExternalId" } } }AWS accounts with CIEM, Activity Insights, and Agent Discovery
{
  "AWSTemplateFormatVersion": "2010-09-09",
  "Parameters": {
    "RoleName": {
      "Default": "SailPointAWSRole",
      "Description": "Role with this name will be created.",
      "Type": "String"
    },
    "ExternalId": {
      "Description": "Unique external ID needed for assuming role.",
      "Type": "String"
    },
    "RolePolicyName": {
      "Default": "SailPointAWSPolicy",
      "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.",
      "Type": "String"
    },
    "BucketName": {
      "Description": "Name of existing Bucket with CloudTrail logs.",
      "Type": "String"
    }
  },
  "Resources": {
    "SailPointAWSPolicy": {
      "Type": "AWS::IAM::ManagedPolicy",
      "DeletionPolicy": "Retain",
      "Properties": {
        "Description": "Policy for created for AWS Organizations",
        "Path": "/",
        "Roles": [
          {
            "Ref": "SailPointAWSRole"
          }
        ],
        "PolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Action": [
                "s3:GetBucketLocation",
                "s3:ListBucket"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  ":",
                  [
                    "arn:aws:s3::",
                    {
                      "Ref": "BucketName"
                    }
                  ]
                ]
              }
            },
            {
              "Action": [
                "s3:GetObject"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  "/",
                  [
                    {
                      "Fn::Join": [
                        ":",
                        [
                          "arn:aws:s3::",
                          {
                            "Ref": "BucketName"
                          }
                        ]
                      ]
                    },
                    "*"
                  ]
                ]
              }
            }
          ]
        }
      }
    },
    "SailPointAWSRole": {
      "Type": "AWS::IAM::Role",
      "DeletionPolicy": "Retain",
      "Properties": {
        "RoleName": {
          "Ref": "RoleName"
        },
        "AssumeRolePolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Effect": "Allow",
              "Principal": {
                "AWS": "arn:aws:iam::874540850173:role/ciem_universal"
              },
              "Action": "sts:AssumeRole",
              "Condition": {
                "StringEquals": {
                  "sts:ExternalId": {
                    "Ref": "ExternalId"
                  }
                }
              }
            }
          ]
        },
        "Policies": [
          {
            "PolicyName": "SailPointAWSPolicy",
            "PolicyDocument": {
              "Version": "2012-10-17",
              "Statement": [
                {
                  "Effect": "Allow",
                  "Resource": "*",
                  "Action": [
                    "organizations:Describe*",
                    "organizations:List*",
                    "iam:Get*",
                    "iam:List*",
                    "iam:UpdateLoginProfile",
                    "iam:CreateGroup",
                    "iam:DeleteAccessKey",
                    "iam:AttachUserPolicy",
                    "iam:DeleteUserPolicy",
                    "iam:UpdateAccessKey",
                    "iam:AttachRolePolicy",
                    "iam:DeleteUser",
                    "iam:CreateUser",
                    "iam:CreateAccessKey",
                    "iam:CreatePolicy",
                    "iam:CreateLoginProfile",
                    "iam:RemoveUserFromGroup",
                    "iam:AddUserToGroup",
                    "iam:DetachRolePolicy",
                    "iam:DeleteSigningCertificate",
                    "iam:AttachGroupPolicy",
                    "iam:DeleteRolePolicy",
                    "iam:DetachGroupPolicy",
                    "iam:DetachUserPolicy",
                    "iam:DeleteLoginProfile",
                    "cloudtrail:DescribeTrails",
                    "cloudtrail:GetEventSelectors",
                    "cloudtrail:GetTrailStatus",
                    "cloudtrail:ListTags",
                    "cloudtrail:LookupEvents",
                    "cloudtrail:Get*",
                    "cloudtrail:Describe*",
                    "cloudtrail:List*",
                    "cloudwatch:Describe*",
                    "cloudwatch:ListTagsForResource",
                    "dynamodb:DescribeGlobalTable",
                    "dynamodb:DescribeTable",
                    "dynamodb:DescribeTimeToLive",
                    "dynamodb:ListGlobalTables",
                    "dynamodb:ListStreams",
                    "dynamodb:ListTables",
                    "dynamodb:ListTagsOfResource",
                    "ec2:Describe*",
                    "ec2:DescribeTransitGatewayAttachments",
                    "ec2:DescribeTransitGatewayMulticastDomains",
                    "ec2:DescribeTransitGatewayPeeringAttachments",
                    "ec2:DescribeTransitGatewayRouteTables",
                    "ec2:DescribeTransitGatewayVpcAttachments",
                    "ec2:DescribeTransitGateways",
                    "ec2:GetManagedPrefixListAssociations",
                    "ec2:GetManagedPrefixListEntries",
                    "ec2:GetTransitGatewayAttachmentPropagations",
                    "ec2:GetTransitGatewayMulticastDomainAssociations",
                    "ec2:GetTransitGatewayPrefixListReferences",
                    "ec2:GetTransitGatewayRouteTableAssociations",
                    "ec2:GetTransitGatewayRouteTablePropagations",
                    "elasticloadbalancing:Describe*",
                    "kms:Describe*",
                    "kms:Get*",
                    "kms:List*",
                    "lambda:GetFunctionConfiguration",
                    "lambda:GetFunctionEventInvokeConfig",
                    "lambda:GetLayerVersionPolicy",
                    "lambda:GetPolicy",
                    "lambda:List*",
                    "rds:Describe*",
                    "rds:ListTagsForResource",
                    "s3:GetAccessPoint",
                    "s3:GetAccessPointPolicy",
                    "s3:GetAccessPointPolicyStatus",
                    "s3:GetAccountPublicAccessBlock",
                    "s3:GetAnalyticsConfiguration",
                    "s3:GetBucket*",
                    "s3:GetEncryptionConfiguration",
                    "s3:GetInventoryConfiguration",
                    "s3:GetObjectAcl",
                    "s3:GetObjectVersionAcl",
                    "s3:GetReplicationConfiguration",
                    "s3:ListAccessPoints",
                    "s3:ListAllMyBuckets",
                    "sns:GetTopicAttributes",
                    "sns:ListSubscriptions",
                    "sns:ListSubscriptionsByTopic",
                    "sns:ListTagsForResource",
                    "sns:ListTopics",
                    "sqs:GetQueueAttributes",
                    "sqs:ListDeadLetterSourceQueues",
                    "sqs:ListQueueTags",
                    "sqs:ListQueues",
                    "tag:GetResources",
                    "tag:GetTagKeys",
                    "iam:GenerateCredentialReport",
                    "iam:GenerateServiceLastAccessedDetails",
                    "iam:SimulateCustomPolicy",
                    "iam:SimulatePrincipalPolicy",
                    "iam:ListUsers",
                    "iam:ListAccessKeys",
                    "iam:GetAccessKeyLastUsed",
                    "iam:ListServiceSpecificCredentials",
                    "iam:ListSSHPublicKeys",
                    "iam:ListSigningCertificates",
                    "bedrock:ListAgents",
                    "bedrock:GetAgent",
                    "bedrock:ListAgentActionGroups",
                    "bedrock:GetAgentActionGroup",
                    "bedrock:ListAgentKnowledgeBases",
                    "bedrock:GetAgentKnowledgeBase",
                    "bedrock:ListKnowledgeBases",
                    "bedrock:GetKnowledgeBase",
                    "bedrock:ListAgentAliases",
                    "bedrock:GetAgentAlias",
                    "bedrock:ListAgentVersions",
                    "bedrock:GetAgentVersion",
                    "bedrock:ListDataSources",
                    "bedrock:GetDataSource",
                    "bedrock:ListAgentCollaborators",
                    "bedrock:GetAgentCollaborator",
                    "kms:Decrypt",
                    "kms:GenerateDataKey",
                    "bedrock-agentcore:ListAgentRuntimes",
                    "bedrock-agentcore:GetAgentRuntime",
                    "bedrock-agentcore:ListAgentRuntimeEndpoints",
                    "bedrock-agentcore:GetAgentRuntimeEndpoint",
                    "bedrock-agentcore:ListAgentRuntimeVersions",
                    "bedrock-agentcore:ListWorkloadIdentities",
                    "bedrock-agentcore:GetWorkloadIdentity",
                    "bedrock-agentcore:ListOauth2CredentialProviders",
                    "bedrock-agentcore:GetApiKeyCredentialProvider",
                    "bedrock-agentcore:ListApiKeyCredentialProviders",
                    "bedrock-agentcore:GetOauth2CredentialProvider",
                            "connect:ListInstances",
                    "connect:DescribeInstance",
                    "connect:ListIntegrationAssociations",
                    "connect:ListEntitySecurityProfiles",
                    "connect:DescribeSecurityProfile",
                    "wisdom:GetAssistant",
                    "wisdom:ListAIAgents",
                    "wisdom:ListAIAgentVersions",
                    "wisdom:GetAIAgent",
                    "wisdom:GetAssistantAssociation",
                    "wisdom:GetKnowledgeBase",
                    "wisdom:GetAIPrompt",
                    "wisdom:GetAIGuardrail",
                    "quicksight:ListAgents",
                    "quicksight:DescribeAgent",
                    "quicksight:DescribeAgentPermissions",
                    "quicksight:ListActionConnectors",
                    "quicksight:DescribeActionConnector",
                    "quicksight:DescribeActionConnectorPermissions",
                    "agent-registry:ListRegistries",
                    "agent-registry:ListRegistryRecords",
                    "agent-registry:GetRegistryRecord",
                    "agent-registry:ListTagsForResource",
                    "iam:DeleteGroup",
                    "iam:DeleteGroupPolicy"

                  ]
                }
              ]
            }
          }
        ],
        "Path": "/"
      }
    }
  },
  "Outputs": {
    "SailPointAWSRoleARN": {
      "Description": "SailPoint AWS Role ARN",
      "Value": {
        "Fn::GetAtt": [
          "SailPointAWSRole",
          "Arn"
        ]
      }
    },
    "SailPointAWSRoleExternalId": {
      "Description": "SailPoint AWS Role External ID",
      "Value": {
        "Ref": "ExternalId"
      }
    }
  }
}
Important
-
Amazon Bedrock AgentCore agents are not supported in AWS GovCloud. For more information about the support of this regional service, refer to AWS Regions in the AWS documentation.
-
Amazon Connect Customer agent discovery actions aren't included in this AWS GovCloud template. The following list of Amazon Connect instance APIs is still valid for partition.
connect:ListInstancesconnect:ListIntegrationAssociations"connect:DescribeInstance""connect:ListEntitySecurityProfiles""connect:DescribeSecurityProfile"
Confirm regional availability for Amazon Q in Connect and the
wisdom:*APIs before adding the following actions:"wisdom:GetAssistant""wisdom:ListAIAgents""wisdom:ListAIAgentVersions""wisdom:GetAIAgent""wisdom:GetAssistantAssociation""wisdom:GetKnowledgeBase""wisdom:GetAIPrompt""wisdom:GetAIGuardrail"
-
Amazon Quick agent discovery actions aren't included in this AWS GovCloud template. Confirm regional availability for Amazon Quick and the
quicksight:*APIs before adding the actions listed in Machine Identity Governance Policies. -
AWS Agent Registry discovery actions aren't included in this AWS GovCloud template. Confirm regional availability for AWS Agent Registry and the
agent-registry:*APIs before adding the actions listed in Machine Identity Governance Policies.
{ "AWSTemplateFormatVersion" : "2010-09-09", "Parameters": { "RoleName": { "Default": "SailPointAWSRole", "Description": "Role with this name will be created.", "Type": "String" }, "ExternalId": { "Description": "Unique external ID needed for assuming role.", "Type": "String" }, "RolePolicyName": { "Default": "SailPointAWSPolicy", "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.", "Type": "String" }, "BucketName": { "Description": "Name of existing Bucket with CloudTrail logs.", "Type": "String" } }, "Resources" : { "SailPointAWSPolicy": { "Type": "AWS::IAM::ManagedPolicy", "DeletionPolicy": "Retain", "Properties": { "Description": "Policy for created for AWS Organizations", "Path": "/", "Roles": [ { "Ref": "SailPointAWSRole" } ], "PolicyDocument": { "Version": "2012-10-17", "Statement": [ { "Action": [ "s3:GetBucketLocation", "s3:ListBucket" ], "Effect": "Allow", "Resource": { "Fn::Join": [ ":", [ "arn:aws:s3::", { "Ref": "BucketName" } ] ] } }, { "Action": [ "s3:GetObject" ], "Effect": "Allow", "Resource": { "Fn::Join": [ "/", [ { "Fn::Join": [ ":", [ "arn:aws:s3::", { "Ref": "BucketName" } ] ] }, "*" ] ] } } ] } } }, "SailPointAWSRole": { "Type": "AWS::IAM::Role", "DeletionPolicy": "Retain", "Properties": { "RoleName": { "Ref": "RoleName" }, "AssumeRolePolicyDocument": { "Version": "2012-10-17", "Statement": [ { "Effect": "Allow", "Principal": { "AWS": [ "arn:aws-us-gov:iam::229634586956:role/ciem_universal" ] }, "Action": "sts:AssumeRole", "Condition": { "StringEquals": { "sts:ExternalId": { "Ref": "ExternalId" } } } } ] }, "Policies": [ { "PolicyName" : "SailPointAWSPolicy", "PolicyDocument" : { "Version":"2012-10-17", "Statement":[ { "Effect":"Allow", "Resource":"*", "Action":[ "organizations:Describe*", "organizations:List*", "iam:Get*", "iam:List*", "iam:UpdateLoginProfile", "iam:CreateGroup", "iam:DeleteAccessKey", "iam:AttachUserPolicy", "iam:DeleteUserPolicy", "iam:UpdateAccessKey", "iam:AttachRolePolicy", "iam:DeleteUser", "iam:CreateUser", "iam:CreateAccessKey", "iam:CreatePolicy", "iam:CreateLoginProfile", "iam:RemoveUserFromGroup", "iam:AddUserToGroup", "iam:DetachRolePolicy", "iam:DeleteSigningCertificate", "iam:AttachGroupPolicy", "iam:DeleteRolePolicy", "iam:DetachGroupPolicy", "iam:DetachUserPolicy", "iam:DeleteLoginProfile", "cloudtrail:DescribeTrails", "cloudtrail:GetEventSelectors", "cloudtrail:GetTrailStatus", "cloudtrail:ListTags", "cloudtrail:LookupEvents", "cloudtrail:Get*", "cloudtrail:Describe*", "cloudtrail:List*", "cloudwatch:Describe*", "cloudwatch:ListTagsForResource", "dynamodb:DescribeGlobalTable", "dynamodb:DescribeTable", "dynamodb:DescribeTimeToLive", "dynamodb:ListGlobalTables", "dynamodb:ListStreams", "dynamodb:ListTables", "dynamodb:ListTagsOfResource", "ec2:Describe*", "ec2:DescribeTransitGatewayAttachments", "ec2:DescribeTransitGatewayMulticastDomains", "ec2:DescribeTransitGatewayPeeringAttachments", "ec2:DescribeTransitGatewayRouteTables", "ec2:DescribeTransitGatewayVpcAttachments", "ec2:DescribeTransitGateways", "ec2:GetManagedPrefixListAssociations", "ec2:GetManagedPrefixListEntries", "ec2:GetTransitGatewayAttachmentPropagations", "ec2:GetTransitGatewayMulticastDomainAssociations", "ec2:GetTransitGatewayPrefixListReferences", "ec2:GetTransitGatewayRouteTableAssociations", "ec2:GetTransitGatewayRouteTablePropagations", "elasticloadbalancing:Describe*", "kms:Describe*", "kms:Get*", "kms:List*", "lambda:GetFunctionConfiguration", "lambda:GetFunctionEventInvokeConfig", "lambda:GetLayerVersionPolicy", "lambda:GetPolicy", "lambda:List*", "rds:Describe*", "rds:ListTagsForResource", "s3:GetAccessPoint", "s3:GetAccessPointPolicy", "s3:GetAccessPointPolicyStatus", "s3:GetAccountPublicAccessBlock", "s3:GetAnalyticsConfiguration", "s3:GetBucket*", "s3:GetEncryptionConfiguration", "s3:GetInventoryConfiguration", "s3:GetObjectAcl", "s3:GetObjectVersionAcl", "s3:GetReplicationConfiguration", "s3:ListAccessPoints", "s3:ListAllMyBuckets", "sns:GetTopicAttributes", "sns:ListSubscriptions", "sns:ListSubscriptionsByTopic", "sns:ListTagsForResource", "sns:ListTopics", "sqs:GetQueueAttributes", "sqs:ListDeadLetterSourceQueues", "sqs:ListQueueTags", "sqs:ListQueues", "tag:GetResources", "tag:GetTagKeys", "iam:GenerateCredentialReport", "iam:GenerateServiceLastAccessedDetails", "iam:SimulateCustomPolicy", "iam:SimulatePrincipalPolicy", "iam:ListUsers", "iam:ListAccessKeys", "iam:GetAccessKeyLastUsed", "iam:ListServiceSpecificCredentials", "iam:ListSSHPublicKeys", "iam:ListSigningCertificates", "bedrock:ListAgents", "bedrock:GetAgent", "bedrock:ListAgentActionGroups", "bedrock:GetAgentActionGroup", "bedrock:ListAgentKnowledgeBases", "bedrock:GetAgentKnowledgeBase", "bedrock:ListKnowledgeBases", "bedrock:GetKnowledgeBase", "bedrock:ListAgentAliases", "bedrock:GetAgentAlias", "bedrock:ListAgentVersions", "bedrock:GetAgentVersion", "bedrock:ListDataSources", "bedrock:GetDataSource", "bedrock:ListAgentCollaborators", "bedrock:GetAgentCollaborator", "kms:Decrypt", "kms:GenerateDataKey", "agent-registry:ListRegistries", "agent-registry:ListRegistryRecords", "agent-registry:GetRegistryRecord", "agent-registry:ListTagsForResource", "iam:DeleteGroup", "iam:DeleteGroupPolicy" ] } ] } } ], "Path": "/" } } }, "Outputs": { "SailPointAWSRoleARN": { "Description": "SailPoint AWS Role ARN", "Value": { "Fn::GetAtt": [ "SailPointAWSRole", "Arn" ] } }, "SailPointAWSRoleExternalId": { "Description": "SailPoint AWS Role External ID", "Value": { "Ref": "ExternalId" } } } -
-
-
Under Deployment regions, select a single region. Because IAM resources are account-level objects, they do not need to be created per region. This setup creates the roles and policies required to collect activity data from all AWS member accounts.
Collecting Resources from All AWS Accounts Using Stack
The following process creates a role and policies with minimum privileges in the management account.
Create an in-line policy on the role for reading resource data from your AWS cloud.
To enable inventory collection in all accounts:
-
Follow the AWS directions to create a stack in the root management account where logs are captured.
-
Upload the appropriate cloud formation template:
AWS accounts only
{
  "AWSTemplateFormatVersion": "2010-09-09",
  "Parameters": {
    "RoleName": {
      "Default": "SailPointAWSRole",
      "Description": "Role with this name will be created.",
      "Type": "String"
    },
    "ExternalId": {
      "Description": "Unique external ID needed for assuming role.",
      "Type": "String"
    },
    "RolePolicyName": {
      "Default": "SailPointAWSPolicy",
      "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.",
      "Type": "String"
    },
    "BucketName": {
      "Description": "Name of existing Bucket with CloudTrail logs.",
      "Type": "String"
    }
  },
  "Resources": {
    "SailPointAWSPolicy": {
      "Type": "AWS::IAM::ManagedPolicy",
      "DeletionPolicy": "Retain",
      "Properties": {
        "Description": "Policy for created for AWS Organizations",
        "Path": "/",
        "Roles": [
          {
            "Ref": "SailPointAWSRole"
          }
        ],
        "PolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Action": [
                "s3:GetBucketLocation",
                "s3:ListBucket"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  ":",
                  [
                    "arn:aws:s3::",
                    {
                      "Ref": "BucketName"
                    }
                  ]
                ]
              }
            },
            {
              "Action": [
                "s3:GetObject"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  "/",
                  [
                    {
                      "Fn::Join": [
                        ":",
                        [
                          "arn:aws:s3::",
                          {
                            "Ref": "BucketName"
                          }
                        ]
                      ]
                    },
                    ""
                  ]
                ]
              }
            }
          ]
        }
      }
    },
    "SailPointAWSRole": {
      "Type": "AWS::IAM::Role",
      "DeletionPolicy": "Retain",
      "Properties": {
        "RoleName": {
          "Ref": "RoleName"
        },
        "AssumeRolePolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Effect": "Allow",
              "Principal": {
                "AWS": "arn:aws:iam::874540850173:role/ciem_universal"
              },
              "Action": "sts:AssumeRole",
              "Condition": {
                "StringEquals": {
                  "sts:ExternalId": {
                    "Ref": "ExternalId"
                  }
                }
              }
            }
          ]
        },
        "Policies": [
          {
            "PolicyName": "SailPointAWSPolicy",
            "PolicyDocument": {
              "Version": "2012-10-17",
              "Statement": [
                {
                  "Effect": "Allow",
                  "Resource": "",
                  "Action": [
                    "iam:GetPolicyVersion",
                    "iam:ListServiceSpecificCredentials",
                    "iam:ListMFADevices",
                    "iam:ListSigningCertificates",
                    "iam:GetGroup",
                    "iam:ListSSHPublicKeys",
                    "iam:ListAttachedRolePolicies",
                    "iam:ListAttachedUserPolicies",
                    "iam:ListAttachedGroupPolicies",
                    "iam:ListRolePolicies",
                    "iam:ListAccessKeys",
                    "iam:ListPolicies",
                    "iam:GetRole",
                    "iam:GetPolicy",
                    "iam:ListGroupPolicies",
                    "iam:ListRoles",
                    "iam:ListUserPolicies",
                    "iam:GetUserPolicy",
                    "iam:ListGroupsForUser",
                    "iam:ListAccountAliases",
                    "iam:ListUsers",
                    "iam:ListGroups",
                    "iam:GetGroupPolicy",
                    "iam:GetUser",
                    "iam:GetRolePolicy",
                    "iam:GetLoginProfile",
                    "iam:ListEntitiesForPolicy",
                    "iam:GetAccessKeyLastUsed",
                    "iam:ListUserTags",
                    "iam:ListRoleTags",
                    "iam:ListPolicyTags",
                    "iam:UpdateLoginProfile",
                    "iam:UpdateAccessKey",
                    "iam:CreateUser",
                    "iam:CreateAccessKey",
                    "iam:CreateLoginProfile",
                    "iam:RemoveUserFromGroup",
                    "iam:AddUserToGroup",
                    "iam:DeleteLoginProfile",
                    "iam:AttachUserPolicy",

"organizations:ListPoliciesForTarget",
      "organizations:ListAccountsForParent",
      "organizations:ListRoots",
      "organizations:ListAccounts",
      "organizations:ListTargetsForPolicy",
      "organizations:DescribeOrganization",
      "organizations:DescribeOrganizationalUnit",
      "organizations:DescribeAccount",
      "organizations:ListParents",
      "organizations:ListOrganizationalUnitsForParent",
      "organizations:DescribePolicy",
    "organizations:ListPolicies",
     "organizations:ListTagsForResource",
     "iam:DeleteGroup",
     "iam:DeleteGroupPolicy"
                  ]
                }
              ]
            }
          }
        ],
        "Path": "/"
      }
    }
  },
  "Outputs": {
    "SailPointAWSRoleARN": {
      "Description": "SailPoint AWS Role ARN",
      "Value": {
        "Fn::GetAtt": [
          "SailPointAWSRole",
          "Arn"
        ]
      }
    },
    "SailPointAWSRoleExternalId": {
      "Description": "SailPoint AWS Role External ID",
      "Value": {
        "Ref": "ExternalId"
      }
    }
  }
}
AWS accounts with Activity Insights
Note
Ensure the role name matches the StackSet name previously specified.
{
  "AWSTemplateFormatVersion": "2010-09-09",
  "Parameters": {
    "RoleName": {
      "Default": "SailPointAWSRole",
      "Description": "Role with this name will be created.",
      "Type": "String"
    },
    "ExternalId": {
      "Description": "Unique external ID needed for assuming role.",
      "Type": "String"
    },
    "RolePolicyName": {
      "Default": "SailPointAWSPolicy",
      "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.",
      "Type": "String"
    },
    "BucketName": {
      "Description": "Name of existing Bucket with CloudTrail logs.",
      "Type": "String"
    }
  },
  "Resources": {
    "SailPointAWSPolicy": {
      "Type": "AWS::IAM::ManagedPolicy",
      "DeletionPolicy": "Retain",
      "Properties": {
        "Description": "Policy for created for AWS Organizations",
        "Path": "/",
        "Roles": [
          {
            "Ref": "SailPointAWSRole"
          }
        ],
        "PolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Action": [
                "s3:GetBucketLocation",
                "s3:ListBucket"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  ":",
                  [
                    "arn:aws:s3::",
                    {
                      "Ref": "BucketName"
                    }
                  ]
                ]
              }
            },
            {
              "Action": [
                "s3:GetObject"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  "/",
                  [
                    {
                      "Fn::Join": [
                        ":",
                        [
                          "arn:aws:s3::",
                          {
                            "Ref": "BucketName"
                          }
                        ]
                      ]
                    },
                    ""
                  ]
                ]
              }
            }
          ]
        }
      }
    },
    "SailPointAWSRole": {
      "Type": "AWS::IAM::Role",
      "DeletionPolicy": "Retain",
      "Properties": {
        "RoleName": {
          "Ref": "RoleName"
        },
        "AssumeRolePolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Effect": "Allow",
              "Principal": {
                "AWS": "arn:aws:iam::874540850173:role/ciem_universal"
              },
              "Action": "sts:AssumeRole",
              "Condition": {
                "StringEquals": {
                  "sts:ExternalId": {
                    "Ref": "ExternalId"
                  }
                }
              }
            }
          ]
        },
        "Policies": [
          {
            "PolicyName": "SailPointAWSPolicy",
            "PolicyDocument": {
              "Version": "2012-10-17",
              "Statement": [
                {
                  "Effect": "Allow",
                  "Resource": "",
                  "Action": [
                    "iam:GetPolicyVersion",
                    "iam:ListServiceSpecificCredentials",
                    "iam:ListMFADevices",
                    "iam:ListSigningCertificates",
                    "iam:GetGroup",
                    "iam:ListSSHPublicKeys",
                    "iam:ListAttachedRolePolicies",
                    "iam:ListAttachedUserPolicies",
                    "iam:ListAttachedGroupPolicies",
                    "iam:ListRolePolicies",
                    "iam:ListAccessKeys",
                    "iam:ListPolicies",
                    "iam:GetRole",
                    "iam:GetPolicy",
                    "iam:ListGroupPolicies",
                    "iam:ListRoles",
                    "iam:ListUserPolicies",
                    "iam:GetUserPolicy",
                    "iam:ListGroupsForUser",
                    "iam:ListAccountAliases",
                    "iam:ListUsers",
                    "iam:ListGroups",
                    "iam:GetGroupPolicy",
                    "iam:GetUser",
                    "iam:GetRolePolicy",
                    "iam:GetLoginProfile",
                    "iam:ListEntitiesForPolicy",
                    "iam:GetAccessKeyLastUsed",
                    "iam:ListUserTags",
                    "iam:ListRoleTags",
                    "iam:ListPolicyTags",
                    "iam:UpdateLoginProfile",
                    "iam:UpdateAccessKey",
                    "iam:CreateUser",
                    "iam:CreateAccessKey",
                    "iam:CreateLoginProfile",
                    "iam:RemoveUserFromGroup",
                    "iam:AddUserToGroup",
                    "iam:DeleteLoginProfile",
                    "iam:AttachUserPolicy",
                    "cloudtrail:Get*",
                    "cloudtrail:Describe*",
                    "cloudtrail:List*",
                    "cloudtrail:LookupEvents",

"organizations:ListPoliciesForTarget",
      "organizations:ListAccountsForParent",
      "organizations:ListRoots",
      "organizations:ListAccounts",
      "organizations:ListTargetsForPolicy",
      "organizations:DescribeOrganization",
      "organizations:DescribeOrganizationalUnit",
      "organizations:DescribeAccount",
      "organizations:ListParents",
      "organizations:ListOrganizationalUnitsForParent",
      "organizations:DescribePolicy",
    "organizations:ListPolicies",
     "organizations:ListTagsForResource",
     "iam:DeleteGroup",
     "iam:DeleteGroupPolicy"
                  ]
                }
              ]
            }
          }
        ],
        "Path": "/"
      }
    }
  },
  "Outputs": {
    "SailPointAWSRoleARN": {
      "Description": "SailPoint AWS Role ARN",
      "Value": {
        "Fn::GetAtt": [
          "SailPointAWSRole",
          "Arn"
        ]
      }
    },
    "SailPointAWSRoleExternalId": {
      "Description": "SailPoint AWS Role External ID",
      "Value": {
        "Ref": "ExternalId"
      }
    }
  }
}
AWS accounts with Agent Discovery
{
  "AWSTemplateFormatVersion": "2010-09-09",
  "Parameters": {
    "RoleName": {
      "Default": "SailPointAWSRole",
      "Description": "Role with this name will be created.",
      "Type": "String"
    },
    "ExternalId": {
      "Description": "Unique external ID needed for assuming role.",
      "Type": "String"
    },
    "RolePolicyName": {
      "Default": "SailPointAWSPolicy",
      "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.",
      "Type": "String"
    },
    "BucketName": {
      "Description": "Name of existing Bucket with CloudTrail logs.",
      "Type": "String"
    }
  },
  "Resources": {
    "SailPointAWSPolicy": {
      "Type": "AWS::IAM::ManagedPolicy",
      "DeletionPolicy": "Retain",
      "Properties": {
        "Description": "Policy for created for AWS Organizations",
        "Path": "/",
        "Roles": [
          {
            "Ref": "SailPointAWSRole"
          }
        ],
        "PolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Action": [
                "s3:GetBucketLocation",
                "s3:ListBucket"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  ":",
                  [
                    "arn:aws:s3::",
                    {
                      "Ref": "BucketName"
                    }
                  ]
                ]
              }
            },
            {
              "Action": [
                "s3:GetObject"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  "/",
                  [
                    {
                      "Fn::Join": [
                        ":",
                        [
                          "arn:aws:s3::",
                          {
                            "Ref": "BucketName"
                          }
                        ]
                      ]
                    },
                    ""
                  ]
                ]
              }
            }
          ]
        }
      }
    },
    "SailPointAWSRole": {
      "Type": "AWS::IAM::Role",
      "DeletionPolicy": "Retain",
      "Properties": {
        "RoleName": {
          "Ref": "RoleName"
        },
        "AssumeRolePolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Effect": "Allow",
              "Principal": {
                "AWS": "arn:aws:iam::874540850173:role/ciem_universal"
              },
              "Action": "sts:AssumeRole",
              "Condition": {
                "StringEquals": {
                  "sts:ExternalId": {
                    "Ref": "ExternalId"
                  }
                }
              }
            }
          ]
        },
        "Policies": [
          {
            "PolicyName": "SailPointAWSPolicy",
            "PolicyDocument": {
              "Version": "2012-10-17",
              "Statement": [
                {
                  "Effect": "Allow",
                  "Resource": "",
                  "Action": [
                    "iam:GetPolicyVersion",
                    "iam:ListServiceSpecificCredentials",
                    "iam:ListMFADevices",
                    "iam:ListSigningCertificates",
                    "iam:GetGroup",
                    "iam:ListSSHPublicKeys",
                    "iam:ListAttachedRolePolicies",
                    "iam:ListAttachedUserPolicies",
                    "iam:ListAttachedGroupPolicies",
                    "iam:ListRolePolicies",
                    "iam:ListAccessKeys",
                    "iam:ListPolicies",
                    "iam:GetRole",
                    "iam:GetPolicy",
                    "iam:ListGroupPolicies",
                    "iam:ListRoles",
                    "iam:ListUserPolicies",
                    "iam:GetUserPolicy",
                    "iam:ListGroupsForUser",
                    "iam:ListAccountAliases",
                    "iam:ListUsers",
                    "iam:ListGroups",
                    "iam:GetGroupPolicy",
                    "iam:GetUser",
                    "iam:GetRolePolicy",
                    "iam:GetLoginProfile",
                    "iam:ListEntitiesForPolicy",
                    "iam:GetAccessKeyLastUsed",
                    "iam:ListUserTags",
                    "iam:ListRoleTags",
                    "iam:ListPolicyTags",
                    "iam:UpdateLoginProfile",
                    "iam:UpdateAccessKey",
                    "iam:CreateUser",
                    "iam:CreateAccessKey",
                    "iam:CreateLoginProfile",
                    "iam:RemoveUserFromGroup",
                    "iam:AddUserToGroup",
                    "iam:DeleteLoginProfile",
                    "iam:AttachUserPolicy",
                    "bedrock:ListAgents",
                    "bedrock:GetAgent",
                    "bedrock:ListAgentActionGroups",
                    "bedrock:GetAgentActionGroup",
                    "bedrock:ListAgentKnowledgeBases",
                    "bedrock:GetAgentKnowledgeBase",
                    "bedrock:ListKnowledgeBases",
                    "bedrock:GetKnowledgeBase",
                    "bedrock:ListAgentAliases",
                    "bedrock:GetAgentAlias",
                    "bedrock:ListAgentVersions",
                    "bedrock:GetAgentVersion",
                    "bedrock:ListDataSources",
                    "bedrock:GetDataSource",
                    "bedrock:ListAgentCollaborators",
                    "bedrock:GetAgentCollaborator",
                    "kms:Decrypt",
                    "kms:GenerateDataKey",
                    "bedrock-agentcore:ListAgentRuntimes",
                    "bedrock-agentcore:GetAgentRuntime",
                    "bedrock-agentcore:ListAgentRuntimeEndpoints",
                    "bedrock-agentcore:GetAgentRuntimeEndpoint",
                    "bedrock-agentcore:ListAgentRuntimeVersions",
                    "bedrock-agentcore:ListWorkloadIdentities",
                    "bedrock-agentcore:GetWorkloadIdentity",
                    "bedrock-agentcore:ListOauth2CredentialProviders",
                    "bedrock-agentcore:GetApiKeyCredentialProvider",
                    "bedrock-agentcore:ListApiKeyCredentialProviders",
                    "bedrock-agentcore:GetOauth2CredentialProvider",

"organizations:ListPoliciesForTarget",
      "organizations:ListAccountsForParent",
      "organizations:ListRoots",
      "organizations:ListAccounts",
      "organizations:ListTargetsForPolicy",
      "organizations:DescribeOrganization",
      "organizations:DescribeOrganizationalUnit",
      "organizations:DescribeAccount",
      "organizations:ListParents",
      "organizations:ListOrganizationalUnitsForParent",
      "organizations:DescribePolicy",
    "organizations:ListPolicies",
     "organizations:ListTagsForResource",
     "iam:DeleteGroup",
     "iam:DeleteGroupPolicy"
                  ]
                }
              ]
            }
          }
        ],
        "Path": "/"
      }
    }
  },
  "Outputs": {
    "SailPointAWSRoleARN": {
      "Description": "SailPoint AWS Role ARN",
      "Value": {
        "Fn::GetAtt": [
          "SailPointAWSRole",
          "Arn"
        ]
      }
    },
    "SailPointAWSRoleExternalId": {
      "Description": "SailPoint AWS Role External ID",
      "Value": {
        "Ref": "ExternalId"
      }
    }
  }
}
AWS accounts with CIEM and Activity Insights
{
  "AWSTemplateFormatVersion": "2010-09-09",
  "Parameters": {
    "RoleName": {
      "Default": "SailPointAWSRole",
      "Description": "Role with this name will be created.",
      "Type": "String"
    },
    "ExternalId": {
      "Description": "Unique external ID needed for assuming role.",
      "Type": "String"
    },
    "RolePolicyName": {
      "Default": "SailPointAWSPolicy",
      "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.",
      "Type": "String"
    },
    "BucketName": {
      "Description": "Name of existing Bucket with CloudTrail logs.",
      "Type": "String"
    }
  },
  "Resources": {
    "SailPointAWSPolicy": {
      "Type": "AWS::IAM::ManagedPolicy",
      "DeletionPolicy": "Retain",
      "Properties": {
        "Description": "Policy for created for AWS Organizations",
        "Path": "/",
        "Roles": [
          {
            "Ref": "SailPointAWSRole"
          }
        ],
        "PolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Action": [
                "s3:GetBucketLocation",
                "s3:ListBucket"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  ":",
                  [
                    "arn:aws:s3::",
                    {
                      "Ref": "BucketName"
                    }
                  ]
                ]
              }
            },
            {
              "Action": [
                "s3:GetObject"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  "/",
                  [
                    {
                      "Fn::Join": [
                        ":",
                        [
                          "arn:aws:s3::",
                          {
                            "Ref": "BucketName"
                          }
                        ]
                      ]
                    },
                    "*"
                  ]
                ]
              }
            }
          ]
        }
      }
    },
    "SailPointAWSRole": {
      "Type": "AWS::IAM::Role",
      "DeletionPolicy": "Retain",
      "Properties": {
        "RoleName": {
          "Ref": "RoleName"
        },
        "AssumeRolePolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Effect": "Allow",
              "Principal": {
                "AWS": "arn:aws:iam::874540850173:role/ciem_universal"
              },
              "Action": "sts:AssumeRole",
              "Condition": {
                "StringEquals": {
                  "sts:ExternalId": {
                    "Ref": "ExternalId"
                  }
                }
              }
            }
          ]
        },
        "Policies": [
          {
            "PolicyName": "SailPointAWSPolicy",
            "PolicyDocument": {
              "Version": "2012-10-17",
              "Statement": [
                {
                  "Effect": "Allow",
                  "Resource": "*",
                  "Action": [
                    "organizations:Describe*",
                    "organizations:List*",
                    "iam:Get*",
                    "iam:List*",
                    "iam:UpdateLoginProfile",
                    "iam:CreateGroup",
                    "iam:DeleteAccessKey",
                    "iam:AttachUserPolicy",
                    "iam:DeleteUserPolicy",
                    "iam:UpdateAccessKey",
                    "iam:AttachRolePolicy",
                    "iam:DeleteUser",
                    "iam:CreateUser",
                    "iam:CreateAccessKey",
                    "iam:CreatePolicy",
                    "iam:CreateLoginProfile",
                    "iam:RemoveUserFromGroup",
                    "iam:AddUserToGroup",
                    "iam:DetachRolePolicy",
                    "iam:DeleteSigningCertificate",
                    "iam:AttachGroupPolicy",
                    "iam:DeleteRolePolicy",
                    "iam:DetachGroupPolicy",
                    "iam:DetachUserPolicy",
                    "iam:DeleteLoginProfile",
                    "cloudtrail:DescribeTrails",
                    "cloudtrail:GetEventSelectors",
                    "cloudtrail:GetTrailStatus",
                    "cloudtrail:ListTags",
                    "cloudtrail:LookupEvents",
                    "cloudtrail:Get*",
                    "cloudtrail:Describe*",
                    "cloudtrail:List*",
                    "cloudwatch:Describe*",
                    "cloudwatch:ListTagsForResource",
                    "dynamodb:DescribeGlobalTable",
                    "dynamodb:DescribeTable",
                    "dynamodb:DescribeTimeToLive",
                    "dynamodb:ListGlobalTables",
                    "dynamodb:ListStreams",
                    "dynamodb:ListTables",
                    "dynamodb:ListTagsOfResource",
                    "ec2:Describe*",
                    "ec2:DescribeTransitGatewayAttachments",
                    "ec2:DescribeTransitGatewayMulticastDomains",
                    "ec2:DescribeTransitGatewayPeeringAttachments",
                    "ec2:DescribeTransitGatewayRouteTables",
                    "ec2:DescribeTransitGatewayVpcAttachments",
                    "ec2:DescribeTransitGateways",
                    "ec2:GetManagedPrefixListAssociations",
                    "ec2:GetManagedPrefixListEntries",
                    "ec2:GetTransitGatewayAttachmentPropagations",
                    "ec2:GetTransitGatewayMulticastDomainAssociations",
                    "ec2:GetTransitGatewayPrefixListReferences",
                    "ec2:GetTransitGatewayRouteTableAssociations",
                    "ec2:GetTransitGatewayRouteTablePropagations",
                    "elasticloadbalancing:Describe*",
                    "kms:Describe*",
                    "kms:Get*",
                    "kms:List*",
                    "lambda:GetFunctionConfiguration",
                    "lambda:GetFunctionEventInvokeConfig",
                    "lambda:GetLayerVersionPolicy",
                    "lambda:GetPolicy",
                    "lambda:List*",
                    "rds:Describe*",
                    "rds:ListTagsForResource",
                    "s3:GetAccessPoint",
                    "s3:GetAccessPointPolicy",
                    "s3:GetAccessPointPolicyStatus",
                    "s3:GetAccountPublicAccessBlock",
                    "s3:GetAnalyticsConfiguration",
                    "s3:GetBucket*",
                    "s3:GetEncryptionConfiguration",
                    "s3:GetInventoryConfiguration",
                    "s3:GetObjectAcl",
                    "s3:GetObjectVersionAcl",
                    "s3:GetReplicationConfiguration",
                    "s3:ListAccessPoints",
                    "s3:ListAllMyBuckets",
                    "sns:GetTopicAttributes",
                    "sns:ListSubscriptions",
                    "sns:ListSubscriptionsByTopic",
                    "sns:ListTagsForResource",
                    "sns:ListTopics",
                    "sqs:GetQueueAttributes",
                    "sqs:ListDeadLetterSourceQueues",
                    "sqs:ListQueueTags",
                    "sqs:ListQueues",
                    "tag:GetResources",
                    "tag:GetTagKeys",
                    "iam:GenerateCredentialReport",
                    "iam:GenerateServiceLastAccessedDetails",
                    "iam:SimulateCustomPolicy",
                    "iam:SimulatePrincipalPolicy",
                    "iam:DeleteGroup",
                    "iam:DeleteGroupPolicy"
                  ]
                }
              ]
            }
          }
        ],
        "Path": "/"
      }
    }
  },
  "Outputs": {
    "SailPointAWSRoleARN": {
      "Description": "SailPoint AWS Role ARN",
      "Value": {
        "Fn::GetAtt": [
          "SailPointAWSRole",
          "Arn"
        ]
      }
    },
    "SailPointAWSRoleExternalId": {
      "Description": "SailPoint AWS Role External ID",
      "Value": {
        "Ref": "ExternalId"
      }
    }
  }
}
{ "AWSTemplateFormatVersion" : "2010-09-09", "Parameters": { "RoleName": { "Default": "SailPointAWSRole", "Description": "Role with this name will be created.", "Type": "String" }, "ExternalId": { "Description": "Unique external ID needed for assuming role.", "Type": "String" }, "RolePolicyName": { "Default": "SailPointAWSPolicy", "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.", "Type": "String" }, "BucketName": { "Description": "Name of existing Bucket with CloudTrail logs.", "Type": "String" } }, "Resources" : { "SailPointAWSPolicy": { "Type": "AWS::IAM::ManagedPolicy", "DeletionPolicy": "Retain", "Properties": { "Description": "Policy for created for AWS Organizations", "Path": "/", "Roles": [ { "Ref": "SailPointAWSRole" } ], "PolicyDocument": { "Version": "2012-10-17", "Statement": [ { "Action": [ "s3:GetBucketLocation", "s3:ListBucket" ], "Effect": "Allow", "Resource": { "Fn::Join": [ ":", [ "arn:aws:s3::", { "Ref": "BucketName" } ] ] } }, { "Action": [ "s3:GetObject" ], "Effect": "Allow", "Resource": { "Fn::Join": [ "/", [ { "Fn::Join": [ ":", [ "arn:aws:s3::", { "Ref": "BucketName" } ] ] }, "*" ] ] } } ] } } }, "SailPointAWSRole": { "Type": "AWS::IAM::Role", "DeletionPolicy": "Retain", "Properties": { "RoleName": { "Ref": "RoleName" }, "AssumeRolePolicyDocument": { "Version": "2012-10-17", "Statement": [ { "Effect": "Allow", "Principal": { "AWS": [ "arn:aws-us-gov:iam::229634586956:role/ciem_universal" ] }, "Action": "sts:AssumeRole", "Condition": { "StringEquals": { "sts:ExternalId": { "Ref": "ExternalId" } } } } ] }, "Policies": [ { "PolicyName" : "SailPointAWSPolicy", "PolicyDocument" : { "Version":"2012-10-17", "Statement":[ { "Effect":"Allow", "Resource":"*", "Action":[ "organizations:Describe*", "organizations:List*", "iam:Get*", "iam:List*", "iam:UpdateLoginProfile", "iam:CreateGroup", "iam:DeleteAccessKey", "iam:AttachUserPolicy", "iam:DeleteUserPolicy", "iam:UpdateAccessKey", "iam:AttachRolePolicy", "iam:DeleteUser", "iam:CreateUser", "iam:CreateAccessKey", "iam:CreatePolicy", "iam:CreateLoginProfile", "iam:RemoveUserFromGroup", "iam:AddUserToGroup", "iam:DetachRolePolicy", "iam:DeleteSigningCertificate", "iam:AttachGroupPolicy", "iam:DeleteRolePolicy", "iam:DetachGroupPolicy", "iam:DetachUserPolicy", "iam:DeleteLoginProfile", "cloudtrail:DescribeTrails", "cloudtrail:GetEventSelectors", "cloudtrail:GetTrailStatus", "cloudtrail:ListTags", "cloudtrail:LookupEvents", "cloudtrail:Get*", "cloudtrail:Describe*", "cloudtrail:List*", "cloudwatch:Describe*", "cloudwatch:ListTagsForResource", "dynamodb:DescribeGlobalTable", "dynamodb:DescribeTable", "dynamodb:DescribeTimeToLive", "dynamodb:ListGlobalTables", "dynamodb:ListStreams", "dynamodb:ListTables", "dynamodb:ListTagsOfResource", "ec2:Describe*", "ec2:DescribeTransitGatewayAttachments", "ec2:DescribeTransitGatewayMulticastDomains", "ec2:DescribeTransitGatewayPeeringAttachments", "ec2:DescribeTransitGatewayRouteTables", "ec2:DescribeTransitGatewayVpcAttachments", "ec2:DescribeTransitGateways", "ec2:GetManagedPrefixListAssociations", "ec2:GetManagedPrefixListEntries", "ec2:GetTransitGatewayAttachmentPropagations", "ec2:GetTransitGatewayMulticastDomainAssociations", "ec2:GetTransitGatewayPrefixListReferences", "ec2:GetTransitGatewayRouteTableAssociations", "ec2:GetTransitGatewayRouteTablePropagations", "elasticloadbalancing:Describe*", "kms:Describe*", "kms:Get*", "kms:List*", "lambda:GetFunctionConfiguration", "lambda:GetFunctionEventInvokeConfig", "lambda:GetLayerVersionPolicy", "lambda:GetPolicy", "lambda:List*", "rds:Describe*", "rds:ListTagsForResource", "s3:GetAccessPoint", "s3:GetAccessPointPolicy", "s3:GetAccessPointPolicyStatus", "s3:GetAccountPublicAccessBlock", "s3:GetAnalyticsConfiguration", "s3:GetBucket*", "s3:GetEncryptionConfiguration", "s3:GetInventoryConfiguration", "s3:GetObjectAcl", "s3:GetObjectVersionAcl", "s3:GetReplicationConfiguration", "s3:ListAccessPoints", "s3:ListAllMyBuckets", "sns:GetTopicAttributes", "sns:ListSubscriptions", "sns:ListSubscriptionsByTopic", "sns:ListTagsForResource", "sns:ListTopics", "sqs:GetQueueAttributes", "sqs:ListDeadLetterSourceQueues", "sqs:ListQueueTags", "sqs:ListQueues", "tag:GetResources", "tag:GetTagKeys", "iam:GenerateCredentialReport", "iam:GenerateServiceLastAccessedDetails", "iam:SimulateCustomPolicy", "iam:SimulatePrincipalPolicy", "iam:DeleteGroup", "iam:DeleteGroupPolicy" ] } ] } } ], "Path": "/" } } }, "Outputs": { "SailPointAWSRoleARN": { "Description": "SailPoint AWS Role ARN", "Value": { "Fn::GetAtt": [ "SailPointAWSRole", "Arn" ] } }, "SailPointAWSRoleExternalId": { "Description": "SailPoint AWS Role External ID", "Value": { "Ref": "ExternalId" } } }AWS accounts with CIEM, Activity Insights, and Agent Discovery
{
  "AWSTemplateFormatVersion": "2010-09-09",
  "Parameters": {
    "RoleName": {
      "Default": "SailPointAWSRole",
      "Description": "Role with this name will be created.",
      "Type": "String"
    },
    "ExternalId": {
      "Description": "Unique external ID needed for assuming role.",
      "Type": "String"
    },
    "RolePolicyName": {
      "Default": "SailPointAWSPolicy",
      "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.",
      "Type": "String"
    },
    "BucketName": {
      "Description": "Name of existing Bucket with CloudTrail logs.",
      "Type": "String"
    }
  },
  "Resources": {
    "SailPointAWSPolicy": {
      "Type": "AWS::IAM::ManagedPolicy",
      "DeletionPolicy": "Retain",
      "Properties": {
        "Description": "Policy for created for AWS Organizations",
        "Path": "/",
        "Roles": [
          {
            "Ref": "SailPointAWSRole"
          }
        ],
        "PolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Action": [
                "s3:GetBucketLocation",
                "s3:ListBucket"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  ":",
                  [
                    "arn:aws:s3::",
                    {
                      "Ref": "BucketName"
                    }
                  ]
                ]
              }
            },
            {
              "Action": [
                "s3:GetObject"
              ],
              "Effect": "Allow",
              "Resource": {
                "Fn::Join": [
                  "/",
                  [
                    {
                      "Fn::Join": [
                        ":",
                        [
                          "arn:aws:s3::",
                          {
                            "Ref": "BucketName"
                          }
                        ]
                      ]
                    },
                    "*"
                  ]
                ]
              }
            }
          ]
        }
      }
    },
    "SailPointAWSRole": {
      "Type": "AWS::IAM::Role",
      "DeletionPolicy": "Retain",
      "Properties": {
        "RoleName": {
          "Ref": "RoleName"
        },
        "AssumeRolePolicyDocument": {
          "Version": "2012-10-17",
          "Statement": [
            {
              "Effect": "Allow",
              "Principal": {
                "AWS": "arn:aws:iam::874540850173:role/ciem_universal"
              },
              "Action": "sts:AssumeRole",
              "Condition": {
                "StringEquals": {
                  "sts:ExternalId": {
                    "Ref": "ExternalId"
                  }
                }
              }
            }
          ]
        },
        "Policies": [
          {
            "PolicyName": "SailPointAWSPolicy",
            "PolicyDocument": {
              "Version": "2012-10-17",
              "Statement": [
                {
                  "Effect": "Allow",
                  "Resource": "*",
                  "Action": [
                    "organizations:Describe*",
                    "organizations:List*",
                    "iam:Get*",
                    "iam:List*",
                    "iam:UpdateLoginProfile",
                    "iam:CreateGroup",
                    "iam:DeleteAccessKey",
                    "iam:AttachUserPolicy",
                    "iam:DeleteUserPolicy",
                    "iam:UpdateAccessKey",
                    "iam:AttachRolePolicy",
                    "iam:DeleteUser",
                    "iam:CreateUser",
                    "iam:CreateAccessKey",
                    "iam:CreatePolicy",
                    "iam:CreateLoginProfile",
                    "iam:RemoveUserFromGroup",
                    "iam:AddUserToGroup",
                    "iam:DetachRolePolicy",
                    "iam:DeleteSigningCertificate",
                    "iam:AttachGroupPolicy",
                    "iam:DeleteRolePolicy",
                    "iam:DetachGroupPolicy",
                    "iam:DetachUserPolicy",
                    "iam:DeleteLoginProfile",
                    "cloudtrail:DescribeTrails",
                    "cloudtrail:GetEventSelectors",
                    "cloudtrail:GetTrailStatus",
                    "cloudtrail:ListTags",
                    "cloudtrail:LookupEvents",
                    "cloudtrail:Get*",
                    "cloudtrail:Describe*",
                    "cloudtrail:List*",
                    "cloudwatch:Describe*",
                    "cloudwatch:ListTagsForResource",
                    "dynamodb:DescribeGlobalTable",
                    "dynamodb:DescribeTable",
                    "dynamodb:DescribeTimeToLive",
                    "dynamodb:ListGlobalTables",
                    "dynamodb:ListStreams",
                    "dynamodb:ListTables",
                    "dynamodb:ListTagsOfResource",
                    "ec2:Describe*",
                    "ec2:DescribeTransitGatewayAttachments",
                    "ec2:DescribeTransitGatewayMulticastDomains",
                    "ec2:DescribeTransitGatewayPeeringAttachments",
                    "ec2:DescribeTransitGatewayRouteTables",
                    "ec2:DescribeTransitGatewayVpcAttachments",
                    "ec2:DescribeTransitGateways",
                    "ec2:GetManagedPrefixListAssociations",
                    "ec2:GetManagedPrefixListEntries",
                    "ec2:GetTransitGatewayAttachmentPropagations",
                    "ec2:GetTransitGatewayMulticastDomainAssociations",
                    "ec2:GetTransitGatewayPrefixListReferences",
                    "ec2:GetTransitGatewayRouteTableAssociations",
                    "ec2:GetTransitGatewayRouteTablePropagations",
                    "elasticloadbalancing:Describe*",
                    "kms:Describe*",
                    "kms:Get*",
                    "kms:List*",
                    "lambda:GetFunctionConfiguration",
                    "lambda:GetFunctionEventInvokeConfig",
                    "lambda:GetLayerVersionPolicy",
                    "lambda:GetPolicy",
                    "lambda:List*",
                    "rds:Describe*",
                    "rds:ListTagsForResource",
                    "s3:GetAccessPoint",
                    "s3:GetAccessPointPolicy",
                    "s3:GetAccessPointPolicyStatus",
                    "s3:GetAccountPublicAccessBlock",
                    "s3:GetAnalyticsConfiguration",
                    "s3:GetBucket*",
                    "s3:GetEncryptionConfiguration",
                    "s3:GetInventoryConfiguration",
                    "s3:GetObjectAcl",
                    "s3:GetObjectVersionAcl",
                    "s3:GetReplicationConfiguration",
                    "s3:ListAccessPoints",
                    "s3:ListAllMyBuckets",
                    "sns:GetTopicAttributes",
                    "sns:ListSubscriptions",
                    "sns:ListSubscriptionsByTopic",
                    "sns:ListTagsForResource",
                    "sns:ListTopics",
                    "sqs:GetQueueAttributes",
                    "sqs:ListDeadLetterSourceQueues",
                    "sqs:ListQueueTags",
                    "sqs:ListQueues",
                    "tag:GetResources",
                    "tag:GetTagKeys",
                    "iam:GenerateCredentialReport",
                    "iam:GenerateServiceLastAccessedDetails",
                    "iam:SimulateCustomPolicy",
                    "iam:SimulatePrincipalPolicy",
                    "iam:ListUsers",
                    "iam:ListAccessKeys",
                    "iam:GetAccessKeyLastUsed",
                    "iam:ListServiceSpecificCredentials",
                    "iam:ListSSHPublicKeys",
                    "iam:ListSigningCertificates",
                    "bedrock:ListAgents",
                    "bedrock:GetAgent",
                    "bedrock:ListAgentActionGroups",
                    "bedrock:GetAgentActionGroup",
                    "bedrock:ListAgentKnowledgeBases",
                    "bedrock:GetAgentKnowledgeBase",
                    "bedrock:ListKnowledgeBases",
                    "bedrock:GetKnowledgeBase",
                    "bedrock:ListAgentAliases",
                    "bedrock:GetAgentAlias",
                    "bedrock:ListAgentVersions",
                    "bedrock:GetAgentVersion",
                    "bedrock:ListDataSources",
                    "bedrock:GetDataSource",
                    "bedrock:ListAgentCollaborators",
                    "bedrock:GetAgentCollaborator",
                    "kms:Decrypt",
                    "kms:GenerateDataKey",
                    "bedrock-agentcore:ListAgentRuntimes",
                    "bedrock-agentcore:GetAgentRuntime",
                    "bedrock-agentcore:ListAgentRuntimeEndpoints",
                    "bedrock-agentcore:GetAgentRuntimeEndpoint",
                    "bedrock-agentcore:ListAgentRuntimeVersions",
                    "bedrock-agentcore:ListWorkloadIdentities",
                    "bedrock-agentcore:GetWorkloadIdentity",
                    "bedrock-agentcore:ListOauth2CredentialProviders",
                    "bedrock-agentcore:GetApiKeyCredentialProvider",
                    "bedrock-agentcore:ListApiKeyCredentialProviders",
                    "bedrock-agentcore:GetOauth2CredentialProvider",
                    "connect:ListInstances",
                    "connect:ListIntegrationAssociations",
                    "wisdom:GetAssistant",
                    "wisdom:ListAIAgents",
                    "wisdom:ListAIAgentVersions",
                    "wisdom:GetAIAgent",
                    "quicksight:ListAgents",
                    "quicksight:DescribeAgent",
                    "quicksight:DescribeAgentPermissions",
                    "quicksight:ListActionConnectors",
                    "quicksight:DescribeActionConnector",
                    "quicksight:DescribeActionConnectorPermissions",
                    "agent-registry:ListRegistries",
                    "agent-registry:ListRegistryRecords",
                    "agent-registry:GetRegistryRecord",
                    "agent-registry:ListTagsForResource",
                    "iam:DeleteGroup",
                    "iam:DeleteGroupPolicy"

                  ]
                }
              ]
            }
          }
        ],
        "Path": "/"
      }
    }
  },
  "Outputs": {
    "SailPointAWSRoleARN": {
      "Description": "SailPoint AWS Role ARN",
      "Value": {
        "Fn::GetAtt": [
          "SailPointAWSRole",
          "Arn"
        ]
      }
    },
    "SailPointAWSRoleExternalId": {
      "Description": "SailPoint AWS Role External ID",
      "Value": {
        "Ref": "ExternalId"
      }
    }
  }
}
Note
Amazon Bedrock AgentCore agents are not supported in AWS GovCloud. For more information about the support of this regional service, refer to AWS Regions in the AWS documentation.
Important
-
Amazon Bedrock AgentCore agents are not supported in AWS GovCloud. For more information about the support of this regional service, refer to AWS Regions in the AWS documentation.
-
Amazon Connect Customer agent discovery actions aren't included in this AWS GovCloud template. The following list of Amazon Connect instance APIs is still valid for partition.
connect:ListInstancesconnect:ListIntegrationAssociations"connect:DescribeInstance""connect:ListEntitySecurityProfiles""connect:DescribeSecurityProfile"
Confirm regional availability for Amazon Q in Connect and the
wisdom:*APIs before adding the following actions:"wisdom:GetAssistant""wisdom:ListAIAgents""wisdom:ListAIAgentVersions""wisdom:GetAIAgent""wisdom:GetAssistantAssociation""wisdom:GetKnowledgeBase""wisdom:GetAIPrompt""wisdom:GetAIGuardrail"
-
Amazon Quick agent discovery actions aren't included in this AWS GovCloud template. Confirm regional availability for Amazon Quick and the
quicksight:*APIs before adding the actions listed in Machine Identity Governance Policies. -
AWS Agent Registry discovery actions aren't included in this AWS GovCloud template. Confirm regional availability for AWS Agent Registry and the
agent-registry:*APIs before adding the actions listed in Machine Identity Governance Policies.
{ "AWSTemplateFormatVersion" : "2010-09-09", "Parameters": { "RoleName": { "Default": "SailPointAWSRole", "Description": "Role with this name will be created.", "Type": "String" }, "ExternalId": { "Description": "Unique external ID needed for assuming role.", "Type": "String" }, "RolePolicyName": { "Default": "SailPointAWSPolicy", "Description": "Policy to allow SailPoint Role to read objects under the specified Cloud Trail Bucket.", "Type": "String" }, "BucketName": { "Description": "Name of existing Bucket with CloudTrail logs.", "Type": "String" } }, "Resources" : { "SailPointAWSPolicy": { "Type": "AWS::IAM::ManagedPolicy", "DeletionPolicy": "Retain", "Properties": { "Description": "Policy for created for AWS Organizations", "Path": "/", "Roles": [ { "Ref": "SailPointAWSRole" } ], "PolicyDocument": { "Version": "2012-10-17", "Statement": [ { "Action": [ "s3:GetBucketLocation", "s3:ListBucket" ], "Effect": "Allow", "Resource": { "Fn::Join": [ ":", [ "arn:aws:s3::", { "Ref": "BucketName" } ] ] } }, { "Action": [ "s3:GetObject" ], "Effect": "Allow", "Resource": { "Fn::Join": [ "/", [ { "Fn::Join": [ ":", [ "arn:aws:s3::", { "Ref": "BucketName" } ] ] }, "*" ] ] } } ] } } }, "SailPointAWSRole": { "Type": "AWS::IAM::Role", "DeletionPolicy": "Retain", "Properties": { "RoleName": { "Ref": "RoleName" }, "AssumeRolePolicyDocument": { "Version": "2012-10-17", "Statement": [ { "Effect": "Allow", "Principal": { "AWS": [ "arn:aws-us-gov:iam::229634586956:role/ciem_universal" ] }, "Action": "sts:AssumeRole", "Condition": { "StringEquals": { "sts:ExternalId": { "Ref": "ExternalId" } } } } ] }, "Policies": [ { "PolicyName" : "SailPointAWSPolicy", "PolicyDocument" : { "Version":"2012-10-17", "Statement":[ { "Effect":"Allow", "Resource":"*", "Action":[ "organizations:Describe*", "organizations:List*", "iam:Get*", "iam:List*", "iam:UpdateLoginProfile", "iam:CreateGroup", "iam:DeleteAccessKey", "iam:AttachUserPolicy", "iam:DeleteUserPolicy", "iam:UpdateAccessKey", "iam:AttachRolePolicy", "iam:DeleteUser", "iam:CreateUser", "iam:CreateAccessKey", "iam:CreatePolicy", "iam:CreateLoginProfile", "iam:RemoveUserFromGroup", "iam:AddUserToGroup", "iam:DetachRolePolicy", "iam:DeleteSigningCertificate", "iam:AttachGroupPolicy", "iam:DeleteRolePolicy", "iam:DetachGroupPolicy", "iam:DetachUserPolicy", "iam:DeleteLoginProfile", "cloudtrail:DescribeTrails", "cloudtrail:GetEventSelectors", "cloudtrail:GetTrailStatus", "cloudtrail:ListTags", "cloudtrail:LookupEvents", "cloudtrail:Get*", "cloudtrail:Describe*", "cloudtrail:List*", "cloudwatch:Describe*", "cloudwatch:ListTagsForResource", "dynamodb:DescribeGlobalTable", "dynamodb:DescribeTable", "dynamodb:DescribeTimeToLive", "dynamodb:ListGlobalTables", "dynamodb:ListStreams", "dynamodb:ListTables", "dynamodb:ListTagsOfResource", "ec2:Describe*", "ec2:DescribeTransitGatewayAttachments", "ec2:DescribeTransitGatewayMulticastDomains", "ec2:DescribeTransitGatewayPeeringAttachments", "ec2:DescribeTransitGatewayRouteTables", "ec2:DescribeTransitGatewayVpcAttachments", "ec2:DescribeTransitGateways", "ec2:GetManagedPrefixListAssociations", "ec2:GetManagedPrefixListEntries", "ec2:GetTransitGatewayAttachmentPropagations", "ec2:GetTransitGatewayMulticastDomainAssociations", "ec2:GetTransitGatewayPrefixListReferences", "ec2:GetTransitGatewayRouteTableAssociations", "ec2:GetTransitGatewayRouteTablePropagations", "elasticloadbalancing:Describe*", "kms:Describe*", "kms:Get*", "kms:List*", "lambda:GetFunctionConfiguration", "lambda:GetFunctionEventInvokeConfig", "lambda:GetLayerVersionPolicy", "lambda:GetPolicy", "lambda:List*", "rds:Describe*", "rds:ListTagsForResource", "s3:GetAccessPoint", "s3:GetAccessPointPolicy", "s3:GetAccessPointPolicyStatus", "s3:GetAccountPublicAccessBlock", "s3:GetAnalyticsConfiguration", "s3:GetBucket*", "s3:GetEncryptionConfiguration", "s3:GetInventoryConfiguration", "s3:GetObjectAcl", "s3:GetObjectVersionAcl", "s3:GetReplicationConfiguration", "s3:ListAccessPoints", "s3:ListAllMyBuckets", "sns:GetTopicAttributes", "sns:ListSubscriptions", "sns:ListSubscriptionsByTopic", "sns:ListTagsForResource", "sns:ListTopics", "sqs:GetQueueAttributes", "sqs:ListDeadLetterSourceQueues", "sqs:ListQueueTags", "sqs:ListQueues", "tag:GetResources", "tag:GetTagKeys", "iam:GenerateCredentialReport", "iam:GenerateServiceLastAccessedDetails", "iam:SimulateCustomPolicy", "iam:SimulatePrincipalPolicy", "iam:ListUsers", "iam:ListAccessKeys", "iam:GetAccessKeyLastUsed", "iam:ListServiceSpecificCredentials", "iam:ListSSHPublicKeys", "iam:ListSigningCertificates", "bedrock:ListAgents", "bedrock:GetAgent", "bedrock:ListAgentActionGroups", "bedrock:GetAgentActionGroup", "bedrock:ListAgentKnowledgeBases", "bedrock:GetAgentKnowledgeBase", "bedrock:ListKnowledgeBases", "bedrock:GetKnowledgeBase", "bedrock:ListAgentAliases", "bedrock:GetAgentAlias", "bedrock:ListAgentVersions", "bedrock:GetAgentVersion", "bedrock:ListDataSources", "bedrock:GetDataSource", "bedrock:ListAgentCollaborators", "bedrock:GetAgentCollaborator", "kms:Decrypt", "kms:GenerateDataKey", "agent-registry:ListRegistries", "agent-registry:ListRegistryRecords", "agent-registry:GetRegistryRecord", "agent-registry:ListTagsForResource", "iam:DeleteGroup", "iam:DeleteGroupPolicy" ] } ] } } ], "Path": "/" } } }, "Outputs": { "SailPointAWSRoleARN": { "Description": "SailPoint AWS Role ARN", "Value": { "Fn::GetAtt": [ "SailPointAWSRole", "Arn" ] } }, "SailPointAWSRoleExternalId": { "Description": "SailPoint AWS Role External ID", "Value": { "Ref": "ExternalId" } } } -
Enabling Data Collection
After the AWS roles are configured, you must take the final steps in your SailPoint tenant:
- First, enable inventory collection for all accounts.
- After that, you can choose to include activity data.
Verifying Your AWS Configuration
When you have finished connecting your AWS accounts, you must verify that the configuration was successful. To verify your configuration:
-
In the AWS Console IAM service, select Roles.
-
Search for the IAM role created by CloudFormation. Select the role and save its name and ARN. For example,
arn:aws:iam::xxxxxxxxxxxx:role/SailPointAWSRole -
Select the Trust Relationships tab and confirm the principal displays:
874540850173for Commercial accounts229634586956for GovCloud accounts -
Select Policies and search for the IAM role created by CloudFormation. For example,
SailPointAWSRole -
Select Permissions and verify the bucket name in the JSON.
-
Ensure the policy allows
s3:GetBucketLocationands3:ListBucketactions on the CloudTrail bucket, and thes3:GetObjectaction on the S3 bucket contents.
Viewing a Summary of the Details
- Go to CloudFormation > Stacks, and select the stack.
- Select the Parameters tab to view the key values for your configuration.
Screenshot
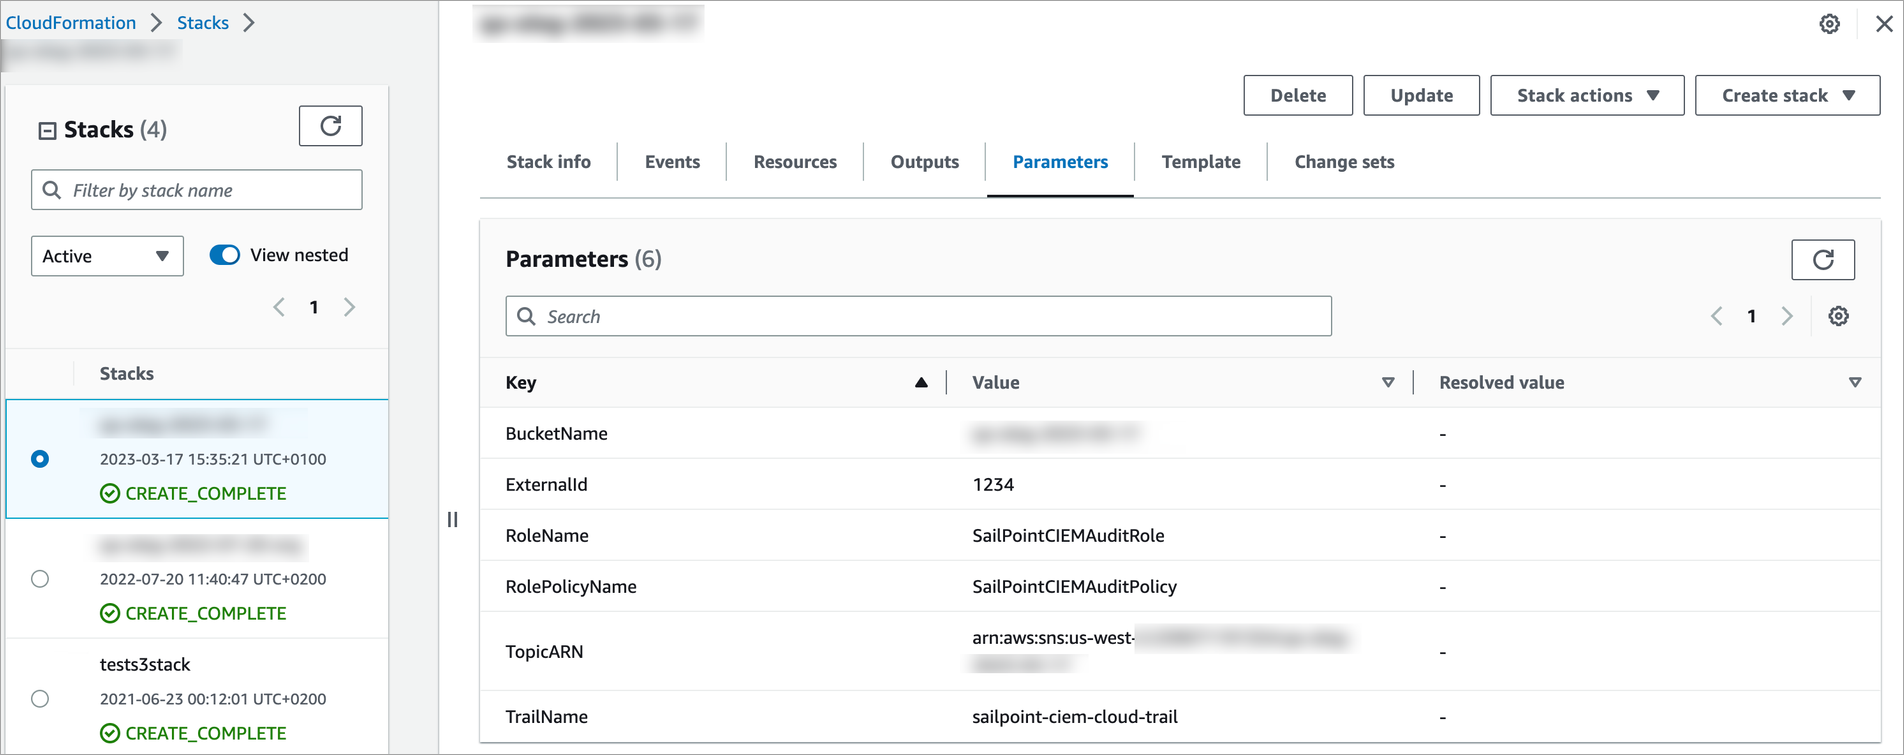
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.