Troubleshooting
If you encounter any of the following issues or errors, SailPoint recommends that you follow the guidance provided below to resolve the error before contacting SailPoint Support.
For issues or errors that are not addressed in this connector guide, refer to the following resources for troubleshooting information:
- SailPoint Identity Services Documentation
- SailPoint Support Knowledge Base
- SailPoint Developer Community
Debug Logs
For information about managing additional source settings, including debug logging and downloading connector logs, refer to Managing Additional Settings.
Cannot Set or Reset the Password for a Single Sign-On User
Issue: In select environments where SSO is enabled, sending email notification is not allowed for the users. So any user created in the create operation does not receive notification emails.
Resolution: In the Aggregation Settings tab in the connector source configuration enable the Disable User Creation Email Notification. For more information, refer to Aggregation Settings.
INSUFFICIENT_ACCESS: Portal User Email Settings Are Not Available
Issue: The partner user is not created with the default configuration when the Disable User Creation Email Notification option is unchecked.
Resolution:
- To create a partner user with enabled email notifications ensure that your community is Active and User's profile is selected in community administration.
- To activate the community, go to Setup > All Sites > Workspaces > Administration > Setting and then select Active. If no site exists, first create one.
- To select the community user profile, go to Setup > All Sites > Workspaces > Administration > Members and then select Profiles.
- Select Save.
Duplicate User Error Is Displayed
Issue: The email ID of that user may be utilized in the Salesforce system already.
Resolution: Create a new account with a different email ID. The Email ID is the mandatory username for the user.
Connector Fails to Create a New Account When the Total Active Account Limit in Salesforce Is Exceeded
Resolution: Increase the account limit in Salesforce or disable existing active accounts in Salesforce before initiating a Create request.
INVALID_SESSION_ID Session Error During Any Salesforce Connector Operation
Issue: INVALID_SESSION_ID
Resolution:
- Remove the
serverUrlandsessionIDattributes from the application configuration using the source update API. - Perform a test connection.
- If the test is successful retry the failed operation.
Errors During JWT Authentication Configuration
Before connecting to Salesforce using OAuth 2.0 JWT Flow, you need to create your own connected app required by JWT Flow on the Salesforce platform.
-
In Salesforce, go to Security Controls > Certificate and Key Management. Select Create Self-Signed Certificate to create a self-signed certificate. Then download the certificate to your local machine.
In this example, the certificate,
jwtapril.crt, was created and downloaded toC:\jwtapril.crtfor demonstration purposes. -
Select Export to Keystore to export your certificate to a keystore file in JKS (Java Keystore) format.
In this example, the certificate is exported to
D:\jwtapril.jks. Use this same location to export the certificate in JKS format. -
Go to Create > Apps, and select New in the connected apps area. Create a connected app that enables OAuth settings and which uses the digital certificate
C:\jwtapril.crtyou downloaded earlier and save it.Screenshots
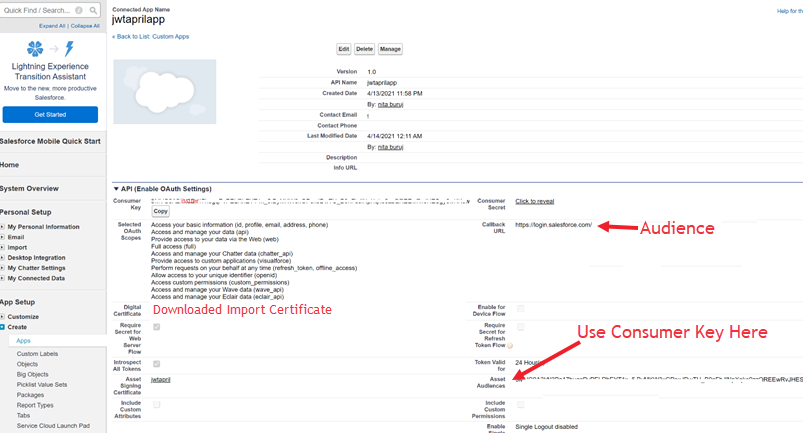
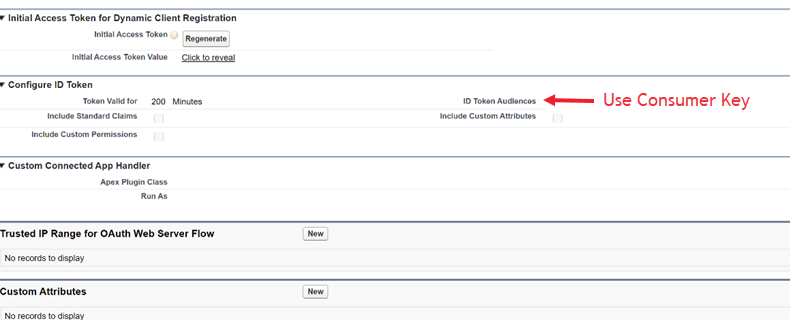
Now, go to Create > Apps and open the newly created connected app. You can find the following attributes in the connect app view:
subject- The username with which certificate is registeredaudience- The callback URL (provide:https://login.salesforce.com)issuer- The connected app's consumer key
-
Execute a keytool command to extract the private key from the Certificate:
A. List the contents of the keystore file from earlier. Check the certificate details with the alias name:
Raw query:
keytool -list -v -keystore keystoreName.jksQuery for this case:
keytool -list -v -keystore <jwtapril>.jksNote
In this case,
<jwtapril>is the alias name of the certificate from earlier.B. Convert the .jks file to a .p12 file by providing the certificate alias name from the keystore. In this example, it's
jwtapril.Raw query:
keytool -importkeystore -srckeystore <source keystore>.jks -srcstorepass <source keystore password> -srckeypass <source key password> -srcalias <source alias> -destalias <destination alias> -destkeystore <destination keystore>.p12 -deststoretype PKCS12 -deststorepass <destination keystore password> -destkeypass <destination key password>Query for this case:
keytool -importkeystore -srckeystore jwtapril.jks -srcstorepass jwtapril -srckeypass jwtapril -srcalias jwtapril -destalias jwtapril -destkeystore destination_keystore.p12 -deststoretype PKCS12 -deststorepass jwtapril -destkeypass jwtapril-srckeystore: location of source keystore file(.jks file)-srcstorepass: password of the keystore file-srckeypass : password of the keystore file-srcalias: alias of the keystore file-destalias: alias of the destination(.p12) file-destkeystore: location where you want to generate the .p12 file-deststorepass: password of the destination filedestkeypass:password of the destination keypassTip
Be sure to keep track of the passwords used in this query. Incorrect passwords may cause errors during private key generation.
Another example:
-> keytool -importkeystore -srckeystore C:\Certificates\Salesforce\00D3k000000usr9.jks -srcstorepass changeit -srckeypass changeit -srcalias jwt8mar -destalias jwt8mar -destkeystore C:\Certificates\Salesforce\pem8Mar.p12 -deststoretype PKCS12 -deststorepass changeit -destkeypass changeitC. Change the .p12 file into .pem format:
openssl pkcs12 -in destination_keystore.p12 -nodes -nocerts -out examplePem.pemNote
You may get an error message such as:
0C2F0000:error:0308010C:digital envelope routines:inner_evp_generic_fetch:unsupported:crypto\evp\evp_fetch.c:373:Global default library context, Algorithm (RC2-40-CBC : 0), Properties ()To work around this, do one of the following:
- Download the
opensslversion for your system from https://indy.fulgan.com/SSL/ - Try to change the node version.
D. Change the extension of the .pem file from ".pem" to ".key".
openssl rsa -in examplePem.key -outform PEM -out privatekey.keyFor example:
openssl rsa -in C:\Certificates\Salesforce1\examplePem.key -outform PEM -out C:\Certificates\Salesforce1\privatekey.keyThe generated private key (
privatekey.keyin the example) should be in RSA format.E. Open to validate the privatekey:
https://8gwifi.org/certsverify.jspInput x509, CSR, or PrivateKey:
put jwtapril.crt contentValidate against x509, CSR, or PrivateKey:
put privatekey.key contentprivatekey.keycontains the privatekey.Note
PrivateKeyPasswordcan be empty as it is not mandatory. - Download the
Note
During the test connection, you may get the following error message:
Unable to Authorize User: user is not admin approved to access this app
To work around this error, do the following:
- Go to Create > App and open your newly created connected app.
- Select Manage.
- Select Edit Policies.
-
In the OAuth Policies section:
A. Select Admin approved users are pre-authorized for Permitted Users, and select OK.
B. Select Save.
C. Select Manage Profiles and then Manage Permission Sets. Do one of the following:
-
Select the profiles and permission sets that are pre-authorized to use this connected app. You can create permission sets if necessary.
Now, the connected app provides access to users assigned with the selected profiles and permission sets. Assign the selected profiles or permission sets to the subject (username is used as the subject).
OR
-
Select All users may self-authorize. This authorizes all users.
-
Note
You may need to authorize a Salesforce user. Use the following Postman query to do so:
-
Import the following cURL request in Postman:
curl --location --request POST 'https://login.salesforce.com/services/oauth2/authorize' \ --header 'Content-Type: application/x-www-form-urlencoded' \ --header 'Cookie: BrowserId=ytV1qb2fEe2h2SmHOqTcbQ; CookieConsentPolicy=0:0; LSKey-c$CookieConsentPolicy=0:0' \ --data-urlencode 'client_id=3MVG9_XwsqeYoueJcfSbGhDFD45vg89rWLCiZ_yhv8WAQ3KFojhtBDz7qSDH37Kp7tbzEv8lRhg6LYk3ZtPu2b' \ --data-urlencode 'client_secret=FF2148B26AC19A1EC8800AA9EC63C8100XDF74C75F86AACF4173D6C355EA2A3A' \ --data-urlencode 'redirect_uri=https://login.salesforce.com/' \ --data-urlencode 'response_type=code -
Save the response of this query with a ".html" extension.
- Open the file and select it in order to validate. The file asks for you to provide a username and password. Provide the same username and password you used to create the certificate.
Unable to Find Valid Certification Path to Requested Target
Error Message: PKIX path building failed: sun.security.provider.certpath.SunCertPathBuilderException: unable to find valid certification path to requested target
Resolution:
- Check if the Profile associated with the Service account User have the
SystemAdminpermission. For more information, refer to [Required Permissions][required-permissions]. - Add the below entry key in the source xml file:
<entry key="OAuth2TokenURL" value="https://test.salesforce.com/services/oauth2/token"/>
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.