Integrating SailPoint with Microsoft Dynamics 365 CRM
Microsoft Dynamics CRM (Customer Relationship Management) is a customer relationship management software package developed by Microsoft focused on enhancing the customer relationship for any organization. Out of the box, the product focuses mainly on the Sales, Marketing, and Customer Service sectors.
CRM Online is a cloud-based offering of Microsoft Dynamics CRM where all the backend processes (such as application servers, setups, deployments, databases, licensing, and so on) are managed on Microsoft servers. It is a subscription-based offering which is preferred for organizations who may not want to manage all the technicalities involved in a CRM implementation.
Connecting SailPoint to your Dynamics 365 CRM allows you to manage identity and access management use cases related to read and provision various Dynamics 365 CRM Native IAM Objects as follows:
- Users: Licensed Users in Dynamics 365 CRM are synchronized from Entra ID. Other types of users such as Application Users and Stub Users can be created in CRM itself.
- Teams: Teams provide an easy way to share business objects and let you collaborate with other people across business units. While a team belongs to one business unit, it can include users from other business units. A user can be associated with more than one team.
- Security Roles: Security roles define access level on different records. These roles can be assigned to users or teams.
Note
To view the latest features, enhancements, and fixes for all SaaS connectors, refer to the SaaS Release Notes page.
Supported Features
The Microsoft Dynamics 365 CRM connector supports the following features:
- Account Management
- Account-Group Management
Account Management
The following table describes the supported operations on various objects for the Microsoft Dynamics 365 CRM connector:
| Operations | Licensed User | Application User | Stub User |
|---|---|---|---|
| Aggregation | Yes | Yes | Yes |
| Get Account | Yes | Yes | Yes |
| Enable/Disable Users | Yes | Yes | N/A |
| Add/Remove Entitlements - Add/Remove Access Teams - Add/Remove Owner Teams - Add/Remove Security Roles |
Yes | Yes | N/A |
Important
The Dynamics 365 Customer Relationship Management connector does not directly support Create users. Instead, licensed users are synchronized from the Entra ID source, so they must be created in that managed system, then imported into the Dynamics 365 Customer Relationship Management source.
Note
Licensed Users are synchronized from Entra ID.
Entitlement Management
| Operations | Owner Team | Access Team | Entra ID Office Group | Entra ID Security Group | Security Role |
|---|---|---|---|---|---|
| Aggregation | Yes | Yes | Yes | Yes | Yes |
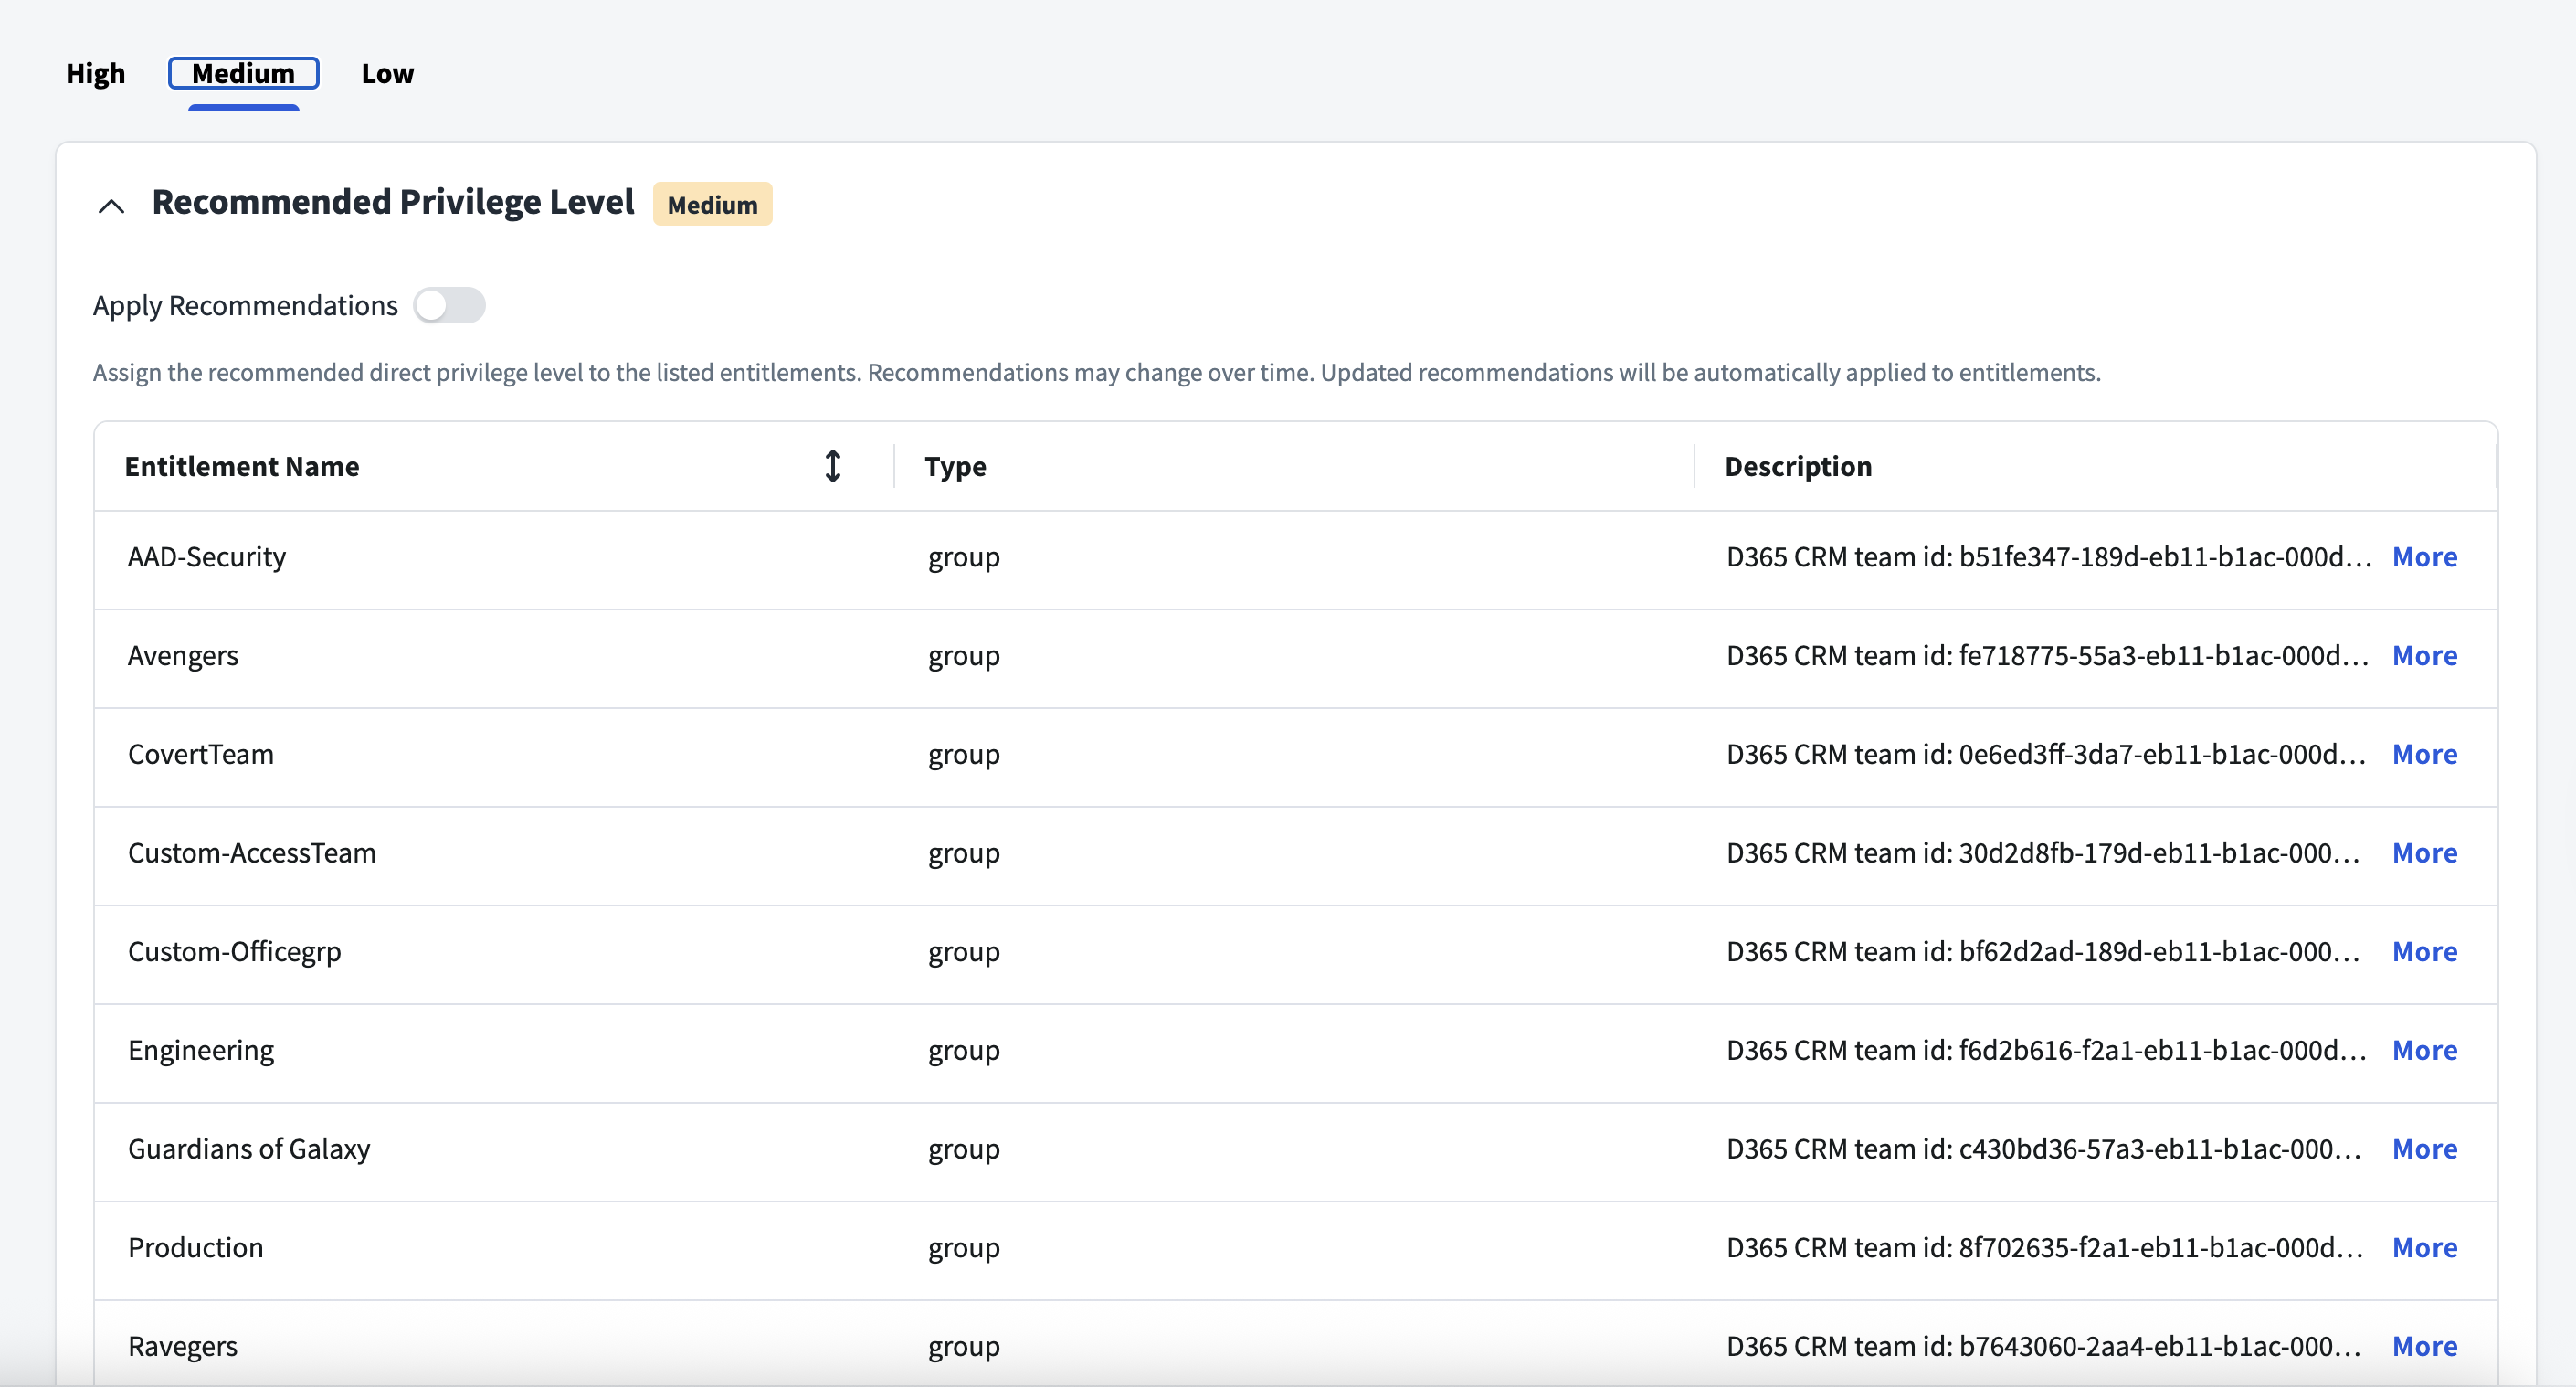
Privilege Classification
SailPoint Privilege Classification helps organizations systematically categorize and manage the privilege levels of entitlements within their sources. By classifying entitlements as high, medium, or low, administrators can better understand the potential risk and impact associated with specific access rights. This allows automatic assignment of privilege levels based on system recommendations, custom-defined criteria, or a same level across all entitlements.
| Privilege Level | Description |
|---|---|
| High | Administrative level access to accounts |
| Medium | Administrative level access for a specific role or function |
| Low | Only basic access of data |
Note
To manage Privilege Classification, users must have administrative roles such as Org Admin, Source Admin or Source Sub-Admin.
For more information, refer to Managing Privilege Classification.
Example
Prerequisites
- Configure at least one virtual appliance cluster and successfully test the connection. For more information, refer to the Virtual Appliance Reference Guide.
The Microsoft Dynamics 365 CRM connector supports OAuth 2.0 authentication with the following grant types:
- Client Credentials
- JWT Certificate Credentials
The following sections describe the configurations that must be performed for the above grant types.
Registering an Application on Entra ID
Registering the application generates the Tenant ID, Client ID, and Client Secret required for authentication. These are required for later processes.
Perform the following:
-
Use either of the following methods to access the Entra Management Portal to perform the configuration:
-
Select Entra ID in the left pane.
- Select App registrations.
- Select New registration.
- On the Register an application page, in the Name field, enter the name of the application that you want to set up.
- Select Register. An Application is created. On the Application page the Application ID (Client ID) and Tenant ID are displayed.
- On the left-hand panel, select Certificates & secrets. On the Certificates & secrets page, in the Client secrets section, select New client secret.
- On the Add a client secret page, enter the Description to generate a secret, and select the validity duration in the Expires list. Select Add.
- Note the value of the client secret that you have just created.
Client Credentials
For the default Client Credentials grant type based authentication, following are the required configurations:
- Obtain the Tenant ID, Client ID, and Client Secret from Entra ID by registering the application (steps mentioned in Registering an Application on Entra ID).
JWT Certificate Credentials
JWT Certificate Credentials supports Authentication based on JWT assertion prepared from Certificate and Private Key.
- Obtain the Tenant ID and Client ID from Entra ID by registering the application (up to step 6 mentioned in Registering an Application on Entra ID).
-
To create a self-signed or CA-signed type X.509 certificate and private key, perform the following steps to register the certificate with the Microsoft identity platform:
Important
The private key must be encrypted with the RSA algorithm and registered at the Entra portal.
- Log in to the Entra Portal.
- Select the client application. In the Entra app registration for the client application, select Certificates & secrets.
- Select Upload certificate and select the certificate file to upload.
- Select Add.
-
Obtain values for the following configurations:
- Certificate: Obtain the text file of the same certificate which was uploaded on the Entra portal.
- Private Key: Obtain the private key text file.
- Private Key Password
Creating an Application User on CRM
Perform the following:
- Open the Dynamics 365 CRM portal.
- Select Settings on top right and go to Advanced Settings. A new tab opens.
- Go to Settings on the new tab, then go to the Security option under System.
- In Features, select Users. From the dropdown menu select Application Users and then select New. A form to create a new user opens.
- Select the user type as Application User again and provide User Name and Application ID. The Application ID is the Client ID of the Application registered in Entra ID previously.
- Save the form.
Required Permissions
Assign one of the following security roles to the application user based on the operation to be performed:
- Custom Security Role
- System Administrator (built-in)
Custom Security Role
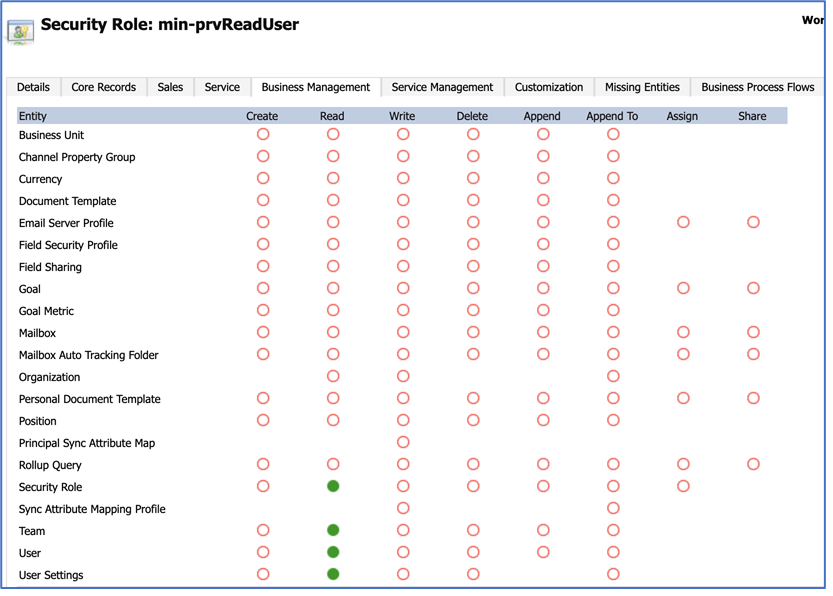
A Custom Security Role must be created with minimum read privileges (as shown in the following figure) for the following purposes:
- Account Aggregation of Users
- Get Object for Users, Security Roles, and Teams
- Group Aggregation for Roles and Teams
In the Business Management section (as shown in the following figure), for the following entities, select the Read option:
- Security Role
- Team
- User
- User Settings
System Administrator
Assign the System Administrator (built-in) security role for the following purposes:
- Add Security Roles and Teams to Users
- Remove Security Roles and Teams from Users
- Enable/Disable Users
Note
All connector operations can be managed with the System Administrator role.
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.