Connecting SailPoint with Top Secret (Read-only)
To connect SailPoint with Top Secret, perform the following tasks:
Adding the Source in SailPoint
To connect to SailPoint, perform the following steps. Once the connection is made, you can configure it to meet your company's needs.
- Sign in to SailPoint.
- Go to Admin > Connections > Sources.
- Select Create New.
- Search for the connector by entering the name in the search box, and then select Configure.
- In the Source Name field, enter a unique and descriptive name for your source. Source names cannot exceed 128 characters.
- In the Description field, provide additional details about the source to help distinguish it from similar sources. This field allows a maximum of 2,000 characters.
- In the Source Owner field, begin typing the name of an owner. Matches appear after you type two or more letters. For more information, refer to Assigning a Source Owner.
-
Under Connection Type, select Direct Connection or Flat File.
- Direct Connection - A direct connection fetches data from the Virtual Appliance Cluster you choose as the application connector for the source. A direct connection configuration allows for real-time updates. For more information about configuring and deploying virtual appliances, refer to the Virtual Appliance Reference Guide.
- Flat File - Select the flat file if no connector is available, or if another system restricts the connection. This option allows only reading and aggregating data as a generic/delimited application. Provisioning activity is unsupported, and additional configuration pages like connection settings and aggregation settings are unavailable.
-
If you selected Direct Connection, in Virtual Appliance Cluster, select the virtual appliance cluster that will be used as the application connector for the source.
- (Optional) Select a governance group to grant its members source or role sub-admin level oversight of the source and its access. For more information, refer to Creating and Managing Governance Groups.
- If this source represents a primary system containing your organization's personnel records, select the Authoritative Source checkbox. For more information, refer to Creating Identity Profiles.
- Select Continue. The source is created, and you are navigated to the Source Setup > Base Configuration page. Continue to configure your connected source there.
Base Configuration
Provide the base configuration parameters. Information you entered in the Create New Source dialog is automatically entered into the fields in the Base Configuration page. You can edit this information if necessary.
- Enter a unique name and description for the source.
-
In the Source Owner dropdown list, select the identity that owns this source.
- To find a source owner, begin entering their name.
-
In the Virtual Appliance Cluster dropdown list, select the virtual appliance to use when communicating with your organization's systems. For more information, refer to SailPoint Virtual Appliances.
-
(Optional) If enabled for your organization, select the Use a Credential Provider checkbox to manage the source's authentication using a credential provider.
Note
To add a credential provider, go to Admin > Connections > Credential Providers. For more information about credential providers, refer to Credential Providers.
-
(Optional) In the Governance Group for Source Management dropdown list, select a governance group to associate with this source. For more information about governance groups, refer to Associating Governance Groups with a Source.
-
(Optional) Select Create Manual Work Items to allow the connector to create manual work items for certain operations. You can also enable this option so the source supports additional source management features such as creating accounts and access profile management.
Important
Once you enable this feature, you cannot disable it.
For more information on manual work items in SailPoint, refer to Work Items. For more information on SailPoint features, refer to SailPoint Identity Services.
-
Select Save.
Uploading the Top Secret File
Upload the file generated by the TSSCFILE utility, and make sure it has a .csv extension. Drag and drop the .csv file or select Upload Files from your computer.
The following examples illustrate TSSCFILE export commands:
| Command | Purpose |
|---|---|
TSS LIST(STC) DATA(ALL) |
Displays the STC record, including procedure names mapped to ACIDs and STC-related attributes. |
TSS LIST(ACIDS) TYPE(USER) DATA(ALL) |
Display a complete view of user ACIDs including name, type, facilities, department/division/zone, and other attributes. |
TSS LIST(ACIDS) TYPE(SCA) DATA(ALL) |
Display detailed Security Control ACID information, including global scope and specific administrative authorities. For example ACID, DATA, RESOURCE, FACILITY, MISC1-MISC9, SCOPE |
TSS LIST(ACIDS) TYPE(ZCA) DATA(ALL) |
Lists Zone Control ACIDs, including administrators for specific zones and their authority to manage the divisions and departments within each zone. |
TSS LIST(ACIDS) TYPE(VCA) DATA(ALL) |
Lists Division Control ACIDs, including administrators for divisions and their authority to create or delete departments and manage resources within each division. |
TSS LIST(ACIDS) TYPE(DCA) DATA(ALL) |
Lists Department Control ACIDs, including department-level administrators and their authority to manage users and profiles within each department. |
TSS LIST(ACIDS) TYPE(ZONE) DATA(ALL) |
Displays Zone definitions, including creation and modification of dates and the list of divisions associated with each zone. |
TSS LIST(ACIDS) TYPE(DIVISION) DATA(ALL) |
Displays Division definitions, including parent zone and the list of all departments in each division. |
TSS LIST(ACIDS) TYPE(DEPARTMENT) DATA(ALL) |
Displays Department definitions, including the parent division and the list of users and profiles owned by each department. |
TSS LIST(ACIDS) TYPE(PROFILE) DATA(ALL) |
Displays profile (security template) details, including resource permission and the list of all the users associated with each profile. |
TSS LIST(ACIDS) TYPE(GROUP) DATA(ALL) |
Displays Group ACID definitions and the members associated with each group. |
Additional Settings
Screenshot
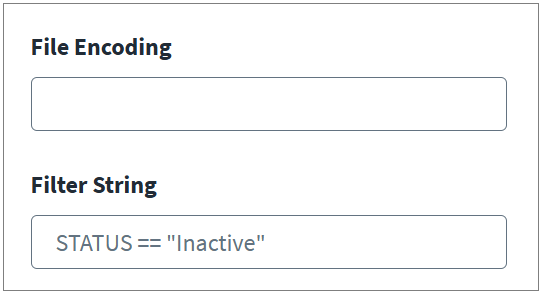
- Specify the File Encoding to be used by the connector. Valid values for this attribute can be found at Character Sets on the Internet Assigned Numbers Authority (IANA) website. If this field is empty, the default encoding (the value of file.encoding specified by the jvm) is used.
- Enter the Filter String to exclude matching strings from the dataset.
- Select Save.
Review and Test
Perform a test to confirm the connection to SailPoint.
- Go to Review and Test.
-
Confirm that the entries in each field are correct.
If you note any mistakes, return to the section and make corrections.
-
Select Test Connection.
SailPoint Application Onboarding
SailPoint application onboarding enables you to easily onboard new applications and create sources following the successful onboarding of a discovery source. To use this feature, continue to Discovered Applications in the SailPoint user interface.
For more information, refer to Application Onboarding in the SailPoint SaaS documentation.
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.