Connecting SailPoint and Identity Security Cloud Governance SaaS
To connect SailPoint with Identity Security Cloud Governance, perform the following tasks:
Adding the Source in SailPoint
To connect to SailPoint, perform the following steps. Once the connection is made, you can configure it to meet your company's needs.
Important
By default, the provisioning feature is disabled, and the connector only supports read-only operations. To support provisioning operations, you must manually enable the feature in the source configuration.
To configure a new source:
- Sign in to SailPoint.
- Go to Admin > Connections > Sources.
- Select Create New.
- Search for the connector by entering the name in the search box, and then select Configure.
- In the Source Name field, enter a unique and descriptive name for your source. Source names cannot exceed 128 characters.
- In the Description field, provide additional details about the source to help distinguish it from similar sources. This field allows a maximum of 2,000 characters.
- In the Source Owner field, begin typing the name of an owner. Matches appear after you type two or more letters. For more information, refer to Assigning a Source Owner.
- (Optional) Select a governance group to grant its members source or role sub-admin level oversight of the source and its access. For more information, refer to Creating and Managing Governance Groups.
- If this source represents a primary system containing your organization's personnel records, select the Authoritative Source checkbox. For more information, refer to Creating Identity Profiles.
- Select Continue. The source is created, and you are navigated to the Source Setup > Base Configuration page. Continue to configure your connected source there.
Connection Settings
The following information is required for SailPoint to connect and interact with Identity Security Cloud Governance.
Screenshot
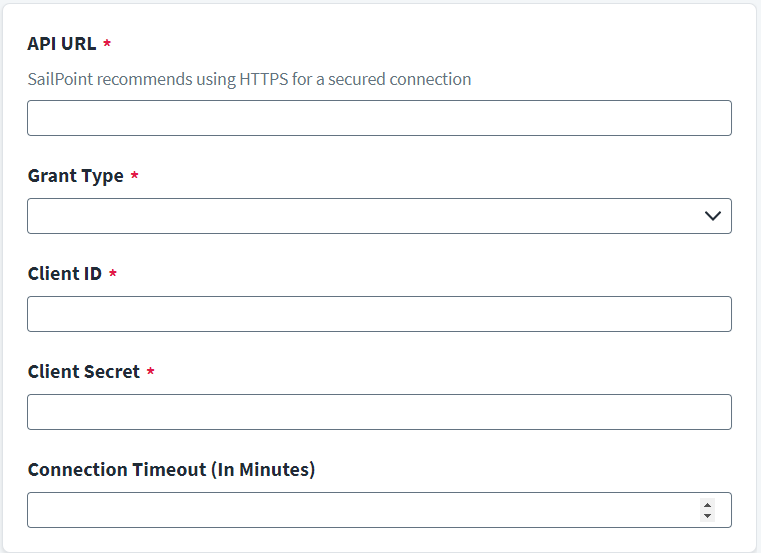
- Enter the API URL path used to connect to the target tenant.
- Select the Grant Type as Client Credentials.
- Enter the Client ID of the managed system.
- Enter the Client Secret of the managed system.
- Enter the time span in Connection Timeout after which an aggregation operation terminates.
- Select Save.
Aggregation Settings
This section provides the details required for aggregating the user accounts.
For more information about aggregation, refer to Loading Account Data.
Screenshot
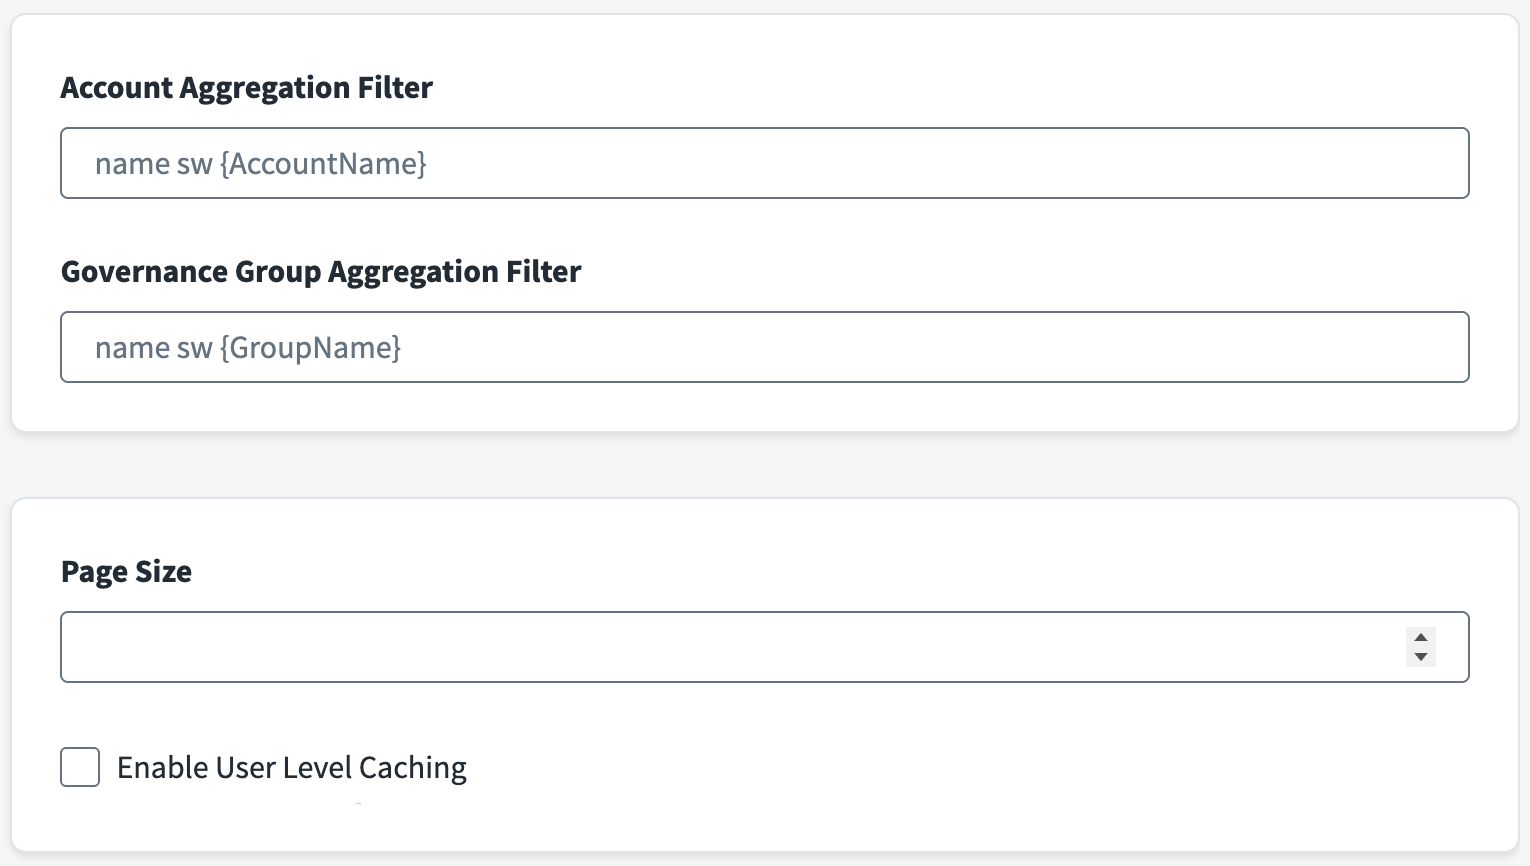
- Go to Aggregation Settings > Filter Settings.
- Enter the appropriate Account Aggregation Filter. For more information, refer to Account Aggregation Filter.
- Enter the appropriate Governance Group Aggregation Filter. For more information, refer to Governance Group Aggregation Filter.
- Enter the number of records in Page Size to aggregate in a single page when iterating over large datasets. You can set it from 1 to 250. The default is 200.
-
Select Enable User Level Caching to create cache objects of user levels for faster access during account aggregation.
Note
During update, it may create additional cache, which can affect aggregation and get object operation.
-
Select Save.
Note
If no filters are applied, the system will fetch all available data.
Account Aggregation Filter
Following operators and attributes are supported.
| Attribute | Operator |
|---|---|
| id | eq, in |
| Name | eq, sw |
| eq, sw | |
| First Name | eq, sw |
| Last Name | eq, sw |
For example, to filter account names starting with ISCUser, use name sw "ISCUser".
Governance Group Aggregation Filter
Following operators and attributes are supported.
| Attribute | Operator |
|---|---|
| id | eq, in |
| Name | eq, sw |
For example, to filter Governance Groups with names starting with "ISCGroup," use name sw "ISCGroup".
Reassignment Settings
Screenshot
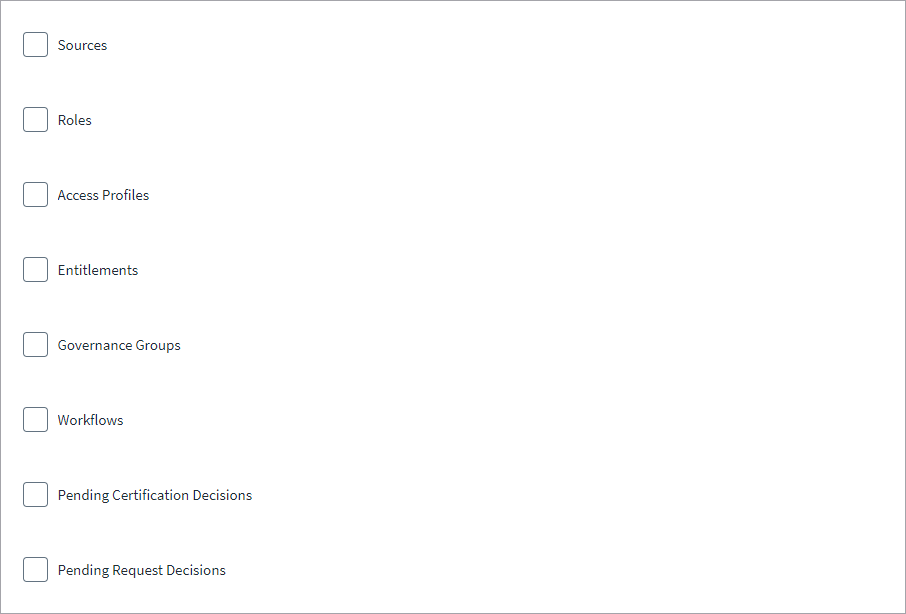
-
Select the Objects and Tasks owned by a user to reassign to their Identity Manager after the governance account user is disabled. Your selections apply to all objects and tasks of that type.
Note
The Pending Request Decisions checkbox reassigns access request decisions (approvals) only if the disabled user is also the owner of an access item, such as an access profile.
-
Select Save.
Note
To ensure the effective functioning of reassignment, it is essential for the identities to have a direct line manager. Without this, the objects and tasks cannot be reassigned.
Review and Test
Perform a test to confirm the connection to SailPoint.
- Go to Review and Test.
-
Confirm that the entries in each field are correct.
If you note any mistakes, return to the section and make corrections.
-
Select Test Connection.
SailPoint Application Onboarding
SailPoint application onboarding enables you to easily onboard new applications and create sources following the successful onboarding of a discovery source. To use this feature, continue to Discovered Applications in the SailPoint user interface.
For more information, refer to Application Onboarding in the SailPoint SaaS documentation.
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.