Integrating SailPoint with CrowdStrike
CrowdStrike is a SaaS connector that aggregates Risk information for identities from your CrowdStrike module.
This document is designed to give specific information about the requirements and fields needed to successfully configure an instance of the CrowdStrike connector.
Note
To view the latest features, enhancements, and fixes for all SaaS connectors, refer to the SaaS Release Notes page.
Supported Features
The CrowdStrike connector supports the following features:
- Aggregation of Accounts
- Single Account Aggregation
-
Identity Protection - Risky User Alert Feature
- Assess compromised account risk from CrowdStrike security reports. The connector aggregates
riskScore,riskScoreSeverity, andriskFactors.
- Assess compromised account risk from CrowdStrike security reports. The connector aggregates
-
Device Enrichment and NHI Mapping
- Map non-human identities to endpoints using hostname, computer name, last login user, OS version, and external IP.
-
Inventorying MCPs and AI Agents
- Discover AI client processes and MCP server configurations from endpoint telemetry.
-
Active Directory Users (NHIs) Management
- Aggregate Active Directory non-human identities from Identity Protection. Identify programmatic accounts with
isHumanandisProgrammatic.
- Aggregate Active Directory non-human identities from Identity Protection. Identify programmatic accounts with
-
Real-Time Response and Incident Data Ingestion
- Ingest real-time response and incident data to support AI agent discovery and security analysis.
Non-Human Identity Discovery
- Aggregate CrowdStrike EDR process agents
- Aggregate CrowdStrike EDR MCP config agents
Refer to Dataset Management for more information.
Refer to Discovering Potential Non-Human Accounts for more information.
Prerequisites
The following prerequisites are required:
- An API Client must be configured in CrowdStrike. This API client must be configured with specific Identity Scopes outlined in Required Permissions.
- You need the CrowdStrike Cloud Environment URL of the CrowdStrike service.
- To connect with the CrowdStrike API you will need to get an OAuth Client ID and Client Secret. These will be used to identify and authenticate your application. For more information on generating the client ID and client secret, refer to the CrowdStrike OAuth documentation (the CrowdStrike documentation requires an active login).
Required Permissions
The following scopes need to be applied to the API client created in CrowdStrike:
Important
To use any of the Identity Protection API functionality, you must enable the Identity Protection GraphQL write scope.
| Scope | Read | Write | Required for |
|---|---|---|---|
| Hosts | Yes | No | All features |
| Real Time Response | Yes | No | AI agents |
| NGSIEM | Yes | Yes | AI agents |
| Identity Protection Assessment | Yes | No | Identity Protection |
| Identity Protection Automation | Yes | No | Identity Protection |
| Identity Protection Detections | Yes | No | Active Directory NHIs |
| Identity Protection Enforcement | Yes | No | Identity Protection |
| Identity Protection Entities | Yes | No | Active Directory NHIs |
| Identity Protection GraphQL | Yes | Yes | Active Directory NHIs |
| Identity Protection Health | Yes | No | Identity Protection |
| Identity Protection On-premise Enablement | Yes | No | Identity Protection |
| Identity Protection Timeline | Yes | No | Active Directory NHIs |
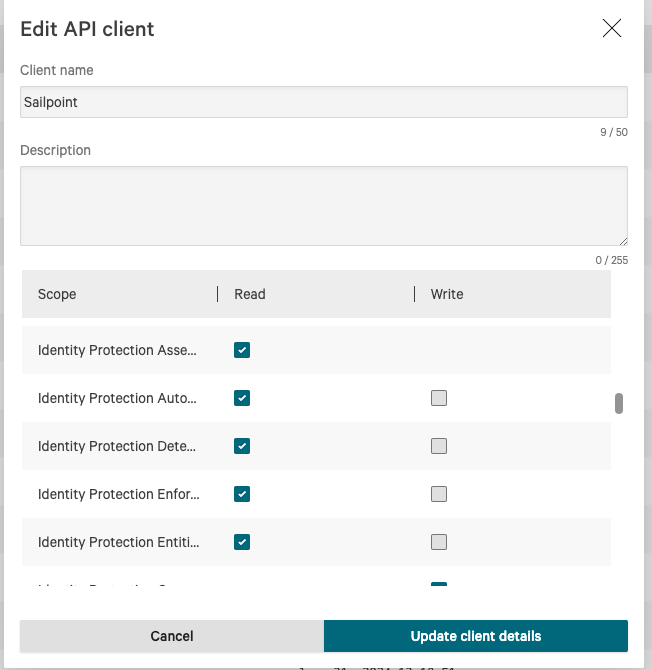
For example, your permissions may look like the following:
Screenshot
Documentation Feedback
Feedback is provided as an informational resource only and does not form part of SailPoint’s official product documentation. SailPoint does not warrant or make any guarantees about the feedback (including without limitation as to its accuracy, relevance, or reliability). All feedback is subject to the terms set forth at https://developer.sailpoint.com/discuss/tos.