Microsoft Copilot Studio Agents Management
Microsoft Copilot Studio Agents are part of the Microsoft Power Platform ecosystem, rather than standalone Azure resources. They operate across three integrated layers:
-
Experience Layer (Copilot Studio): Where the agent is designed and managed.
-
Data Layer (Dataverse): Where the agent's configuration and metadata are stored.
-
Identity Layer (Azure AD/Entra ID): Where the agent's identity is managed for secure authentication and service access.
Every Copilot belongs to a Power Platform environment. The environment determines where to store the agent and which Dataverse database belongs to that environment.
Important
Your organization must have SailPoint Agentic Fabric to use this feature. Contact your Customer Success team for more information. For more information, refer to SailPoint Agentic Fabric.
Supported Features
-
Aggregation of Microsoft Copilot Studio agents
-
Activate and deactivate Microsoft Copilot Studio agents
Prerequisites
Make sure the service principal configured on the SailPoint platform for Microsoft Entra ID SaaS connector is added as an application user in every Power Platform environment where you want to manage Microsoft Copilot Studio agents.
Steps to add the service principal as an application user Power Platform Admin Center:
-
Sign in to the Power Platform Admin Center.
-
Go to Manage.
-
Select the environment.
-
Go to Settings > Users + permissions > Application users.
-
Select New app user > Add an app.
-
Select the service principal used by the Entra ID SaaS connector, then select Add.
Required Permissions
Copilot agents reside within Power Platform environments, and their metadata is stored in Dataverse. Consequently, your user account must have specific permissions within the Power Platform Admin Center to view or manage these agents.
Required Security Roles
|
PI / Role |
Permission / Role Name |
Type |
Description / Purpose |
|---|---|---|---|
|
Security Role |
Global Discovery Service Role |
Role-based |
Lets the app call the Global Discovery API and get the list of instances. |
|
Custom Security Role |
BotReader (custom role: Read = Organization on bot + botcomponent) |
Role-based |
Lets the app call the bots API and read agent metadata and components. |
Required Dataverse Privileges
To activate or deactivate Copilot Studio agents, the SailPoint application user in Power Platform requires the Write privilege on the Bot (Agent) and Bot Component tables in Dataverse, in addition to the read privileges required for aggregation.
|
Privilege |
Dataverse Table |
Level |
Required For |
|---|---|---|---|
|
Read ( |
Bot / Agent |
Organization |
Aggregation (read agents) |
|
Write ( |
Bot / Agent |
Organization |
Activate and deactivate agents |
|
Read ( |
Bot Component |
Organization |
Aggregation (read components) |
|
Write ( |
Bot Component |
Organization |
Enable and disable agents |
Steps to configure these privileges in the Power Platform Admin Center:
-
Sign in to the Power Platform Admin Center.
-
Select your environment and go to Settings > Users + Permissions > Security Roles.
-
Open the BotReader security role assigned to the SailPoint application user. If this role doesn't exist, create it.
-
On the Custom Tables tab, find the Agent (
bot) and Agent Component (botcomponent) tables. -
Set the Write column to Organization level for both tables.
-
Select Save.
-
Go to Application Users, select the SailPoint app, select Manage Security Roles, and confirm the updated role is assigned.
Enabling Machine Identity Governance
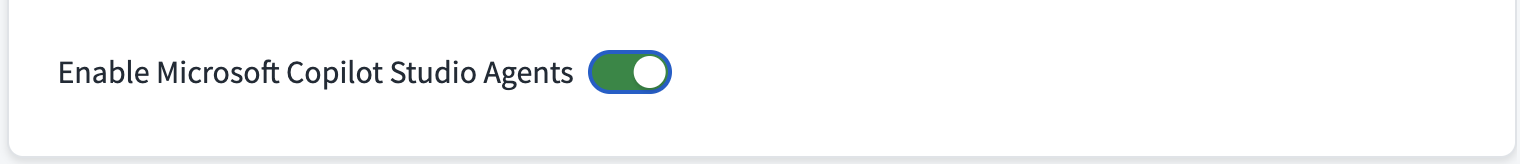
To enable Copilot Studio agents aggregation, follow these steps:
 Screenshot
-
Go to Microsoft Entra SaaS source configuration page within ISC.
-
Select Machine Identity Governance Settings tab.
-
Select Enable Microsoft Copilot Studio Agents. This enables Copilot agent aggregation in your environment.
-
Select Save.
Supported Resources
For more information, refer to Microsoft Copilot Studio Resources.